> This is part 1 of 2 of the full documentation (pages 1–100 of 150).
> The content is paginated: fetch every part to see all of it.
> Next part: https://docs.inopli.com/llms-full.txt/1
> Page index: https://docs.inopli.com/llms.txt

# Understanding Inopli

Inopli represents the <mark style="color:green;">forefront</mark> in security incident management platforms, integrating <mark style="color:green;">efficiency</mark> and <mark style="color:green;">cutting-edge</mark> technology into a unique <mark style="color:green;">centralized</mark> system. Meticulously designed, the Inopli solution <mark style="color:green;">transforms</mark> the monitoring and administration of alerts and incidents, providing a comprehensive and detailed perspective of security vulnerabilities. This platform is an <mark style="color:green;">ally</mark> for organizations of any scale, maximizing <mark style="color:green;">productivity</mark> and reducing operational costs.

Inopli alert management engine was specifically created to enhance the <mark style="color:green;">accuracy</mark> of manual work. It acts as an advanced filter, drastically reducing the incidence of false-positive alerts, an innovation that not only boosts the <mark style="color:green;">efficiency</mark> of security teams but also <mark style="color:green;">optimizes</mark> resources, resulting in a substantial <mark style="color:green;">reduction of operational costs</mark>.

{% embed url="<https://youtu.be/s-h-21u1quU>" %}
Inopli Solution
{% endembed %}

***


# First Access

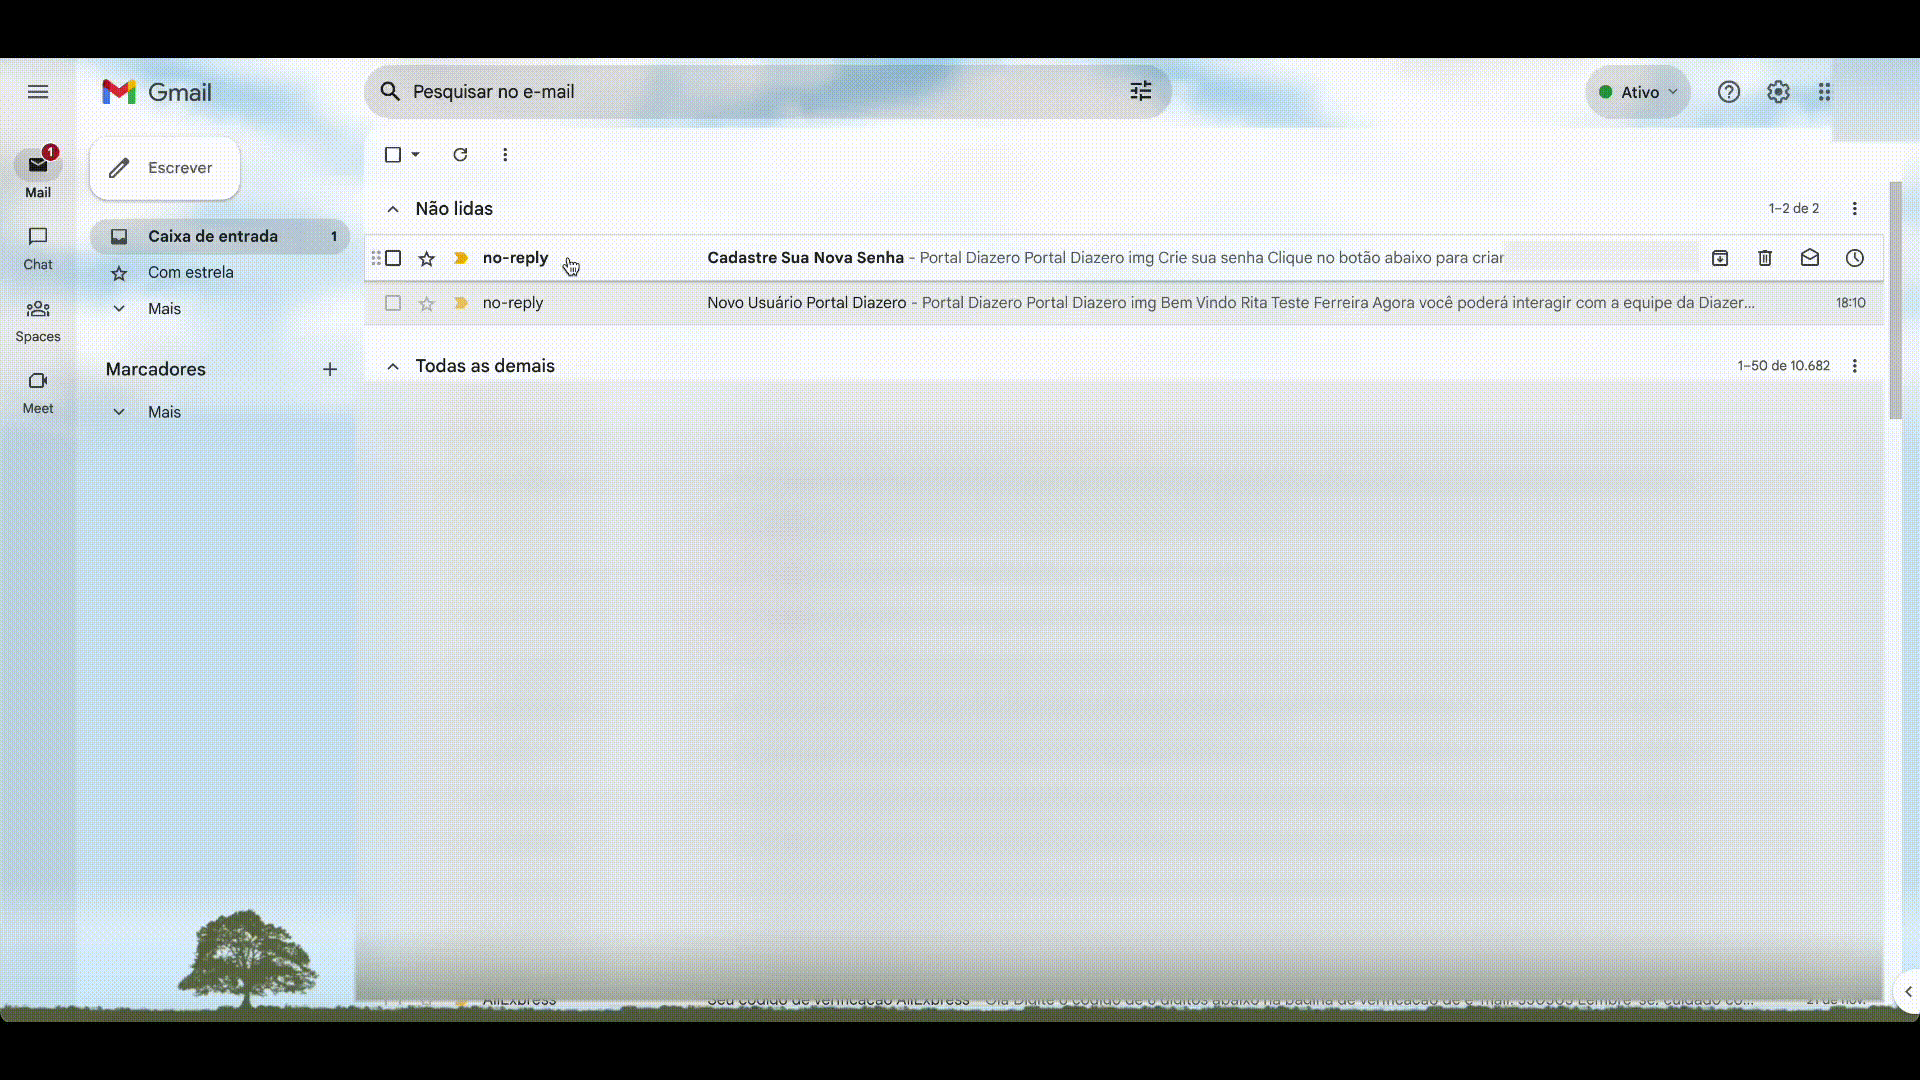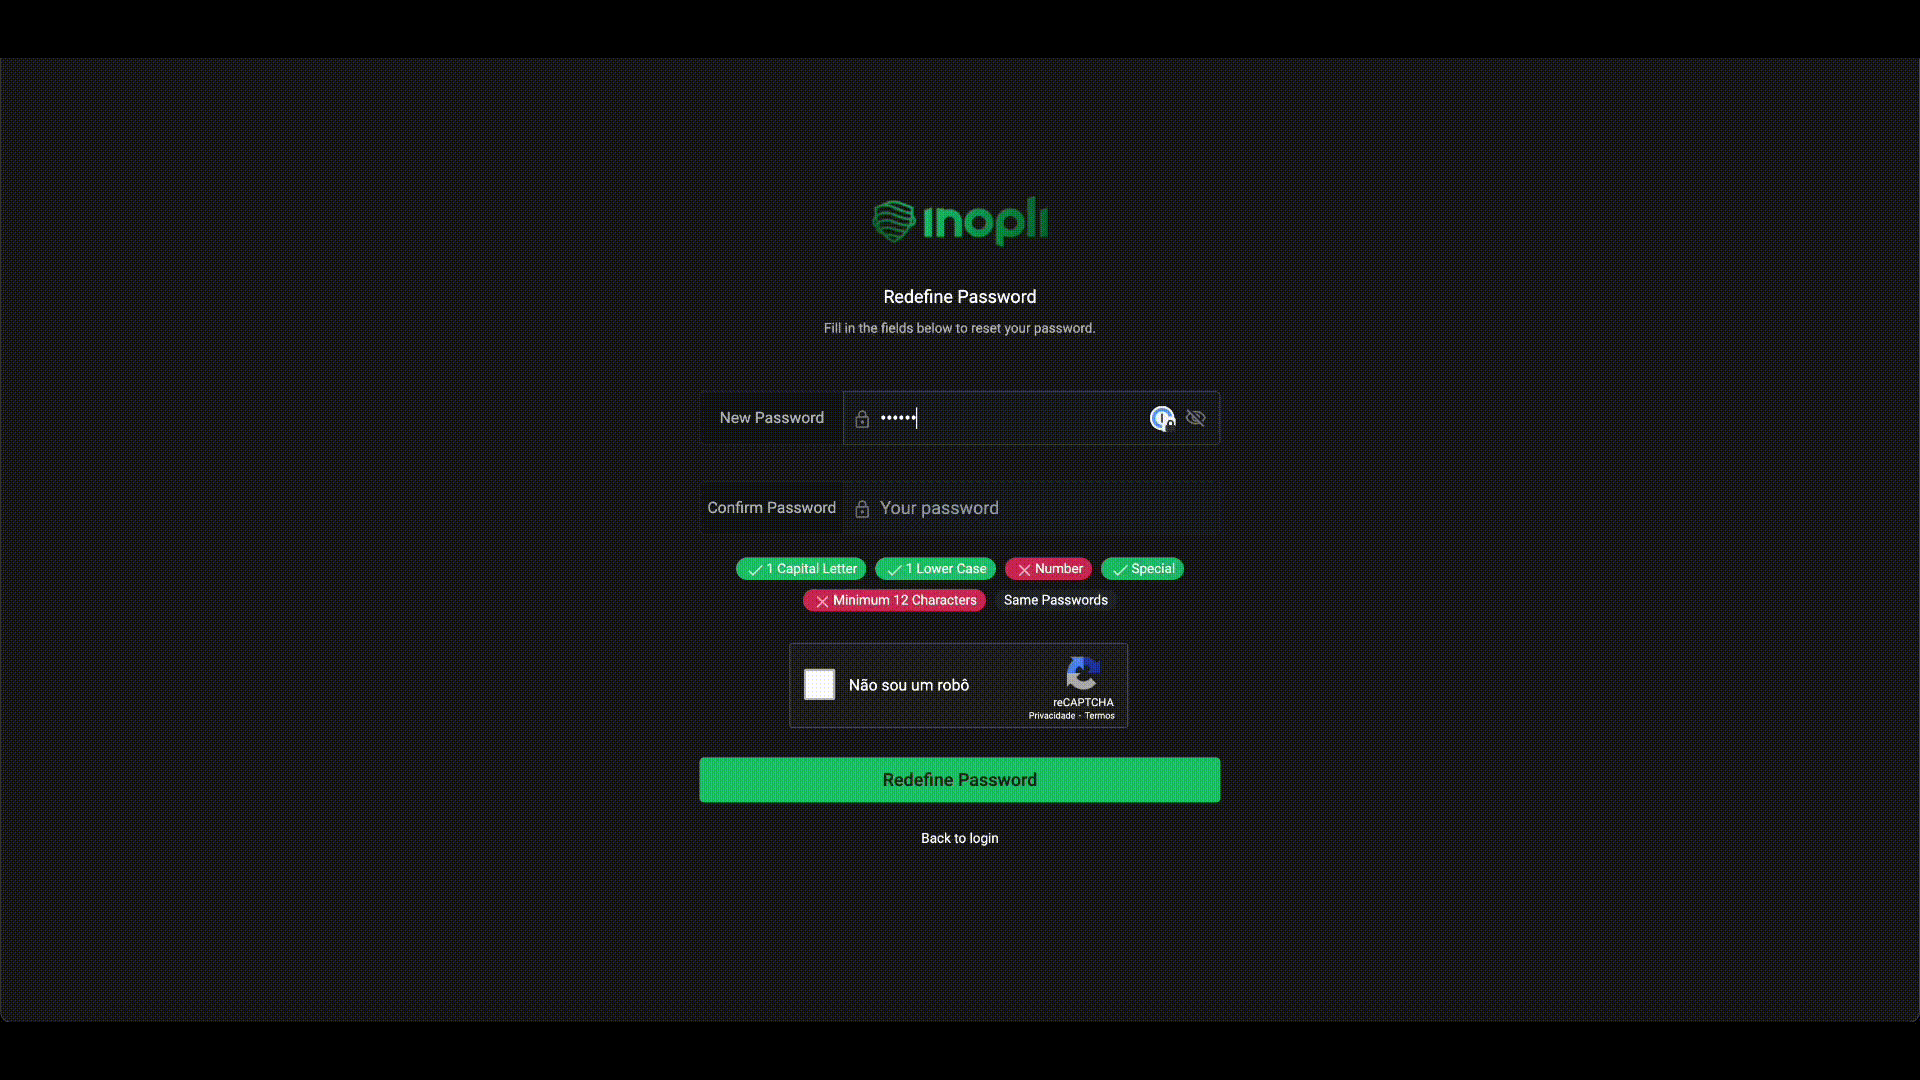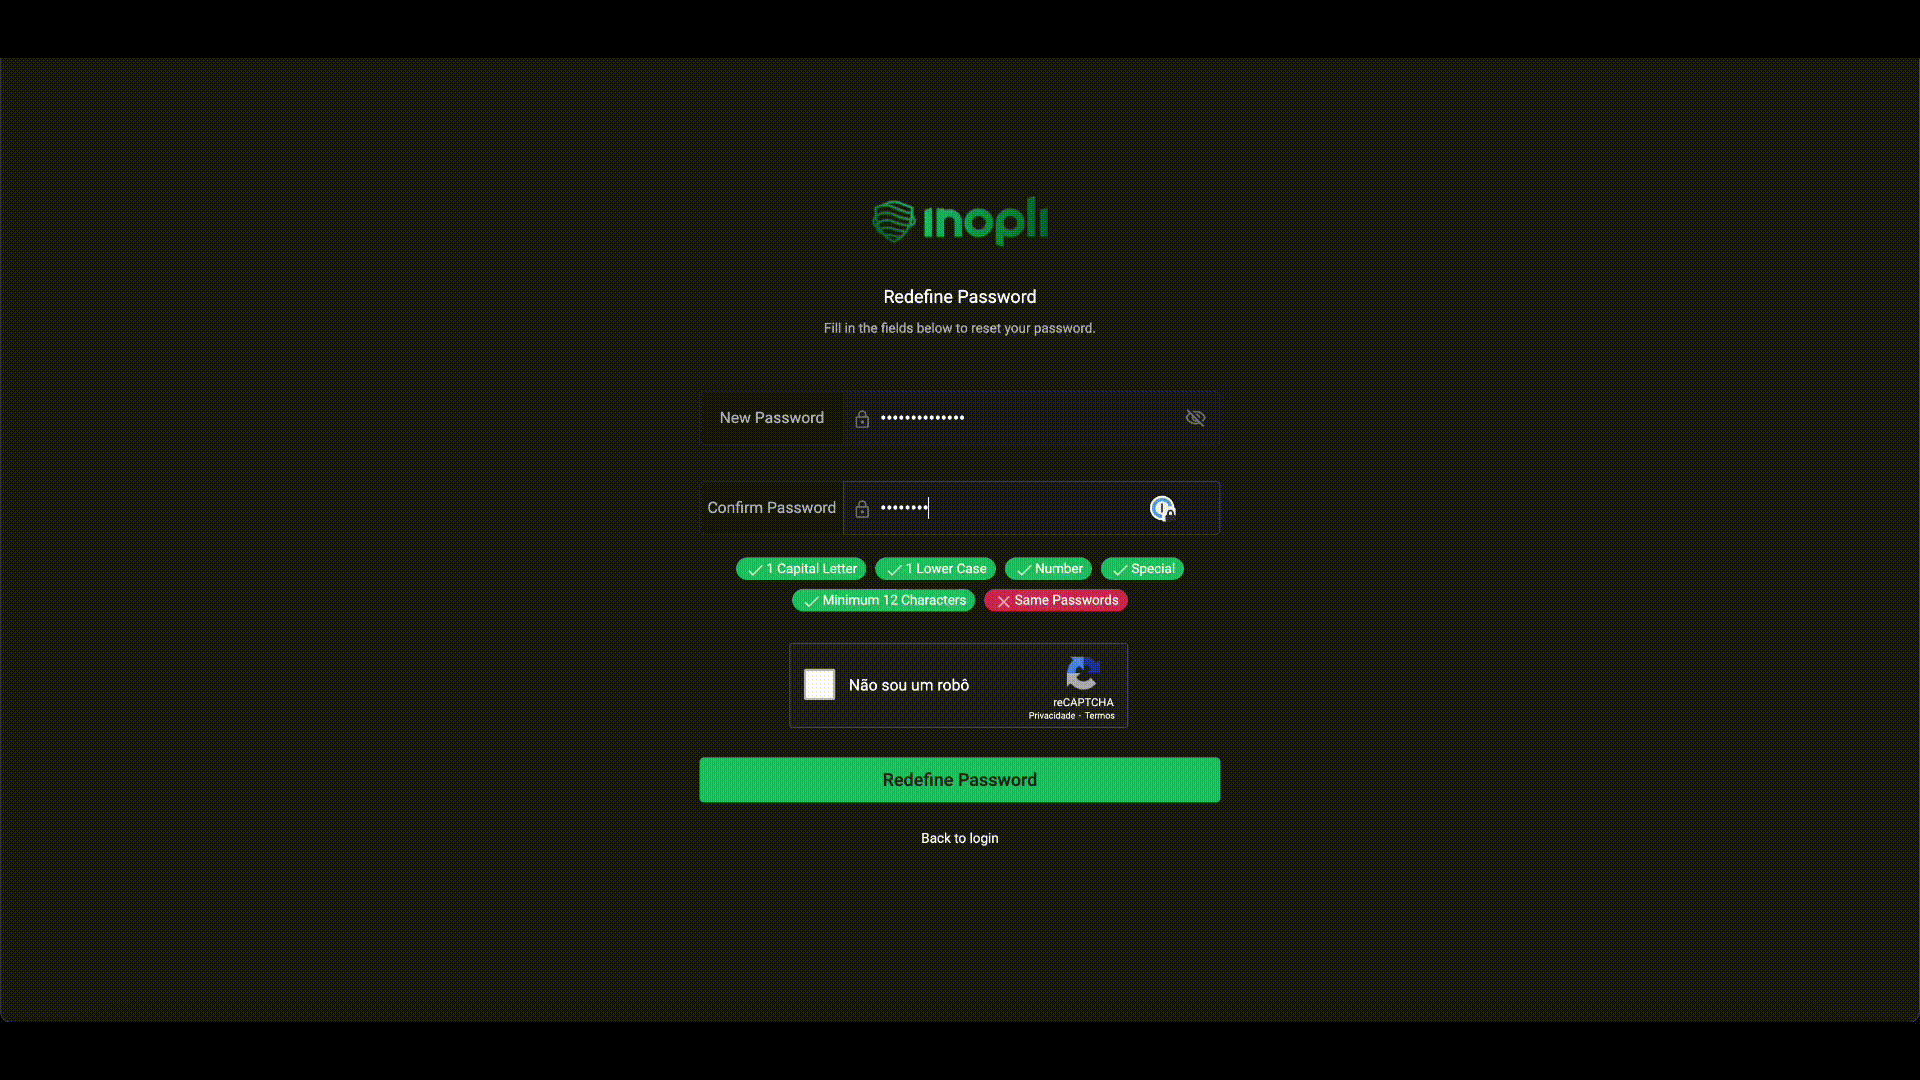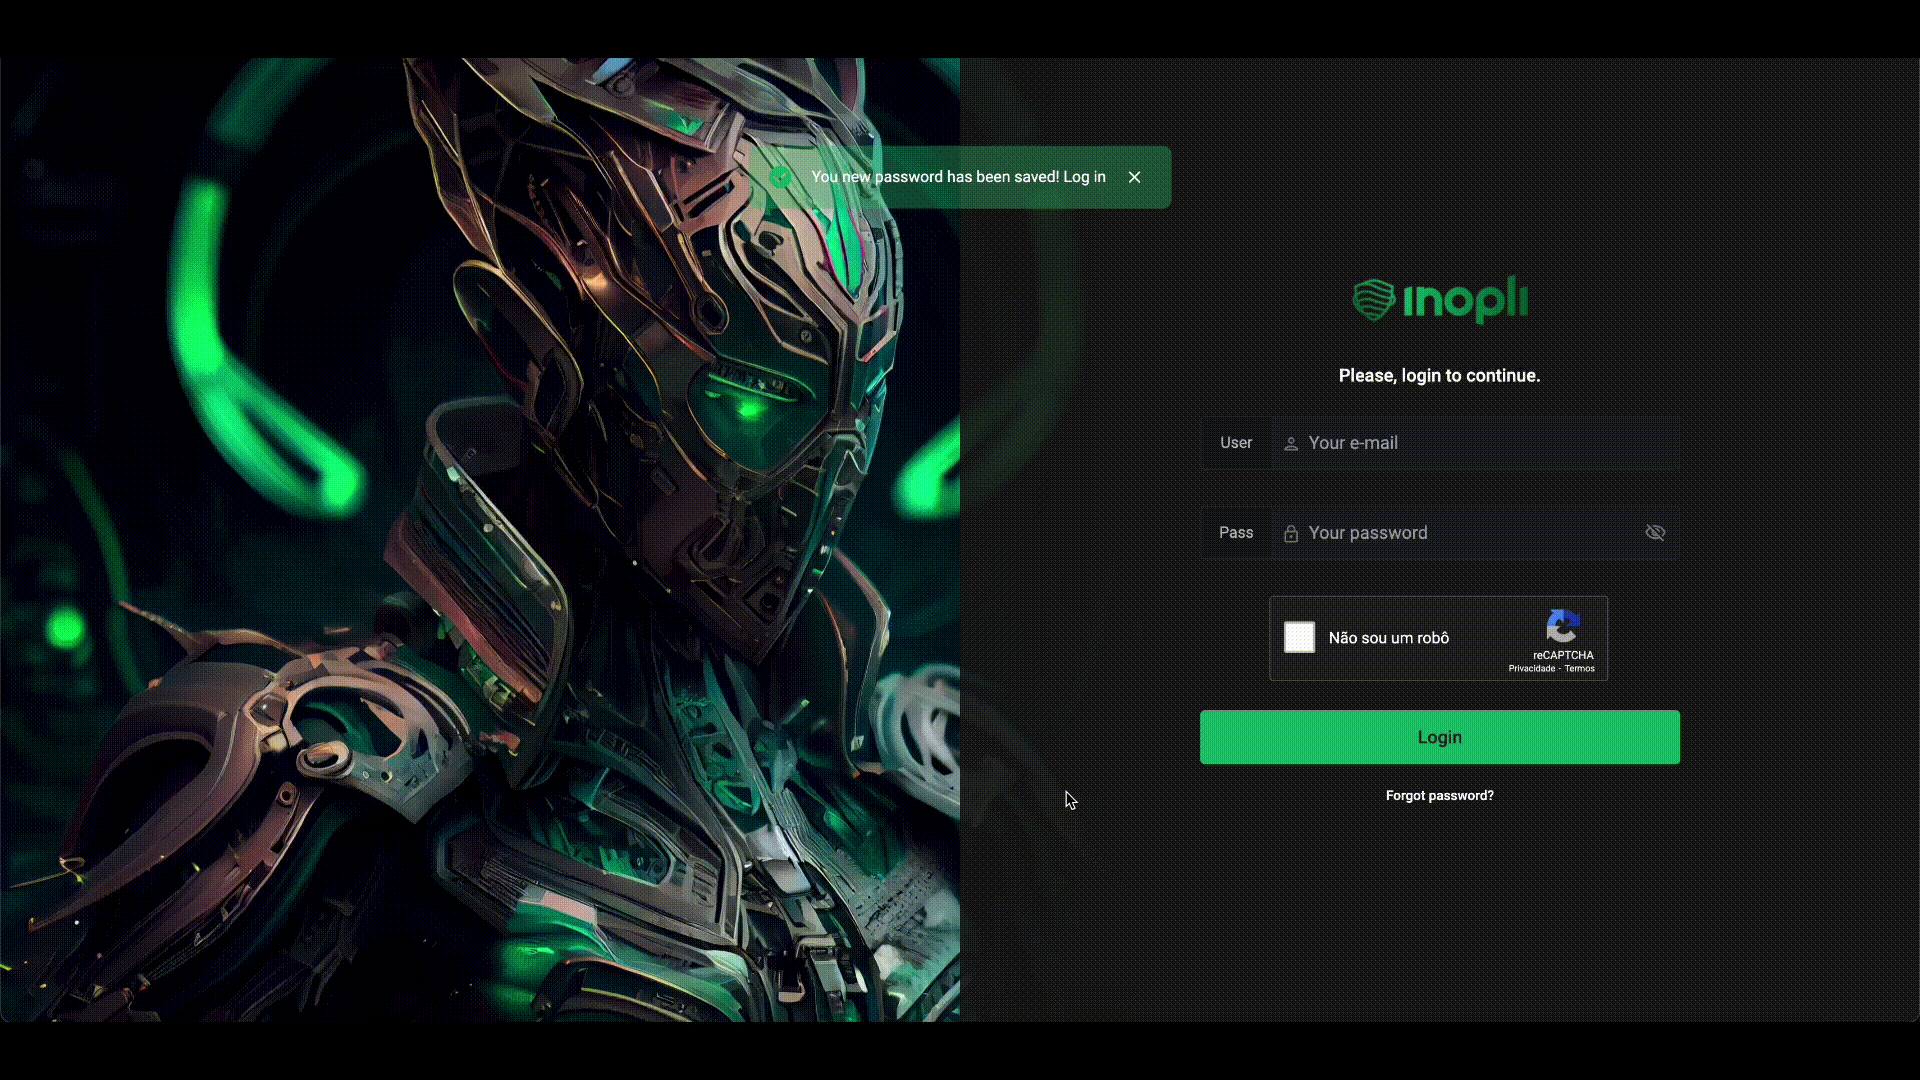
After your account is created by your administrator, you will receive an email to set up your access password.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FCUYbOwHxm0UxIX8463N3%2Fgenerate-password.gif?alt=media&amp;token=5aefca22-67c5-4f31-95c9-5252757d83c4" alt="Video demonstrate how create your password into Inopli"><figcaption><p>How create your password</p></figcaption></figure>

Once set, you can log in to <mark style="color:green;">Inopli</mark> using your credentials.&#x20;

{% embed url="<https://app.inopli.com/>" %}

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2Fk0akvo5MYMyMXGXQs6BX%2Flogin.gif?alt=media&amp;token=70d2a970-5c6e-4835-8d4b-673f50c93982" alt="Video doing login into Inopli"><figcaption><p>Doing login into Inopli</p></figcaption></figure>

Now you are able to use and there are not additional configurations required to access the system.

***


# Modules


# Response Module

## SIEM Management

Inopli <mark style="color:green;">revolutionizes</mark> the way SIEM solutions are configured and deployed. With an <mark style="color:green;">innovative</mark> approach, Inopli offers <mark style="color:green;">automated</mark> installation, minimizing the need for manual intervention and significantly reducing errors. Provide an <mark style="color:green;">easy</mark> and <mark style="color:green;">effective</mark> integration with any existing SIEM solution, <mark style="color:green;">unifying</mark> the management and visibility of active SIEMs.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FfEs3yiknFkMEiWQ0VKgG%2FScreenshot%202023-11-13%20205216.png?alt=media&amp;token=f46caaa4-4c18-4950-8f47-ed858ffbfb3d" alt=""><figcaption><p>Configuring a SIEM into Inopli Solution</p></figcaption></figure>

***

## Automated Triage

Inopli’s automated triage engine leverages artificial intelligence to process and analyze alerts with exceptional precision. With its advanced capability to eliminate up to <mark style="color:$success;">**97.5% of false positives**</mark>, Inopli intelligently identifies and discards duplicate or irrelevant alerts, transforming the triage process into a fully automated and highly efficient operation.

AI-driven correlation models continuously learn from historical data and analyst decisions, improving the platform’s ability to detect meaningful patterns and prioritize what truly matters. The response and investigation of alerts are also automated, guided by adaptive rules that accelerate the workflow and eliminate redundancies, resulting in a substantial reduction in operational workload.

This efficiency is achieved through <mark style="color:$success;">**six critical behavioral criteria**</mark> used by Inopli to determine the relevance and automation potential of each alert. These criteria, combined with the AI treatment process, allow the platform to adapt dynamically to each client’s operational context, delivering a more <mark style="color:$success;">**accurate, agile, and reliable cybersecurity environment**</mark> for organizations of any size.

<details>

<summary>Critical criteria to identify the need for automation</summary>

* Is the same attack generating a considerable number of alerts?
* Is the alert associated with a larger-scale attack?
* Does the alert refer to an incident waiting for resolution, currently being treated, or a previously resolved incident?
* Can the alert be evaluated based on existing security intelligence?
* Is the alert related to a documented correlation rule?
* Is the documentation of the correlation rule adapted to the impacted client?

</details>

These criteria allow Inopli to accurately identify the nature and relevance of each alert, ensuring a <mark style="color:$success;">**rapid and precise response.**</mark> At the same time, the platform adapts its functionality to meet the specific needs of each client. The result is a more effective, agile, and reliable cybersecurity environment for organizations of all sizes.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FSS5fEqmSLc2nuuYA7tZx%2FScreenshot%202023-11-16%20082726.png?alt=media&amp;token=d5b68e0a-5659-4044-b97d-1cddbd6cb636" alt=""><figcaption><p>Dashboard for management of processed alerts</p></figcaption></figure>

***

## Incident Management

<mark style="color:$success;">**Inopli**</mark> enables meticulous tracking of SLAs, ensuring that each incident is managed in strict accordance with established service priorities. Through its sophisticated interface, users can follow the complete lifecycle of every incident, observing all changes and updates in real time.

Inopli stands out for its ability to organize the priority queue based on a severity model that dynamically adapts to each client’s specific context. This ensures that the most critical incidents receive immediate attention, optimizing both response and resolution times.

To enhance operational intelligence, Inopli introduces the <mark style="color:$success;">**Post-Incident Assessment**</mark> feature, powered by artificial intelligence. This module automatically performs an initial evaluation of each incident, identifying potential root causes, affected assets, and incident patterns. The AI’s assessment is directly added to the incident record, providing analysts with an informed starting point for investigation and reducing the time required for manual analysis.

In addition to offering both macro and micro perspectives of the service process, Inopli links incidents directly to their corresponding playbooks, ensuring consistent, guided response actions. This integration, combined with AI-driven assessments, significantly accelerates response time and enables analysts to focus on effective problem resolution with maximum precision and efficiency.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F6D71A4ML54YUPMHgpVJe%2FScreenshot%202023-11-16%20091339.png?alt=media&amp;token=0522c2a4-fa8b-4624-8c88-0447f0c26348" alt=""><figcaption><p>Incident Management Dashboard</p></figcaption></figure>

***

## Documents Management

Inopli empowers users to <mark style="color:green;">efficiently create and manage correlation rule documentation.</mark> These rules are vital for classifying and prioritizing incidents, enabling more effective monitoring and a quick, accurate response to potential threats. Thanks to its flexible and adaptable design, Inopli's <mark style="color:green;">correlation rules can be easily integrated into any SIEM</mark> (Security Information and Event Management) system, significantly enhancing interoperability with various security monitoring solutions.

Furthermore, Inopli offers robust features for <mark style="color:green;">creating and managing incident response playbooks</mark>. These playbooks cover all stages of the incident response lifecycle, from initial detection and analysis to containment, eradication, and recovery. Having detailed and well-documented procedures is crucial not only for <mark style="color:green;">providing clear guidance to security analysts</mark> but also for <mark style="color:green;">ensuring the uniform application of best security practices.</mark> This not only increases operational efficiency but also ensures compliance with corporate regulations and industry standards.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FO86iBkC9bnL0q9RNNZeK%2FScreenshot%202023-11-27%20at%2018.44.44.png?alt=media&amp;token=231c86d2-6175-44b4-abfd-584d399148aa" alt=""><figcaption><p>Create Documentation View</p></figcaption></figure>

***

## Process Automation

By automating the Threat Hunting process, the Security Operations Center (SOC) <mark style="color:green;">team is liberated to focus on more complex challenges and high-level tasks.</mark> Inopli plays a crucial role in this respect, <mark style="color:green;">adopting a proactive strategy in identifying new correlation rule opportunities</mark>. Utilizing advanced and predefined scripts, it analyzes large volumes of data from monitored sources, searching for innovative and significant correlations. Upon discovering a potential correlation, Inopli integrates this finding into its rich knowledge base and signals to the specialized team the need to develop and implement the rule in the system.

In the SIEM (Security Information and Event Management) Management phase, Inopli employs a <mark style="color:green;">specialized agent to oversee the health of servers running solutions like SIEM</mark>. This aspect is fundamental for the early identification of failures or disruptions. Through carefully crafted scripts, Inopli performs detailed health assessments, <mark style="color:green;">detecting anomalies with exceptional precision.</mark> In adverse situations or upon the emergence of problems, Inopli <mark style="color:green;">ensures immediate communication with the responsible team,</mark> providing a quick and efficient response, crucial for maintaining the security and integrity of the system.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FKA0OWCwj1g9Y0bBe5gxT%2FScreenshot%202023-11-27%20at%2018.46.53.png?alt=media&amp;token=54f08a8d-3ddb-49c6-9e70-a44f299ece1b" alt=""><figcaption><p>Healthcheck Dashboard</p></figcaption></figure>

***

## Quality Management

It is possible to track the <mark style="color:green;">efficiency and performance metrics</mark> of the system and the team through performance indicators already configured in the Inopli dashboards. Among these indicators, there are:

<details>

<summary>MTTD (Mean Time to Detect)</summary>

This is the average time required to detect a problem after it has occurred. A reduction in this time implies faster identification and response to incidents, minimizing potential damages.

</details>

<details>

<summary>MTTR (Mean Time to Respond)</summary>

This is the average time it takes to respond to an incident after it has been detected. A shorter MTTR indicates a more agile and prepared team to handle incidents.

</details>

<details>

<summary>MTTC (Mean Time to Contain)</summary>

This is the average time to contain an incident once it has been identified. A reduction in this time limits the spread of damage.

</details>

<details>

<summary>MTTR (Mean Time to Repair)</summary>

This is the average time required to fix an issue after it has been contained. A reduction in this time can lead to quicker recovery and fewer service interruptions.

</details>

<details>

<summary>Compliance with SLA (Service Level Agreement)</summary>

This metric highlights the proportion of cases where the agreed-upon service levels were met. It plays a vital role both in ensuring customer satisfaction and in preventing contractual issues.

</details>

<details>

<summary>Number of Incident Response Playbooks</summary>

This is the total number of Incident Response Playbooks implemented in Document Management, reflecting the team's ability to handle a variety of situations.

</details>

<details>

<summary>Workload Reduction</summary>

This metric shows the amount of work saved through automation and other efficiencies.

</details>

<details>

<summary>Incident Response Playbooks Coverage</summary>

This indicator measures the percentage of Correlation Rules that have documented Incident Response Playbooks. A high percentage reflects thorough preparation and a more structured response system.

</details>

<details>

<summary>Qualitative Assessment in Inopli</summary>

For a qualitative assessment, Inopli has implemented a feedback system within Incident Management. This system tracks the progress of operational maturity through adaptable metrics, allowing leadership and senior cybersecurity staff to thoroughly assess team performance. The assessment process is divided into 3 stages for a comprehensive and fair analysis.\
\
An incident response rating, ranging from 1 to 5 stars, is generated based on this assessment. This rating serves as an immediate indicator of performance and response quality.

Inopli uses this data to establish quality indicators for each analyst's incident response. These indicators support ongoing, in-depth analysis of team effectiveness, help identify areas for improvement, and track progress over time.

</details>

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FlTWoh3c9tmzcflliP0ql%2FScreenshot%202023-11-27%20at%2018.47.09.png?alt=media&amp;token=d51410fe-ebf6-4510-b9f5-5ab5ba72a788" alt=""><figcaption><p>KPI Dashboard</p></figcaption></figure>

***

## Request Management

Inopli features an <mark style="color:green;">advanced automated system for evaluating standard requests</mark>, offering instant and accurate analyses. This functionality ensures that all client requests are handled with agility and efficiency, maximizing customer satisfaction and operational effectiveness.

Through centralized management, we <mark style="color:green;">facilitate collaboration and communication within your team</mark>, providing <mark style="color:green;">continuous and high-quality service to clients</mark>. This system ensures that the entire cybersecurity operations team acts in a synchronized and cohesive manner, addressing client needs with a unified and well-coordinated strategy. Therefore, our integrated approach optimizes the management of client requests, making the process more efficient and less prone to errors or delays. Our solution is designed to <mark style="color:green;">simplify and speed up customer service, ensuring fast and precise responses to all requests</mark>.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FAaaHB2FoMONUyovf0anV%2FScreenshot%202023-11-27%20at%2018.50.22.png?alt=media&amp;token=da3e3a4d-d2f2-4b77-9a49-3f45ebaea849" alt=""><figcaption><p>Request Flowchart</p></figcaption></figure>

***

## MITRE Integration

The automated assessment of MITRE ATT\&CK <mark style="color:green;">provides a clear and comprehensive view</mark> of your organization's cybersecurity landscape. Consequently, <mark style="color:green;">all security incidents are tagged with the MITRE domain</mark>, aligning with the customer's individualized MITRE map. This enables your cybersecurity team to:

* Evaluate and enhance the maturity of your continuous monitoring.&#x20;
* Gain in-depth knowledge of Tactics, Techniques, and Procedures (TTPs).&#x20;
* Implement proactive threat hunting measures, increasing the chances of prompt breach detection.&#x20;

This strategic perspective on monitoring maturity offers <mark style="color:green;">valuable insights into the organization's readiness to handle existing and emerging threats.</mark> It empowers security teams to focus on continuous improvements, thereby strengthening the overall cyber resilience of the organization.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FA0edu6il3tiKEXe305mI%2FScreenshot%202023-11-27%20at%2018.49.02.png?alt=media&amp;token=4c0b1afa-1181-43c7-b1fd-30cefa39dbe1" alt=""><figcaption><p>Att&#x26;ck Matrix Dashboard</p></figcaption></figure>

***


# DRP Module


# Configuring the MSS

Inopli has been designed to <mark style="color:green;">offer customization and scalability</mark>, meeting the specific requirements of the MSS. This platform allows for <mark style="color:green;">flexible configuration and efficient management</mark> of a wide range of customizable parameters. This approach ensures that the system provides <mark style="color:green;">a more assertive and efficient visualization</mark> of performance indicators and other items that enhance the security routine. With Inopli, users can easily adapt the system to align it with their strategic objectives, facilitating the monitoring and analysis of vital data.&#x20;

Moreover, the intuitive interface and the robustness of Inopli's data analysis tools aid in making <mark style="color:green;">evidence-based decisions</mark>, optimizing processes and promoting <mark style="color:green;">more effective management.</mark>

***


# Configuring the MSP's profile

### Identification

In the identification field, you will be able to view <mark style="color:green;">key information about your MSS</mark>, including details such as the name, corporate name, and CNPJ. Additionally, contractual information, such as the contract number, MSS exclusivity, and level, <mark style="color:green;">is managed and edited by Diazero Technologies administrators</mark>. If any of this information is incorrect, please <mark style="color:green;">contact us</mark>. We are here to assist any issues.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FnfWAn7W8iS1QFUBmIR5l%2Fsetup-mss-information.png?alt=media&amp;token=bf57d557-2f74-4d9f-a544-4e23736537ab" alt=""><figcaption><p>MSP's Profile Identification Section</p></figcaption></figure>

***

### Default SLA

A default SLA is a dedicated storage space for the <mark style="color:green;">standard SLAs of MSS client companies</mark>. You can register values by severity for incidents and requests.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FdafYJF7rVOdhR3E4Kbij%2FScreenshot%202023-11-29%20at%2022.19.36.png?alt=media&amp;token=52e13b87-6377-4249-a371-4405ff9938b5" alt=""><figcaption><p>Default SLA View</p></figcaption></figure>

***

### Incident Management

The Incident Management area defines the necessary values for <mark style="color:green;">customizing the automation</mark> of various workflows related to the <mark style="color:green;">handling and treatment</mark> indicators of <mark style="color:green;">incidents</mark>.

1. **Automatic Incident Reminder:** Specify after how many days <mark style="color:green;">a reminder message</mark> should be sent to prompt the analyst to interact with the open incident.
2. **Automatic Incident Completion:** Specify after how many days an open incident without interaction should <mark style="color:green;">be automatically marked as complete</mark>.
3. **Reasonable Time To Respond An Incident:** Define an <mark style="color:green;">ideal time parameter</mark>, in minutes, for responding to an open incident.
4. **Incident Inactivity Notification Time:** Specify the <mark style="color:green;">daily time</mark> at which the processing of notifications or closure of open incidents without activity should be executed.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F06Yw9bB11d1TndRfoDdr%2FScreenshot%202023-11-29%20at%2022.13.40.png?alt=media&amp;token=a77c9fab-5fda-471c-8dd8-d7934f0a7795" alt=""><figcaption><p>Incident Management View</p></figcaption></figure>

***

### Rule Identification Code

This is where you define the <mark style="color:green;">customized prefix for correlation rules</mark> to be created in the system. Typically, it consists of 2 or 3 letters.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FZb4a5wGFP31uSbAzloZH%2FScreenshot%202023-11-29%20at%2022.28.00.png?alt=media&amp;token=da40c16b-ca2a-45e2-bf7d-52c55c8ef370" alt=""><figcaption><p>Rule Identificstion Code View</p></figcaption></figure>

***

### Preferences

Reserved space for general system preferences.

1. **Rules Status:** Indicates whether <mark style="color:green;">correlation rules with an incomplete</mark> status can be activated.
2. **Ideal Time For Support Assistance:** Define, in minutes, the <mark style="color:green;">ideal response time to a customer's message</mark> in the chat.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FGrQNXXPCF8EQpM73gNUO%2FScreenshot%202023-11-29%20at%2022.20.12.png?alt=media&amp;token=56e17086-5170-491b-b1df-93a648ff3f9a" alt=""><figcaption><p>Preferences View</p></figcaption></figure>

***

### Logo

The <mark style="color:green;">MSS logo</mark> will be uploaded, which will be used throughout the system.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FUKQCmeoi9B4zc3pKYCpW%2FScreenshot%202023-11-29%20at%2022.21.49.png?alt=media&amp;token=a3035aa0-ca23-4c82-8f63-1b9728be25cd" alt=""><figcaption><p>Logo View</p></figcaption></figure>

***


# Request Categories

Request Profiles screen is a dedicated interface for <mark style="color:green;">creating and editing request profiles.</mark> These profiles can be filtered, activated, deactivated, deleted, and linked to companies, offering 100% <mark style="color:green;">customization to meet client-specific needs.</mark> It enables the mapping of the most frequent requests and the definition of the information flow required from the user. This approach streamlines <mark style="color:green;">problem resolution</mark>, making it <mark style="color:green;">faster</mark> and <mark style="color:green;">more efficient</mark>. Additionally, the system allows for configuring the responses to <mark style="color:green;">assign a level of criticality to each request</mark>.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FmoPeZcinXMZOWRMrp4ug%2Flist-request-profile.gif?alt=media&amp;token=47d3b58c-511d-4787-9e2a-53092d422c79" alt=""><figcaption><p>List of Request Profiles</p></figcaption></figure>

***

### Creating a Request Profile

When creating a profile, <mark style="color:green;">it's essential to provide a name and description.</mark>&#x20;

The flowchart outlines the <mark style="color:green;">user's journey when initiating a request</mark>, aiding in retrieving relevant information. Certain stages allow defining the criticality of the ensuing request.

Adding a new stage to the flow is as simple as clicking the '+' sign. In every stage the user's response is mandatory.

#### Types of Stages

{% tabs %}
{% tab title="Title" %}
This is the first stage of the flow, where a standard question is posed. The user's text response forms the <mark style="color:green;">title of the request</mark>.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F5qcgXKVw4mp8vONjq73F%2FScreenshot%202023-11-30%20at%2021.32.48.png?alt=media&amp;token=23254b39-b9c6-48fa-8d75-91af1c39ad44" alt=""><figcaption><p>Title Stage</p></figcaption></figure>
{% endtab %}

{% tab title="Question" %}
This second standard stage, where <mark style="color:green;">you can set the main question</mark> to be answered for different 'Response' stage types.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2Fw6kotUZbK08zjHMT4bmV%2Fquestion-stage.gif?alt=media&amp;token=6db75f16-aa89-4d15-823f-7cd38c5e1847" alt=""><figcaption><p>Adding Question Stage</p></figcaption></figure>
{% endtab %}

{% tab title="Response" %}
At this stage, <mark style="color:green;">the criticality of the request is determined.</mark> It presents the user with fixed response options to the 'Question' stage, typically in a select format.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F17EiiL2dhHybpm4cvtQG%2Fresponse-stage.gif?alt=media&amp;token=dbd07f21-a833-4f6f-a6ec-c4ab15aea7f5" alt=""><figcaption><p>Adding Response Stage</p></figcaption></figure>
{% endtab %}

{% tab title="Text" %}
A stage for <mark style="color:green;">open-ended questions.</mark>

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FQjyiC6ZrREJahGTpvxDB%2Ftext-response-stage.gif?alt=media&amp;token=9dd0306d-52d7-4bb3-b99a-d39e6c54a7bc" alt=""><figcaption><p>Adding open-ended questions</p></figcaption></figure>
{% endtab %}
{% endtabs %}

To complete this flow, connect all stages to form a continuous sequence leading to the 'Create Request' stage.

Once the flow is finalized, it can be linked to companies that will use it as their request flow.

{% hint style="warning" %}
Remember: Each company can only be linked to one request profile.
{% endhint %}

***


# Policies

Policies section in Inopli offers an <mark style="color:green;">advanced text editor,</mark> specially designed for the development and documentation of <mark style="color:green;">business policies</mark>. This tool is focused on the operational area, acting as an <mark style="color:green;">essential guide</mark> for the execution of specific processes. In Inopli, users can customize policies for two main workflows:&#x20;

1. Incident Response: establishes clear procedures for incident handling.
2. Creating Correlation Rules: guides the structuring of internal rules.

The editor itself is <mark style="color:green;">intuitive</mark> and similar to text editing platforms, <mark style="color:green;">offering a range of text formatting</mark> options, including bold, italic, lists, and much more. These features allow users to <mark style="color:green;">highlight the most critical parts of the policies</mark>, ensuring that important points are easily <mark style="color:green;">identifiable and understood.</mark> With this tool, Inopli facilitates the creation of clear and effective guidelines, which are fundamental for the safe management and operationalization of business activities.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FGicKzJkVjT1Ope5vr041%2Fpolices-examples.gif?alt=media&amp;token=6ce4b821-851a-4346-885c-6312a2072df2" alt=""><figcaption><p>Edit Polices View</p></figcaption></figure>

***


# Managing Integrations

The Inopli integration system is very flexible, <mark style="color:green;">offering compatibility with the most popular and widely used systems</mark>. Each integration is designed to amplify the functionalities of Inopli, providing an even more productive experience.

In the this section, users have the capability to <mark style="color:green;">configure and manipulate</mark> various types of integrations. These integrations can be filtered, activated, deactivated and deleted, offering 100% <mark style="color:green;">customization to meet client-specific needs.</mark>

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FExncWHqj48FV9rmjVagH%2Fintegrations.gif?alt=media&amp;token=56e682cd-af96-439b-95df-d916b8ba8426" alt=""><figcaption><p>Overview Integrations Dashboard</p></figcaption></figure>

{% content-ref url="/pages/VIc1NTrGFoYrk3gU9ByE" %}
[E-mail](/system-settings/configuring-the-mss/managing-integrations/e-mail)
{% endcontent-ref %}

{% content-ref url="/pages/IYRSKIyXMbWrM7yzT4GX" %}
[ChatGPT](/system-settings/configuring-the-mss/managing-integrations/chatgpt)
{% endcontent-ref %}

{% content-ref url="/pages/wSLd0oVFHe52mqeQFMqg" %}
[Google Chat](/system-settings/configuring-the-mss/managing-integrations/google-chat)
{% endcontent-ref %}

{% content-ref url="/pages/RVAUa8DSXGdG2Sp234gv" %}
[Slack](/system-settings/configuring-the-mss/managing-integrations/slack)
{% endcontent-ref %}

{% content-ref url="/pages/JXpaITAcaLc4i2scbMJq" %}
[Telegram](/system-settings/configuring-the-mss/managing-integrations/telegram)
{% endcontent-ref %}


# ChatGPT

The ChatGPT in Inopli <mark style="color:green;">serves as an assistance tool for analysts</mark> in their daily tasks. It can be used in various activities, <mark style="color:green;">addressing specific queries</mark>, or <mark style="color:green;">generating playbooks</mark> into correlation rule edition. Additionally, ChatGPT <mark style="color:green;">is accessible via a quick access button</mark>, allowing for consultations at any moment.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F48gGGCnAO2c3LI8vNW89%2Fchat_gpt.gif?alt=media&amp;token=a710c04c-2b18-4e67-a2e7-478d5cc69629" alt=""><figcaption><p>Overview ChatGPT  Feature</p></figcaption></figure>

To enable ChatGPT in Inopli, you need to <mark style="color:green;">register the access token</mark> number provided by your ChatGPT account.

See below which field to enter the access token:

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F4nacrvCrLUPfakLXgjS2%2FScreenshot%202023-12-06%20at%2020.24.20.png?alt=media&amp;token=984bd776-bdbf-4d07-aaae-eec0d6252cc0" alt=""><figcaption><p>Field to enter ChatGPT access token.</p></figcaption></figure>

***


# Slack

Slack is implemented as a solution for <mark style="color:green;">notifying and auditing events</mark> that are <mark style="color:green;">triggered by predefined triggers on the integration page</mark>. These triggers are activated through a <mark style="color:green;">simple selection</mark>. Ensuring <mark style="color:green;">agile and precise communication</mark> within the team.

To set up the integration with Slack, it is essential to provide the pre-configured <mark style="color:green;">Bot Token and Chat Id from Slack.</mark>

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FBS2TWI5CvFaFMsIyMIWU%2FScreenshot%202023-12-06%20at%2020.36.29.png?alt=media&amp;token=cf7b90bb-2ffb-4648-a6ec-22febbf3b1c4" alt=""><figcaption><p>Integration with Slack</p></figcaption></figure>

Following this step, simply <mark style="color:green;">choose from the predefined options which events you wish to monitor through the integration</mark>, tailoring the setup to your specific needs and preferences.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FrhQyuPbe0NY5yMk45dom%2FScreenshot%202023-12-06%20at%2020.39.16.png?alt=media&amp;token=e3d7d319-6f25-4d01-9dd2-0aee13ee3fe9" alt=""><figcaption><p>Predefined options to monitor through integration.</p></figcaption></figure>

***


# Telegram

Telegram is implemented as a solution for <mark style="color:green;">notifying and auditing events</mark> that are <mark style="color:green;">triggered by predefined triggers on the integration page</mark>. These triggers are activated through a <mark style="color:green;">simple selection</mark>. Ensuring <mark style="color:green;">agile and precise communication</mark> within the team.

To set up the integration with Telegram, it is essential to provide the pre-configured <mark style="color:green;">Bot Username and Bot Token from Telegram</mark>.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FtWlcSnaXSvaj6kMuv71D%2FScreenshot%202023-12-06%20at%2020.42.32.png?alt=media&amp;token=3641fdda-c7f5-4608-ad5c-a51826507e68" alt=""><figcaption><p>Integration with Telegram.</p></figcaption></figure>

Following this step, simply <mark style="color:green;">choose from the predefined options which events you wish to monitor through the integration</mark>, tailoring the setup to your specific needs and preferences.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FrhQyuPbe0NY5yMk45dom%2FScreenshot%202023-12-06%20at%2020.39.16.png?alt=media&amp;token=e3d7d319-6f25-4d01-9dd2-0aee13ee3fe9" alt=""><figcaption><p>Predefined options to monitor through integration.</p></figcaption></figure>

***


# Google Chat

Google Chat is implemented as a solution for <mark style="color:green;">notifying and auditing events</mark> that are <mark style="color:green;">triggered by predefined triggers on the integration page</mark>. These triggers are activated through a <mark style="color:green;">simple selection</mark>. Ensuring <mark style="color:green;">agile and precise communication</mark> within the team.

To set up the integration with Google Chat, it is essential to provide the pre-configured <mark style="color:green;">Key, Token and Space from Google Chat</mark>.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F6f2tPALAAHwNJOa9cOVy%2FScreenshot%202023-12-06%20at%2020.44.17.png?alt=media&amp;token=31aeef53-97ce-4938-b921-d6126b794599" alt=""><figcaption><p>Integration with Google Chat</p></figcaption></figure>

Following this step, simply <mark style="color:green;">choose from the predefined options which events you wish to monitor through the integration</mark>, tailoring the setup to your specific needs and preferences.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FrhQyuPbe0NY5yMk45dom%2FScreenshot%202023-12-06%20at%2020.39.16.png?alt=media&amp;token=e3d7d319-6f25-4d01-9dd2-0aee13ee3fe9" alt=""><figcaption><p>Predefined options to monitor through integration.</p></figcaption></figure>

***


# E-mail

The integrated email sending system in Inopli allows for <mark style="color:green;">notifications and auditing</mark> <mark style="color:green;">of events triggered by predefined triggers on the integration page.</mark> The activation of these triggers is <mark style="color:green;">simplified</mark>, ensuring agile and accurate communication within the team. Additionally, it offers the [<mark style="color:green;">possibility to configure automatic emails for reports</mark>](/) on vital system indicators, <mark style="color:green;">with flexibility in both the frequency and content</mark> of these reports, adapting to the specific needs of the user.

For the email system configuration, simply <mark style="color:green;">enter the emails that should receive the information</mark>.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FV7KvtFLuogsYizAetLTn%2FScreenshot%202023-12-06%20at%2023.33.52.png?alt=media&amp;token=3858839a-9782-4e6d-93c0-d9002cccacec" alt=""><figcaption><p>Integration with E-mail</p></figcaption></figure>

Following this step, simply <mark style="color:green;">choose from the predefined options which events you wish to monitor through the integration</mark>, tailoring the setup to your specific needs and preferences.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FrhQyuPbe0NY5yMk45dom%2FScreenshot%202023-12-06%20at%2020.39.16.png?alt=media&amp;token=e3d7d319-6f25-4d01-9dd2-0aee13ee3fe9" alt=""><figcaption><p>Predefined options to monitor through integration.</p></figcaption></figure>

{% hint style="info" %}
For more information about [**Automated Reports**](/) access our article.
{% endhint %}

***


# Data Sources

In the this section, users have the capability to <mark style="color:green;">configure and manipulate</mark> various data sources, which <mark style="color:green;">generate information in the form of events</mark>. These data are captured by the Security Information and Event Management (SIEM). Once collected, <mark style="color:green;">they are processed and analyzed to determine whether they constitute a security incident or not</mark>. This decision depends on the analysis conducted by the alert handling engine, which is configurable to meet specific criteria.&#x20;

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F0pZu74kZYGNFSiq56AC3%2FScreenshot%202023-12-05%20at%2020.27.56.png?alt=media&amp;token=0a9c2017-566b-4b78-a0de-6ce6abf50ef2" alt=""><figcaption><p>Data Sources Overview</p></figcaption></figure>

Users can view a paginated <mark style="color:green;">list of all created data sources</mark>. This screen provides the functionality to <mark style="color:green;">filter data sources based on their status</mark>, whether active or inactive. This initial dashboard is <mark style="color:green;">designed to facilitate the administration of data sources</mark>, allowing users to change the status, edit the settings of a specific data source, or delete it with just a few clicks.

{% hint style="info" %}
**Data Source** is any location, system, or device where data is generated or stored. This includes servers, network devices, applications, databases, file systems, and even cloud services. It is used as feeding security tools and systems with real-time or near-real-time information. This includes Intrusion Detection and Prevention Systems (IDS/IPS), Security Information and Event Management (SIEM) systems, and network behavior analysis solutions.
{% endhint %}

***

### Creating a Data Source

#### Identification

When creating a data source, it's essential to provide <mark style="color:green;">a name and description</mark>.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FcmEgMSzQtvGfWbw7KdZE%2FScreenshot%202023-12-05%20at%2020.24.26.png?alt=media&amp;token=4dfd205b-542d-4f5b-aee9-36e1727e8090" alt=""><figcaption><p>Identification Stage</p></figcaption></figure>

#### Event Types

It is possible to associate <mark style="color:green;">patterns of events</mark> (event types) detected in a data source, which share a <mark style="color:green;">history or similar behavior</mark>, with the goal of identifying and mapping anomalies. These patterns will <mark style="color:green;">serve as a reference</mark> in the development of correlation rules. This significantly enhances the <mark style="color:green;">efficiency of processing and uniformity in incident generation</mark>, contributing to a quicker and more accurate response to potential threats.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FRDctWNt9cpwamUMpUOkz%2FScreenshot%202023-12-05%20at%2020.26.02.png?alt=media&amp;token=324ea5f9-f4a0-4d82-8a85-b0e5b6051be6" alt=""><figcaption><p>Eventy Types Stage</p></figcaption></figure>

{% hint style="info" %}
**Event Type** is a classification used to describe the nature of an event detected by data sources. Help security analysts understand what happened, why it happened, and how it should be addressed. It can be classified into various categories, such as unauthorized access attempts, system failures, configuration changes, suspicious network activities, application errors, and others. Each category represents a distinct event type with specific implications for security.
{% endhint %}

#### Config Files

It functions as a repository containing <mark style="color:green;">files used to ensure normalization and standardization</mark> among clients during the implementation of the SIEM, which will be involved in processing correlation rules. It is possible to load files in <mark style="color:green;">.xml, .config, or .json formats</mark>. Additionally, the system allows for the <mark style="color:green;">consultation of previously modified versions</mark> of these configuration files, <mark style="color:green;">facilitating the management of changes over time.</mark>

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FvEpHQ33cUAcqdFJYbJwR%2FScreenshot%202023-12-05%20at%2020.27.00.png?alt=media&amp;token=33969a88-e8c9-45e5-94a6-dfe7f64d99d2" alt=""><figcaption><p>Config Files Stage</p></figcaption></figure>

***


# Roles

Users can view a paginated <mark style="color:green;">list of all created roles profiles</mark>. This screen provides the functionality to <mark style="color:green;">filter roles based on their status</mark>, whether active or inactive. This initial dashboard is designed to facilitate the administration of roles, allowing users to <mark style="color:green;">change the status, edit the role profile, duplicate a role profile, or delete it</mark> with just a few clicks.

### MSP's Roles

It is possible to <mark style="color:green;">create specific roles for each MSP</mark>, allowing for more <mark style="color:green;">detailed and centralized administration</mark>.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FetDXgerB1R8I8hn4T95g%2FScreenshot%202023-12-12%20at%2021.05.52.png?alt=media&amp;token=5b8a0d18-44cd-45ea-bf94-174c86a09d93" alt=""><figcaption><p>MSP's Roles</p></figcaption></figure>

### Roles for Companies

It serves as a <mark style="color:green;">pre-configured set of access rule standards, established by the MSS.</mark> These standards <mark style="color:green;">act as access profile templates for companies</mark>, significantly <mark style="color:green;">simplifying the access management</mark> process for clients. With this repository, businesses <mark style="color:green;">can quickly implement access profiles</mark>, ensuring a more efficient and standardized administration of security policies in their operations.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FZoabNuklYQBi83z08xNk%2FScreenshot%202023-12-05%20at%2020.56.38.png?alt=media&amp;token=b1fb5e43-7cab-4186-abfe-d95d59f40f1f" alt=""><figcaption><p>Roles For Companies Overview</p></figcaption></figure>

{% content-ref url="/pages/sjSZv5OtsQFxq84UvAqi" %}
[Creating a Role](/system-settings/configuring-the-mss/roles/creating-a-role)
{% endcontent-ref %}

***


# Creating a Role

### Identification

When creating a role, it's essential to provide <mark style="color:green;">a name and description</mark>.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FQYD5bHdonxeXlusM5LIB%2FScreenshot%202023-12-05%20at%2021.07.09.png?alt=media&amp;token=8dce875e-8623-45c0-823a-141b8d60b33c" alt=""><figcaption><p>Identification Stage</p></figcaption></figure>

### Permissions

Where detailed configurations are made regarding <mark style="color:green;">which permissions will be granted to a specific profile</mark>, among the options of product, category, or functionality. This area <mark style="color:green;">provides filtering tools</mark>, allowing users to search for and select permissions either by name or through direct selection. This system <mark style="color:green;">facilitates the assignment of permissions</mark>, ensuring more precise control over access to different parts of the product.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FTjjoBgzEvLdLZWZ2ckcR%2FScreenshot%202023-12-05%20at%2021.13.59.png?alt=media&amp;token=8f3c05f8-f12d-48c5-b8e7-013179d146f6" alt=""><figcaption><p>Permissions Stage</p></figcaption></figure>

***

### Companies (Only for Roles for Companies)

This space is dedicated to the <mark style="color:green;">activation of clients who can use the profile as a template</mark>. In a practical way, through a switch, it is easy to select which companies will have access to this template model as an option for use.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FOMc6kwf4onBHOs3ROPLZ%2FScreenshot%202023-12-05%20at%2021.20.32.png?alt=media&amp;token=cd00868d-b450-4ff2-8477-114efe3312fa" alt=""><figcaption><p>Companies Stage</p></figcaption></figure>

***


# Managing Companies

Inopli offers a great solution for <mark style="color:green;">company management</mark>, providing an intuitive control panel that allows access to an <mark style="color:green;">organized and paginated list</mark>. This panel includes <mark style="color:green;">useful filters</mark>, such as activity status (active or inactive), specific roles, and a search bar for custom queries. It also <mark style="color:green;">simplifies the editing and deletion of companies.</mark> This functionality <mark style="color:green;">eases administration</mark>, allowing for the customization of the experience according to the unique needs of each client.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FXz8dqYImSZkqY8JJtRQb%2Fcompanies-dashboard.gif?alt=media&amp;token=8748ba01-65f4-4f8e-acd0-633b19201d63" alt=""><figcaption><p>Overview Companies Dashboard</p></figcaption></figure>

***


# Configuring the Company's profile

### Identification

In the identification section, a <mark style="color:green;">view of the important information of the companies</mark> is provided, including details such as <mark style="color:green;">name, corporate name, CNPJ</mark> (Brazilian National Registry of Legal Entities), <mark style="color:green;">telephone number, postal code, and full address.</mark> This area facilitates quick and efficient access to the essential data of each company. <mark style="color:green;">This information is managed and edited by Diazero Technologies administrators</mark>. If any of this information is incorrect, please <mark style="color:green;">contact us</mark>. We are here to assist any issues.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FvM5bmav6pMkZxdFJmd4w%2FScreenshot%202023-12-07%20at%2021.19.05.png?alt=media&amp;token=21540433-6fab-41ab-8f75-ffc2a2da6790" alt=""><figcaption><p>Company's Profile Identification Section</p></figcaption></figure>

***

### SLA

The Service Level Agreement (SLA) section <mark style="color:green;">provides the option to customize SLA values</mark> for resolving incidents and requests, based on the severity and/or criticality of each case. Additionally, it's [<mark style="color:green;">easy to adopt the SLA standards previously set in the company's MSS profile</mark>](/system-settings/configuring-the-mss/configuring-the-msps-profile#default-sla), using an activation switch for a simplified and efficient setup.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FnYw4GP6R1svhrVOizVwK%2FScreenshot%202023-12-07%20at%2021.27.52.png?alt=media&amp;token=8d64cbb6-1b9e-407a-a8a3-007a60827138" alt=""><figcaption><p>SLA Configuration Section</p></figcaption></figure>

***

### Logo

With an intuitive drag-and-drop feature, it's <mark style="color:green;">possible to personalize the company profile by uploading its logo</mark> in either <mark style="color:green;">.png or .jpg</mark> formats.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FzR7LbSKyQfFWZq8btngo%2FScreenshot%202023-12-07%20at%2021.29.21.png?alt=media&amp;token=eb4c18e0-db0b-4059-bf92-e04d659ef286" alt=""><figcaption><p>Logo Configuration Section</p></figcaption></figure>

***


# Company's Roles

In <mark style="color:green;">addition to the standard roles provided by the MSS</mark>, it is possible to <mark style="color:green;">create specific roles for each company</mark>, allowing for more <mark style="color:green;">detailed and centralized administration</mark>. Both types of roles - those provided by the system and those custom-created - will be <mark style="color:green;">displayed in a paginated list, with advanced filtering options</mark>. Furthermore, these roles come with practical functionalities for activation/deactivation, editing, and deletion, simplifying the management and customization of system access.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F51EY6yxRO6wCsUb5BXNY%2FScreenshot%202023-12-08%20at%2020.12.31.png?alt=media&amp;token=bd29d068-3634-4393-ad5c-01616e672a5b" alt=""><figcaption><p>Overview of company's roles</p></figcaption></figure>

{% content-ref url="/pages/sjSZv5OtsQFxq84UvAqi" %}
[Creating a Role](/system-settings/configuring-the-mss/roles/creating-a-role)
{% endcontent-ref %}

***


# Managing Company's Integrations

The setup of integrations with major messaging services <mark style="color:green;">enables the client to have control over notifications and/or auditing</mark>. The process to establish these integrations [<mark style="color:green;">is similar to that already configured for the MSP profile</mark>](/system-settings/configuring-the-mss/managing-integrations), ensuring a user-friendly experience.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FvSS8XF14qVt3Fzxqvk08%2FScreenshot%202023-12-07%20at%2021.40.50.png?alt=media&amp;token=b62a224e-a3b0-4f7b-be13-7dc9c1cd20f7" alt=""><figcaption><p>Company's Integrations Dashboard</p></figcaption></figure>

{% content-ref url="/pages/VIc1NTrGFoYrk3gU9ByE" %}
[E-mail](/system-settings/configuring-the-mss/managing-integrations/e-mail)
{% endcontent-ref %}

{% content-ref url="/pages/wSLd0oVFHe52mqeQFMqg" %}
[Google Chat](/system-settings/configuring-the-mss/managing-integrations/google-chat)
{% endcontent-ref %}

{% content-ref url="/pages/RVAUa8DSXGdG2Sp234gv" %}
[Slack](/system-settings/configuring-the-mss/managing-integrations/slack)
{% endcontent-ref %}

{% content-ref url="/pages/JXpaITAcaLc4i2scbMJq" %}
[Telegram](/system-settings/configuring-the-mss/managing-integrations/telegram)
{% endcontent-ref %}

***


# Monitoring Systems

This interface in question is designed to efficiently <mark style="color:green;">manage the monitoring systems associated with the company.</mark> It offers comprehensive compatibility, *<mark style="color:green;">**allowing integration with any vendor**</mark>*. This interface <mark style="color:green;">facilitates the management of each SIEM individually</mark>. Users can view all the integrations established with the company in an organized and paginated manner. Furthermore, the interface provides <mark style="color:green;">simplicity in editing the activation status, in deleting existing integrations, and in adding new integrations.</mark>

{% hint style="info" %} <mark style="color:green;">**Monitoring System**</mark> is designed to function as a <mark style="color:green;">central repository</mark>, <mark style="color:green;">collecting and processing all events</mark> from various data sources. It plays a crucial role in the organization and analysis of these events. A powerful correlation mechanism, built on the principles of <mark style="color:green;">Boolean algebra</mark>, continuously searches for patterns indicating anomalies. Once detected, these anomalies trigger alerts with unique identifiers based on the used Boolean algebra. These identifiers are <mark style="color:green;">integrated into our relational system to link the detected events to their respective correlation rules</mark>.
{% endhint %}

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FelvekwMUyg5g02ycKTFg%2FScreenshot%202023-12-11%20at%2020.03.56.png?alt=media&amp;token=500a7562-61a7-4a48-b822-b3c1f82a7e73" alt=""><figcaption><p>Overview Monitoring System</p></figcaption></figure>

***

### Creating a new monitoring system integration

#### Identification

When creating a monitoring system integration, it's essential to provide <mark style="color:green;">a name and description</mark>.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FWe6X8PmgTMEs1g7gXBsR%2FScreenshot%202023-12-11%20at%2020.20.28.png?alt=media&amp;token=65037fb1-48d2-4441-bd43-c2ad66ee6c24" alt=""><figcaption><p>Identification Stage</p></figcaption></figure>

#### Vendor

Each vendor has their own standard for configuring integrations, and <mark style="color:green;">our system is versatile enough to connect with any SIEM.</mark>

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FkoDxaVH5YoDlBNZ7pLeR%2FScreenshot%202023-12-11%20at%2020.28.55.png?alt=media&amp;token=ce653611-0130-4a89-9a5c-a89e51dc5a12" alt=""><figcaption><p>Vendor Options into Configuration Stage</p></figcaption></figure>

#### Servers

Our system enables the <mark style="color:green;">registration and continuous monitoring of the status of servers</mark> supporting the monitoring solution. This feature allows Inopli to have a detailed understanding of the architecture and function of each server. Management is optimized through a paginated listing interface, which includes advanced filtering features, as well as options to maintain, edit, or remove the 'active' status of servers.

Additionally, Inopli <mark style="color:green;">provides a specialized agent to be installed on the servers.</mark> This agent is responsible for <mark style="color:green;">constantly monitoring the server's health</mark>, ensuring its continuous operation. In case of any issues, Inopli <mark style="color:green;">automatically intervenes to make corrections</mark>, ensuring that the server remains functional without interruptions.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F2skiLaWcpq0SuLgHPbdr%2FScreenshot%202023-12-11%20at%2020.45.15.png?alt=media&amp;token=c46ed7ff-8b29-4c17-b7cb-0ede6ebf5026" alt=""><figcaption><p>Overview Servers Stage</p></figcaption></figure>

To register a new server in our system, it is necessary to provide essential information such as the <mark style="color:green;">agent's token, a fullname of the server, and its intended function.</mark> After this step, it is possible to link <mark style="color:green;">Threat Hunting and Health Check profiles</mark> to the server, as needed. These profiles are essential for ensuring efficient monitoring and maintaining the server's health.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FzO0NrMrvoiKtqBjvC39q%2FScreenshot%202023-12-11%20at%2022.46.41.png?alt=media&amp;token=7f9f1f58-7ae2-43bf-938d-2e138f9a3736" alt=""><figcaption><p>Adding a server</p></figcaption></figure>

***


# Managing User Access


# Creating MSP's user accounts

Viewing all registered users in an MSP is efficient and organized. The interface allows <mark style="color:green;">for paginated navigation and offers intuitive filters for activation status, access profile, and language</mark>. There is also a quick search functionality for the user's name. <mark style="color:green;">User management operations allow for easy activation, deactivation, deletion, password resetting, or profile editing</mark>.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FqiVxAnIkMvIdzGGSi5rU%2FScreenshot%202023-12-13%20at%2020.55.58.png?alt=media&amp;token=70b1d3ab-e054-4a8f-85b7-4d37990f0966" alt=""><figcaption><p>Overview MSP's Users</p></figcaption></figure>

To register a new user, it <mark style="color:green;">is mandatory to provide a first name, last name, and an email address.</mark> Additional information, such as phone number, preferred language, and avatar, can be added to enhance profile identification.

{% hint style="warning" %}
The email must be unique on the platform.
{% endhint %}

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FTcO10nKjXyhVEs7mDrOG%2FScreenshot%202023-12-13%20at%2020.56.58.png?alt=media&amp;token=67b00843-f046-4250-9fe4-c30271cdce53" alt=""><figcaption><p>Creating MSP's User</p></figcaption></figure>

The concept of <mark style="color:green;">'roles' is crucial, defining the access levels and responsibilities of the user on the platform.</mark> After setting up the profile, the user will receive an email with the necessary details for the first access.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FhI9HXS8iCpi9O3XV6hkw%2FScreenshot%202023-12-13%20at%2020.59.06.png?alt=media&amp;token=f0d11992-edbe-49e0-b129-0627468854f1" alt=""><figcaption><p>Selecting Role Profile for New User</p></figcaption></figure>

{% content-ref url="/pages/0mjABzcxr7BsAE7w5LHJ" %}
[First Access](/getting-started/first-access)
{% endcontent-ref %}

***


# Creating end user accounts

Viewing all registered users in a company is efficient and organized. The interface allows <mark style="color:green;">for paginated navigation and offers intuitive filters for activation status, access profile, and language</mark>. There is also a quick search functionality for the user's name. <mark style="color:green;">User management operations allow for easy activation, deactivation, deletion, password resetting, or profile editing</mark>.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FKroZ9lNZlFaTjo02fi46%2FScreenshot%202023-12-13%20at%2021.03.07.png?alt=media&amp;token=80b11bb8-ffbf-45d3-8af3-544abf3f0754" alt=""><figcaption><p>Overview End Users</p></figcaption></figure>

To register a new user, it <mark style="color:green;">is mandatory to provide a first name, last name, and an email address.</mark> Additional information, such as phone number, preferred language, and avatar, can be added to enhance profile identification.

{% hint style="warning" %}
The email must be unique on the platform.
{% endhint %}

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F8iBk0fRqu4Jd7hcKyFvj%2FScreenshot%202023-12-13%20at%2021.05.08.png?alt=media&amp;token=11292ccb-f55a-4691-b9ef-c2790e7cf389" alt=""><figcaption><p>Creating End User</p></figcaption></figure>

The concept of <mark style="color:green;">'roles' is crucial, defining the access levels and responsibilities of the user on the platform.</mark> After setting up the profile, the user will receive an email with the necessary details for the first access.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FhI9HXS8iCpi9O3XV6hkw%2FScreenshot%202023-12-13%20at%2020.59.06.png?alt=media&amp;token=f0d11992-edbe-49e0-b129-0627468854f1" alt=""><figcaption><p>Selecting Role Profile for New User</p></figcaption></figure>

{% content-ref url="/pages/0mjABzcxr7BsAE7w5LHJ" %}
[First Access](/getting-started/first-access)
{% endcontent-ref %}

***


# Rules

Inopli serves as a central hub for operational documents, used to optimize incident processing. This centralization facilitates the <mark style="color:green;">documentation and management of correlation rules, making them more accessible and efficient in the operational context.</mark>&#x20;

The system integrates with the alert engine, using the information from the correlation rules to initiate incident procedures. This integration <mark style="color:green;">not only allows the automatic opening of incidents based on the generated alerts, but also supports incident grouping strategies.</mark> This ensures compliance with recognized market frameworks, ensuring best practices and operational standards.&#x20;

<mark style="color:green;">It is mandatory that the correlation rules are properly configured and active.</mark> In the absence of these rules, the system cannot identify the necessary information to open an incident, ignoring the alerts.

***

#### **Dashboard:**

Provides a view of the indicators related to the status of the correlation rules. Users can identify which rules are active and which are inactive, crucial information in the listing of the set of registered rules, and <mark style="color:green;">it is possible to add, edit, remove, and deactivate rules, facilitating management and real-time monitoring.</mark>

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FdgwNaAq8gn5YhTPKVATr%2FScreenshot%202023-12-30%20at%2013.03.33.png?alt=media&amp;token=7b211f49-5527-44cc-89fa-b8b836c8fc80" alt=""><figcaption><p>Overview Dashboard Roles</p></figcaption></figure>

***

#### **Mind View:**&#x20;

Mind View presents <mark style="color:green;">an intuitive visual interface for the correlation between the structure of monitored data sources and the types of events detected during the threat hunting process.</mark> Allowing the visualization of the correlation rules registered in the environment. Through this visualization, it is possible to identify gaps resulting from the absence of correlation rules, preventing relevant incidents from going unnoticed.&#x20;

<mark style="color:green;">In the context of MSPs, Mind View plays a critical role, becoming a valuable deliverable for customers.</mark>

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FYpL4036U4XeAenUT8CSz%2FScreenshot%202023-12-30%20at%2013.04.49.png?alt=media&amp;token=50199360-7f1d-4154-8ecf-b0fa369e98b5" alt=""><figcaption><p>Overview Mind View</p></figcaption></figure>

***


# Main

It is the <mark style="color:green;">first stage for create</mark> a rule correlation.

***

### **Identification**

**ID:** Each rule is automatically identified by an ID, which [<mark style="color:green;">is generated according to the prefix set during the MSP configuration.</mark>](/system-settings/configuring-the-mss/configuring-the-msps-profile#rule-identification-code)

**Language:** The system <mark style="color:green;">allows versions in different languages within the same profile</mark>, providing a customized consultation according to the user's language preference.

**Name:** Serves for the direct <mark style="color:green;">identification of the rule</mark>.

**Attack:** <mark style="color:green;">Defines the attack vector</mark> that the rule aims to prevent or mitigate.

{% hint style="info" %}
The name and attack fields are essential for integration with systems like ChatGPT, facilitating the automatic filling of playbooks and rule details.
{% endhint %}

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FkPDuI8Lf97qXeB6S2ni3%2FScreenshot%202023-12-30%20at%2013.28.10.png?alt=media&amp;token=e2afcd69-c484-4bf7-bb97-3c0810abfc29" alt=""><figcaption><p>Identification Stage</p></figcaption></figure>

***

### **Data Source**

**Data Source:** <mark style="color:green;">Identifies the data source</mark> of the selected correlation rule.

**Event Type:** There are two main types of events in information security:

* **Security Intelligence Events:** Associated with data sources that have security intelligence (e.g., endpoint protection or application firewalls) and are usually linked to specific threats. These <mark style="color:green;">do not require complex correlation rules for anomaly identification.</mark>
* **Non-Security Intelligence Events:** Related to data sources without security intelligence (e.g., operating systems), which <mark style="color:green;">require more complex correlation rules.</mark> In these cases, the analyst must create custom event types for these data sources.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FtHhTcEj1pEMFClLP5rP6%2FScreenshot%202023-12-30%20at%2013.28.23.png?alt=media&amp;token=dd75b0a2-dc1e-4236-8a9b-1a013e8799df" alt=""><figcaption><p>Data Source Stage</p></figcaption></figure>

***

### **Integration**

<mark style="color:green;">It is possible to prepare the rule for one or more monitoring solutions.</mark> The selection of vendors directly impacts the listing of relationships and grouping rules (grouping rules).

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FHXsJHbguFK2Lw8EtoD0G%2FScreenshot%202023-12-30%20at%2013.28.41.png?alt=media&amp;token=183157a9-85d5-4b9d-8f40-09b71243ce34" alt=""><figcaption><p>Integration Stage</p></figcaption></figure>

***

### **Relations**

This functionality provides the system with <mark style="color:green;">information about which SIEM rule relates to the correlation rule.</mark> This allows for more efficient management and an integrated view of security policies.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FLDTqmyrbfbT5Odv9oAmv%2FScreenshot%202023-12-30%20at%2013.29.49.png?alt=media&amp;token=f30c5bdd-60c7-4eee-8d87-fd2a38ee6e16" alt=""><figcaption><p>Relations Stage</p></figcaption></figure>

***


# Monitoring Systems

### **Rule Profile**

Offers the <mark style="color:green;">ability to customize rules according to the specific needs of the company using the service.</mark> This customization ensures that the rule is aligned with the operational and security requirements of the organization.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FavYp5mSpIMIMC34gJJM5%2FScreenshot%202023-12-30%20at%2013.45.57.png?alt=media&amp;token=3fa938c3-1d9e-4e6a-af57-b4b48284f412" alt="" width="375"><figcaption><p>Rule Profile Management</p></figcaption></figure>

***

### **Documentation**

**Description**: <mark style="color:green;">specific details of the applicability of the correlation rule.</mark>

**CVSS (Common Vulnerability Scoring System):** an open standard for assessing the severity of security vulnerabilities in information systems. <mark style="color:green;">It provides a numerical score that reflects the severity of the vulnerability based on various criteria, such as impact and ease of exploitation.</mark> Integrating CVSS into monitoring systems helps prioritize responses to potential threats.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FwIQgj2po172unjCVSTKf%2FScreenshot%202023-12-30%20at%2013.46.13.png?alt=media&amp;token=df1f32cb-ba03-4ea8-9631-297b4aa3592e" alt=""><figcaption><p>Documentation Stage</p></figcaption></figure>

***

### Monitoring System Profiles

<mark style="color:green;">It is possible to create specific monitoring system profiles</mark> that can later be used to configure the details of each client company.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FHQcQXtv8Xpk3xq5gxEWc%2FScreenshot%202023-12-30%20at%2013.47.11.png?alt=media&amp;token=fc144a0f-2c61-474d-918e-829a52a53d4e" alt="" width="375"><figcaption><p>Monitoring System Profile Management</p></figcaption></figure>

***

**Vendors**

<mark style="color:green;">Documents all the details of the SIEM correlation rules from different suppliers.</mark> The configuration for each SIEM vendor is done in such a way as to directly reflect the internal configurations of the SIEM. This allows for precise and effective integration between the monitoring system and the specific solutions of each vendor.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2Fk8HM9y40f0EquS3ztjK5%2FScreenshot%202023-12-30%20at%2013.50.38.png?alt=media&amp;token=8722c6a5-e02c-45cd-af01-84580f0715cc" alt=""><figcaption><p>Vendors Stage</p></figcaption></figure>

***


# Rule Details

### **Incident Description**

**Incident Description:** a designated space to <mark style="color:green;">insert the description of the incident</mark> that will be opened by this correlation rule.

**Disable Alert Grouping:** This option, <mark style="color:green;">when activated, instructs Inopli to open an independent incident for each unique value identified in the grouping field</mark>. If this option is deactivated, Inopli will identify multiple attackers responsible for the same incident and group them together.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FFZCvDpC6hz6Tw0alAYOQ%2FScreenshot%202023-12-30%20at%2014.11.42.png?alt=media&amp;token=f5b68007-6e9f-43d5-8a4c-ef6d2f8f764c" alt=""><figcaption><p>Incident Description Stage</p></figcaption></figure>

***

### **Grouping**

Extremely necessary for the activation of the rule. <mark style="color:green;">It determines which field is necessary for Inopli to use in the treatment process</mark>, usually the field identifying the origin of the attack, with the possibility of configuring one or more for each SIEM.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F5GvVDjRGqqnwSotKhvLV%2FScreenshot%202023-12-30%20at%2014.12.06.png?alt=media&amp;token=600a24c2-27e5-4e84-a6a5-8504008c71dd" alt=""><figcaption><p>Grouping Stage</p></figcaption></figure>

***


# Mitre Techniques

It is possible to <mark style="color:green;">link specific techniques and/or sub-techniques to a correlation rule</mark>, enabling the mapping and indicators of security coverage.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2Fc9oFCU8ISQFE9tDZ5OPJ%2FScreenshot%202023-12-30%20at%2014.15.15.png?alt=media&amp;token=2ea733c8-1e4a-4793-81fb-03363ce0f170" alt=""><figcaption><p>Mitre Techniques Stage</p></figcaption></figure>

***


# Playbooks

The dashboard integrates with the correlation rules, providing management of responses to security incidents. Through a paginated list, the <mark style="color:green;">dashboard allows for the addition, editing, deletion, and activation of playbooks in an intuitive and organized manner.</mark>

The ability to activate or deactivate playbooks as needed ensures that responses to incidents are prompt.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FFtn40RnZXN5nzz9xTx9q%2FScreenshot%202023-12-30%20at%2014.41.13.png?alt=media&amp;token=eb250bed-b409-4538-8303-8021a6e13357" alt=""><figcaption><p>Overview Playbooks Dashboard</p></figcaption></figure>

***

## Creating a Playbook

### Identification

* **Nome:** Must be <mark style="color:green;">descriptive, clearly</mark> reflecting the purpose and scope of the playbook.
* **Visibilidade:**&#x20;
  1. **DEFAULT:** This category includes <mark style="color:green;">general use playbooks</mark>. They are designed to be applicable in a wide range of scenarios and companies.
  2. **ADVANCED:** Playbooks in this category are <mark style="color:green;">customized for the specific needs of a company</mark>. They are detailed and focused on particular scenarios, reflecting the policies, infrastructure, and specific security risks of the company.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F1FKRhUHMBKCmSA3EVXtS%2FScreenshot%202023-12-30%20at%2014.43.19.png?alt=media&amp;token=e7172801-9cfa-4d7f-841e-5f059d127e6f" alt=""><figcaption><p>Identification Stage</p></figcaption></figure>

***

### Phases of Incident Response

<mark style="color:green;">It is possible to manage treatment steps for each of the incident response phases</mark>, as outlined by the most renowned market frameworks, with the possibility of assigning the responsibility of the stage to the MSP or the company.&#x20;

The stages are:&#x20;

1. **Preparation:** <mark style="color:green;">Prepare the incident response team</mark> to efficiently deal with potential threats. (E.g., Team training, creation and updating of documentation).&#x20;
2. **Identification:** The first active response stage, where the <mark style="color:green;">veracity of the incident is determined</mark>. Detailed analysis to confirm whether the incident is a false positive or a real threat.&#x20;
3. **Containment:** Implemented only if the incident is confirmed. Execute <mark style="color:green;">measures to prevent the spread of the threat</mark> (e.g., isolation of systems or network segmentation).&#x20;
4. **Eradication:** <mark style="color:green;">Identify and eliminate the root cause of the incident</mark> (e.g., Removal of malware, correction of vulnerabilities, and strengthening of security controls).&#x20;
5. **Recovery:** Take the necessary <mark style="color:green;">measures to return the environment to normal operation</mark> (e.g., Verification of system integrity, data restoration from backups, and post-recovery monitoring).

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FdRZMf9P4YyEJoYWYdLZJ%2FScreenshot%202023-12-30%20at%2014.58.33.png?alt=media&amp;token=eeb23f23-c3c9-4ca4-9b83-1a1456757b3a" alt=""><figcaption><p>Phase of Incident Response Example</p></figcaption></figure>

***

### Lessons Learned

Reserved space <mark style="color:green;">to describe strategies in the post-incident analysis to identify improvements</mark> in the playbook and security practices.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FKb8gCz1BMJVSrNdjcacv%2FScreenshot%202023-12-30%20at%2015.04.31.png?alt=media&amp;token=607bef25-25a2-4a59-935a-47ea9b338ad6" alt=""><figcaption><p>Lessons Learned Stage</p></figcaption></figure>

***

### Comments

Space for the security team <mark style="color:green;">to leave notes and important observations about the playbook.</mark>

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2Fa4TIq6EAG3EVo7F1LMc7%2FScreenshot%202023-12-30%20at%2015.03.58.png?alt=media&amp;token=abe2ec0a-aea3-43fe-a9a7-de06f9af06cc" alt=""><figcaption><p>Comments Stage</p></figcaption></figure>

***

### Versioning

Space to <mark style="color:green;">document the revision with each update of the playbook</mark>, providing a detailed history and an audit trail.

{% hint style="danger" %}
Whenever the playbook is updated, it is necessary to provide a description of the new version.
{% endhint %}

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F0RO7pGgat8D4uwK8kqNq%2FScreenshot%202023-12-30%20at%2015.04.43.png?alt=media&amp;token=8b6abb02-cbf7-44b6-81bd-d40f1e9f4088" alt=""><figcaption><p>Versioning Stage</p></figcaption></figure>

***


# Companies

<mark style="color:green;">It is possible to activate rules for specific companies tailored to their needs.</mark> Each company can select one or more 'Rule Profiles' and 'Monitoring System Profiles' that align with their security policies and operational needs. There is also the option to apply one or more whitelists or blacklists for each company.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F4sN4PIPMC0AKA6SkA7d7%2FScreenshot%202023-12-30%20at%2014.30.07.png?alt=media&amp;token=8c7fcda7-fcc0-417c-bf9f-77117b560ea2" alt=""><figcaption><p>Companies Stage</p></figcaption></figure>

***


# Knowledge Lists

Knowledge Lists are essential for <mark style="color:green;">enhancing the processing of the alert engine, aiming to reduce false positives in an advanced and customized manner.</mark> In the user interface, it's possible to add, edit, filter, delete, and activate conditions as needed.&#x20;

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FZAQmfr4nbPujmJ14GQDy%2FScreenshot%202023-12-30%20at%2010.54.12.png?alt=media&amp;token=276b068b-8d89-463f-b0e7-9006f022ce17" alt=""><figcaption><p>Overview Knowledge Lists</p></figcaption></figure>

***

### White List

Prioritized in the handling of alerts, its purpose is to filter the information contained in the alerts. I<mark style="color:green;">f an alert triggers a mechanism defined in the White List, it will be processed,</mark> otherwise, it will be discarded. This helps in identifying legitimate events, reducing interruptions caused by false alerts.

***

### Black List

Used to eliminate alerts that trigger any of its mechanisms. <mark style="color:green;">This list is effective in discarding alerts associated with events already known to be non-threatening or irrelevant,</mark> optimizing the efficiency of the monitoring system.

***

### Creating a List

Both lists follow same creation process, with a form that includes <mark style="color:green;">a name, description, and a list of entries</mark>, which can be managed independently.&#x20;

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2Fy9srjJ5TMxCxG1WD5NdW%2FScreenshot%202023-12-30%20at%2010.53.42.png?alt=media&amp;token=da206c72-0540-405c-bed9-ba7c3110af41" alt=""><figcaption><p>Creating a List</p></figcaption></figure>

Each entry must contain:

* Name: Identifies the entry.&#x20;
* Monitoring System: Defines which Security Information and Event Management (SIEM) system the rules will be applied to.&#x20;
* Check All: Enables the identification of the value in any field within the alert payload. If deactivated, the identification follows the key-value rule.&#x20;
* Regex: If activated, it detects patterns based on regular expressions in the alert payload; if deactivated, it can search for plain text.&#x20;
* It is possible to add key-value fields to create validation groups using logical operators (and/or), thus establishing a boolean rule scheme.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FI8NHcl9aOQ3JoPm68leG%2FScreenshot%202023-12-30%20at%2010.53.24.png?alt=media&amp;token=7ceeb915-a3c9-4bf6-a029-46cb19395b2e" alt=""><figcaption><p>Creating an Entry</p></figcaption></figure>

For the lists to be effective, [<mark style="color:green;">they need to be linked to a correlation rule in the "Companies" tab during rule editing.</mark>](/response/rules/companies) This link ensures that the knowledge lists are applied appropriately.


# Managing MITRE

The MITRE ATT\&CK® (Adversarial Tactics, Techniques, and Common Knowledge) is a well-known <mark style="color:green;">global framework used for understanding and categorizing tactics, techniques, and procedures (TTPs) associated with cyber threats.</mark>

In Inopli, it is integrated into a dynamic and adaptable dashboard for security system administrators. This <mark style="color:green;">control panel offers an interactive interface,</mark> allowing administrative users to add or remove techniques and sub-techniques from the MITRE ATT\&CK framework. This functionality is crucial for keeping the system's database aligned with the latest strategies and changes in the cyber threat landscape.

When a new technique is added to the system through the dashboard, it becomes immediately available for use in various functions. This includes application in correlation rules, which are essential for detecting and responding to incidents. Additionally, the newly included technique is also <mark style="color:green;">integrated into the MITRE coverage indicator generator</mark>, to evaluate the effectiveness of the implemented security measures.

The inclusion of updated techniques and sub-techniques ensures an increase in security, as it allows administrators to keep up with emerging trends in cyber attacks.

This approach ensures that the team not only keeps its threat database updated, but also strengthens its ability to prevent, detect, and respond to security incidents more effectively.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FrhQKSutJIoaPwWs1trrW%2FScreenshot%202023-12-30%20at%2010.16.34.png?alt=media&amp;token=8f8db67b-526f-471b-8456-98daa0c464cf" alt=""><figcaption><p>Overview MITRE Att&#x26;ack Matrix</p></figcaption></figure>

***

### Creating a Technique

To <mark style="color:green;">ensure that the documentation always remains up-to-date</mark>, the team has the ability to add new techniques and/or sub-techniques, as well as to delete those that are no longer necessary. In the addition process, a detailed form is used, in which <mark style="color:green;">all essential information is requested for the accurate mapping of a new technique, sub-technique, and its respective version</mark>. This procedure ensures that each entry is complete, thus facilitating the management and location of information within the system.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FNhnSMOl1zWcBYIelAXND%2FScreenshot%202023-12-30%20at%2010.30.41.png?alt=media&amp;token=83738b32-88f3-49d3-af5c-aeff23b4ecce" alt=""><figcaption><p>Create a Technique</p></figcaption></figure>

***


# Incidents

The incidents reflect events that, after being processed, generate alerts and are linked to specific correlation rules. In the initial dashboard, <mark style="color:green;">a graph displays the incidents opened in the last 24 hours by severity</mark>, as well as a general overview of the incident status and a paginated list.

Users can filter incidents by severity, responsible analyst, status, creation date, update date, or search by the name or ID of the incident. <mark style="color:green;">The default view lists urgent incidents in an optimized manner, without predefined filters or sort orders.</mark>

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F58rds81O1C2n13YB5obp%2Foverview-incidents.gif?alt=media&amp;token=24c2cb49-39e6-4623-b8cf-0a3a9180485f" alt=""><figcaption><p>Overview Incidents Dashboard</p></figcaption></figure>

{% hint style="warning" %}
The prioritization in the list follows a standard: incidents with 'NEW' status and the shortest remaining SLA time are shown first, followed by those that had interactions with Mss/Company, and finally, the rest are listed by ID in descending order.
{% endhint %}

A color palette indicates special situations:

* Red: SLA exceeded.
* Yellow: SLA 1 hour about to be exceeded.
* Green: Incident with a new unread interaction.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FZw6qkrKAszdpp0XHfSHv%2FScreenshot%202023-12-18%20at%2022.33.54.png?alt=media&amp;token=cd68f65d-fe8c-4db5-9420-9eaf41006cf4" alt=""><figcaption><p>Incident Table Order</p></figcaption></figure>

***

#### **Important columns into dashboard include:**

* SLA: The time agreed with the client, which stops counting when the incident is addressed.
* Severity: Organized from INFO to CRITICAL, according to the parent correlation rule.
* Status: Indicates the stage of resolution, varying from active, pending, under treatment, and closed.
* Rate: The average user feedback, based on various parameters.

***

#### Available actions into dashbord:

* Escalate Incident: Increases the incident's priority in the list, reducing the SLA.
* [<mark style="color:green;">Alerts</mark>](/response/incidents/alerts): Displays all the alerts that led to the incident.
* [<mark style="color:green;">Messages</mark>](/response/incidents/messages): Allows analysts to follow and participate in the resolution process, sending messages and files, and includes system messages about changes in the incident.
* [<mark style="color:green;">Rate</mark>](/response/incidents/rate): Displays feedback for each analyst involved.

***

### Incident Details

Presents important information, links, message history, and activities related to the incident, allowing individual or mass changes in various parameters.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2Ftxdp58szDA9lrk9ZAYmn%2FScreenshot%202023-12-18%20at%2022.38.30.png?alt=media&amp;token=fa985fe2-27b2-4194-b003-84ee6c80b4be" alt="" width="162"><figcaption><p>Incident Details</p></figcaption></figure>

{% content-ref url="/pages/nYykzOSxr93bxfVOZi15" %}
[Alerts](/response/incidents/alerts)
{% endcontent-ref %}

{% content-ref url="/pages/m0oNicfjqfB5lp8ULeIy" %}
[Messages](/response/incidents/messages)
{% endcontent-ref %}

{% content-ref url="/pages/OL60S6SBanae7JG2O7Wy" %}
[History](/response/incidents/history)
{% endcontent-ref %}

{% content-ref url="/pages/eft3Y28tOoDXTxfvkBvk" %}
[Playbooks](/response/incidents/playbooks)
{% endcontent-ref %}

{% content-ref url="/pages/GQ4GQ6IueU8FdATB4uWj" %}
[Rules](/response/incidents/rules)
{% endcontent-ref %}

***


# Alerts

<mark style="color:green;">All alerts that originated the specific incident are listed</mark>, allowing searches for parts of the payload and enabling quick and practical viewing of it.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2Fuyws2bxJL3KGp0SmZbTZ%2FScreenshot%202023-12-18%20at%2022.39.46.png?alt=media&amp;token=730269c4-4b32-4ec0-997b-ce8d96ca7231" alt=""><figcaption><p>List of Alerts By Incident</p></figcaption></figure>

***


# Messages

This functionality is used for <mark style="color:green;">communication between analysts and clients</mark>. It <mark style="color:green;">enables file attachments</mark> and <mark style="color:green;">tracking of the incident's change history through automatically generated messages</mark>. Searches can be conducted for parts of the message or the user's name. Additionally, the status can be changed to AWAITING SERVICE when a response is required to resolve the incident.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FPcWHMInenGnngHyF31Gz%2FScreenshot%202023-12-18%20at%2022.40.20.png?alt=media&amp;token=a13ffef8-9210-430b-9eb8-30d32b107724" alt=""><figcaption><p>List of Messages Into Incidents Page</p></figcaption></figure>

***


# History

This tool <mark style="color:green;">facilitates communication between analysts</mark> at the end of shifts or <mark style="color:green;">during the handover of responsibilities</mark>, providing essential context to the new person in charge of the incident.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FLQ2BBWvqkRTMYXcnRSJG%2FScreenshot%202023-12-18%20at%2022.40.54.png?alt=media&amp;token=17e7c845-696a-4f88-813c-afa13af0076d" alt=""><figcaption><p>Activity History Into Incidents Page</p></figcaption></figure>

***


# Rate

After an incident is completed, <mark style="color:green;">it's possible to provide feedback to the responsible analysts</mark>, with options for detailed viewing and evaluation by both Mss users and Company clients.

<mark style="color:green;">The rate is between 1-5 points.</mark>

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FlbFzynpah95tpXku4Pjc%2FScreenshot%202023-12-18%20at%2022.42.01.png?alt=media&amp;token=4aa35a55-0bff-48b6-83e4-b73aab4bb411" alt=""><figcaption><p>Feedback Users</p></figcaption></figure>

***


# Playbooks

Users can view all the <mark style="color:green;">playbooks applicable to resolving the incident</mark>, accessing their versions and downloading the necessary documentation.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FRtwopVt9kjUc3zhYwCdF%2FScreenshot%202023-12-18%20at%2022.41.09.png?alt=media&amp;token=e2a0ae8d-3c81-4411-b1de-1ba447fc69c2" alt=""><figcaption></figcaption></figure>

***


# Rules

<mark style="color:green;">The correlation rule that defines the open incident</mark> is presented clearly, including a summary of the profile and the most relevant information of the rule.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FhJLwySuywFB4JJte8Hy3%2FScreenshot%202023-12-18%20at%2022.41.24.png?alt=media&amp;token=37529730-97a8-403d-958e-883301a42e51" alt=""><figcaption></figcaption></figure>

***


# Requests

Users categorized as 'company' <mark style="color:green;">make requests directed to 'mss' type users</mark>, following a process defined by 'mss' itself. Once created, the <mark style="color:green;">requests are organized in a paginated list</mark>, prioritized according to established criteria. Additionally, there are filtering and sorting options to facilitate the management of these requests. On the home screen, users <mark style="color:green;">can also view a control panel that displays the current status of the treatment of each request</mark>, allowing for efficient and organized monitoring.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FjLoxGO33GkYkdSeUWm56%2FScreenshot%202023-12-20%20at%2020.18.50.png?alt=media&amp;token=c22c0a96-5672-413a-a7d2-2801d1b73e95" alt=""><figcaption><p>Overview Requests Dashboard</p></figcaption></figure>

{% hint style="warning" %}
The prioritization in the list follows a standard: requests with 'NEW' status and the shortest remaining SLA time are shown first, followed by those that had interactions with Mss/Company, and finally, the rest are listed by ID in descending order.
{% endhint %}

A color palette indicates special situations:

* Red: SLA exceeded.
* Yellow: SLA 1 hour about to be exceeded.
* Green: Incident with a new unread interaction.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F2h8iMU0XVmwTtWjRU7jg%2FScreenshot%202023-12-20%20at%2020.19.38.png?alt=media&amp;token=7b2fd892-6e10-46ba-b259-ce12e0bb02e8" alt=""><figcaption><p>Request Table Order</p></figcaption></figure>

***

#### **Important columns into dashboard include:**

* SLA: The time agreed with the client, which stops counting when the incident is addressed.
* Criticality: Organized from LOW to CRITICAL, according to the parent correlation rule.
* Status: Indicates the stage of resolution, varying from active, pending, under treatment, and closed.
* Rate: The average user feedback, based on various parameters.

***

#### Available actions into dashbord:

* Escalate Request: Increases the request's priority in the list, reducing the SLA.
* [<mark style="color:green;">Messages</mark>](/response/incidents/messages): Allows analysts to follow and participate in the resolution process, sending messages and files, and includes system messages about changes in the request.
* [<mark style="color:green;">Rate</mark>](/response/incidents/rate): Displays feedback for each analyst involved.

***

### Request Details

Presents important information, links, message history, and activities related to the resquest, allowing individual or mass changes in various parameters.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FeYvPfW0zp0oEzX5u1Ww4%2FScreenshot%202023-12-20%20at%2020.34.40.png?alt=media&amp;token=5b13b35f-801b-4da3-bd3e-742cbf7397f5" alt="" width="305"><figcaption><p>Request Details</p></figcaption></figure>

{% content-ref url="/pages/m0oNicfjqfB5lp8ULeIy" %}
[Messages](/response/incidents/messages)
{% endcontent-ref %}

{% content-ref url="/pages/OL60S6SBanae7JG2O7Wy" %}
[History](/response/incidents/history)
{% endcontent-ref %}

***


# Dashboards


# Operational Dashboard

The operational dashboard, <mark style="color:green;">available to 'company' and 'mss' type users</mark>, provides up-to-date and detailed information about incidents and requests, facilitating real-time operational monitoring without the need for date filters.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FnAQNDBGzbndlJo0B1BWG%2FScreenshot%202023-12-20%20at%2021.58.42.png?alt=media&amp;token=f614a5d8-561a-4c10-b8e7-72e480c65954" alt=""><figcaption><p>Overview Operational Dashboard</p></figcaption></figure>

***

### **General Information**

* **Total Incidents/Requests:** Displays the total number of incidents and requests recorded in the system.
* **Average Resolution Time:** Calculates the average time from the creation of the incident to its closure.
* **Idle Time Between Messages:** Shows the time interval between sending a message and receiving a response.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F6F0sisgDrSBO6wpsLYky%2FScreenshot%202023-12-20%20at%2021.58.54.png?alt=media&amp;token=2792ac36-d600-45da-8f17-fdce68f80d3b" alt=""><figcaption><p>General Information</p></figcaption></figure>

***

### Incidents/Requests by Status

Presents the distribution of incidents and requests by different statuses.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2Fzz02nQJ26N7uypZs0TFY%2FScreenshot%202023-12-20%20at%2021.59.06.png?alt=media&amp;token=86983ac2-afc9-4bc4-b436-ac9b78976ce5" alt=""><figcaption><p>Incidents/Requests by Status</p></figcaption></figure>

***

### **Recent Incidents/Requests**

Lists the most recent incidents and requests in the system.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FrWdSZ0jASyb1ylRRdwcI%2FScreenshot%202023-12-20%20at%2021.59.20.png?alt=media&amp;token=bad4a067-d767-4748-94ae-4318cf69c60d" alt="" width="148"><figcaption><p>Recent Incidents/Requests</p></figcaption></figure>

***

### Incidents/Requests Queue

Organizes, by order of priority, the incidents and requests with 'NEW' status.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F0wHluqdSMwJouGG49wT8%2FScreenshot%202023-12-20%20at%2021.59.51.png?alt=media&amp;token=5bf2a05b-3460-4dc3-8638-b5cc69b9c753" alt="" width="146"><figcaption><p>Incidents/Requests Queue</p></figcaption></figure>

***

### General Chart

Visually represents the severity and status of incidents/requests received in the last 24 hours.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F6VT0akNUEM57xksnQhbv%2FScreenshot%202023-12-20%20at%2021.59.36.png?alt=media&amp;token=9b599b76-b7f5-4204-a0cb-a24ff3897cb3" alt=""><figcaption><p>General Chart</p></figcaption></figure>

***

### Treatment by Severity

Groups information of incidents/requests by severity and treatment status.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F7s3eC75sDlNQ3VmoFxdG%2FScreenshot%202023-12-20%20at%2022.00.16.png?alt=media&amp;token=dcf8a3a7-450e-4f57-ac6a-fd65c1e610d7" alt="" width="363"><figcaption><p>Treatment by Severity</p></figcaption></figure>

***

### Responsibility by Severity

Summarizes incidents/requests by severity and current responsible party.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F8dYiUwJADPsJyFPYkMk5%2FScreenshot%202023-12-20%20at%2022.00.23.png?alt=media&amp;token=936d45b5-3234-4aea-9767-cbdaa1796d42" alt="" width="363"><figcaption><p>Responsibility by Severity</p></figcaption></figure>

***

### Interactions Waiting for Response

Lists incidents/requests that are marked as 'waiting for response', from the oldest to the most recent, including the waiting time in the queue.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FxlNAkgZYtt73EnQBMiP4%2FScreenshot%202023-12-20%20at%2022.16.53.png?alt=media&amp;token=4634572b-ec27-4f83-bbf9-727d0a1537d8" alt="" width="293"><figcaption><p>Interactions Waiting for Response</p></figcaption></figure>

***

### Analysts by Availability

Displays the online/offline status of analysts linked to 'mss/company' users accessing the dashboard.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FB8gQJro5TcStHnka3U5q%2FScreenshot%202023-12-20%20at%2022.00.05.png?alt=media&amp;token=5e457a36-4654-4602-b1c6-bf262d07cb29" alt="" width="369"><figcaption><p>Analysts by Availability</p></figcaption></figure>

***


# Executive Dashboard

This dashboard, <mark style="color:green;">accessible to MSS or company type users</mark>, offers detailed <mark style="color:green;">indicators on system health and alert processing</mark>, with the ability to filter by date ranges. It provides a comprehensive overview of the main aspects of security and operational efficiency.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FL7BTvSOYeEGOg0M6cTDz%2FScreenshot%202023-12-26%20at%2019.15.40.png?alt=media&amp;token=8a1748bd-f5a8-4572-93b8-82d68b9f1f7a" alt=""><figcaption><p>Overview Executive Dashboard</p></figcaption></figure>

***

#### **Overall Health**

Indicates, in a scaled format, the overall average of Info Security, Risk Exposure, Maturity, and Mitre indicators.&#x20;

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FnIEK3kvNIdEhKKC2Ymwg%2FScreenshot%202023-12-26%20at%2020.10.34.png?alt=media&amp;token=5d986962-b4ed-4fd9-9688-ea8ff3538976" alt="" width="375"><figcaption><p><strong>Info Security</strong></p></figcaption></figure>

***

#### **Info Security**

Average of coverage indicators for relations, event types, and private playbooks.&#x20;

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FrN1pYzZ1ospFqgJn8RI7%2FScreenshot%202023-12-26%20at%2020.10.46.png?alt=media&amp;token=40589608-5a73-4266-b90a-04e2c61d51dd" alt="" width="197"><figcaption><p>Info Security</p></figcaption></figure>

***

#### **Risk Exposure**

Checks the coverage of the time for first treatment, measuring its compliance with the standards set in the setup. The closer to 0%, the better the indicator.&#x20;

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FaeJyreD8AeZCXUIHALCl%2FScreenshot%202023-12-26%20at%2020.10.54.png?alt=media&amp;token=051ddabf-445c-4ce9-be95-12b47d752b94" alt="" width="197"><figcaption><p>Risk Exposure</p></figcaption></figure>

***

#### **Maturity**

Average of indicators in the Security Operation graph, rated on a scale of up to 5 points.&#x20;

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FPbbaOc2Vqm1YBNF58Tpn%2FScreenshot%202023-12-26%20at%2020.11.02.png?alt=media&amp;token=da87b7ef-088a-465f-a883-ae2d839f5a03" alt="" width="197"><figcaption><p>Maturity</p></figcaption></figure>

***

#### **Mitre**

Calculates the coverage of correlation rules for techniques and sub-techniques listed in Mitre.&#x20;

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F4UkSHdslCFuVoAbvZgMO%2FScreenshot%202023-12-26%20at%2020.11.10.png?alt=media&amp;token=4235896f-d3dc-4708-9597-85a2b7e8df4e" alt="" width="197"><figcaption><p>Mitre</p></figcaption></figure>

***

#### **Attack Vector**

Visual representation of the treatment of events by data source, their attack vectors, and related results in the confusion matrix.&#x20;

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FhwqDJHW1mUEouvAQY9gk%2FScreenshot%202023-12-26%20at%2019.16.38.png?alt=media&amp;token=c5fdf5ed-06e7-413d-b750-fdc78b1d3aad" alt=""><figcaption><p>Attack Vector</p></figcaption></figure>

***

#### Events x Incidents

Visual representation of confirmed incidents, arising from events received by the monitoring system, demonstrating effectiveness in reducing manual labor.&#x20;

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F5Z3DqSHCAMECmg5VeoEp%2FScreenshot%202023-12-26%20at%2019.17.08.png?alt=media&amp;token=4c8cb1f0-dddc-4bfc-b380-2f0d8c026660" alt="" width="563"><figcaption><p>Events x Incidents</p></figcaption></figure>

***

#### Quality KPIs:&#x20;

* Average Time To Detect An Incident (MTTD): The average time to identify an incident from the generation of the alert.&#x20;
* Average Time To Respond To An Incident (MTTR): A performance indicator of the security team measuring the time from the opening of the incident to the start of treatment.&#x20;
* Average Time To Contain An Incident (MTTC): The time it takes the team from identification to the start of the threat blocking phase.&#x20;
* Average Time To Repair (MTTR): The time required to fix the problems and eradicate the threat, returning the environment to a safe state.&#x20;

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FVvgvmzjmkzqjHGANzUMR%2FScreenshot%202023-12-26%20at%2019.17.26.png?alt=media&amp;token=8854fc97-9459-4df1-8406-4163c342e5e1" alt="" width="563"><figcaption><p>Quality KPIs</p></figcaption></figure>

***

#### Incidents By Status

Number of incidents distributed by each type of status.&#x20;

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F9X0O3Lg8YuUtKScoFtg3%2FScreenshot%202023-12-26%20at%2019.17.56.png?alt=media&amp;token=35bf714a-ba6f-4179-a9de-3ceae95b7143" alt="" width="563"><figcaption><p>Incidents By Status</p></figcaption></figure>

***

#### Confusion Matrix

The number of alerts in each status of the confusion matrix.&#x20;

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FEqEZQcDFxZWrXPaBZe04%2FScreenshot%202023-12-26%20at%2019.18.10.png?alt=media&amp;token=622e3723-4972-4350-aa32-d38d4542b896" alt="" width="563"><figcaption><p>Confusion Matrix</p></figcaption></figure>

***

#### Security Operation

Visual representation, with a color rule, indicating the compliance level of various indicators, with descriptions available when hovering over their titles.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FRGpZvRXHDDp6T41h4Z6i%2FScreenshot%202023-12-26%20at%2019.59.38.png?alt=media&amp;token=876e84fd-bd43-46b7-aa37-36aabaf8e4a2" alt=""><figcaption><p>Security Operation</p></figcaption></figure>

* **Continuous Monitoring**
  * **Monitoring Systems**
    * **Relations:** Coverage of treatment of relations in the correlation rules.
  * **Data Sources**
    * **Correlation Rules:** Coverage if each event type is linked to at least one correlation rule.
  * **Mitre Framework**
    * **Tactics:** Coverage if each technique has at least one correlation rule.
    * **Techniques:** Coverage if there is at least one correlation rule linked to the technique.
* **Incident Response**
  * **Playbooks**
    * **Initial Playbooks:** Coverage if each correlation rule has at least one initial playbook.
    * **Advanced Playbooks:** Coverage if each active customer has at least one advanced type playbook.
  * **Continuous Operation**
    * **SLA:** Contracted SLA coverage percentage coverage.
    * **Quality of Service:** Maximum average rating coverage.
    * **Response Time:** Optimal response time coverage.
* **Customer Management**
  * **Continuous Operation**
    * **Requests:** Coverage of request processing, considering open/closed.
    * **SLA:** Contracted SLA coverage percentage coverage.
    * **Response Time:** Optimal response time coverage.
* **Automatic Response**
  * **Automatic Treatment Engine**
    * **First Response:** Mean Time To Treatment an Alert.
    * **Workload Reduction:** Workload Reduction in Percentage.

{% hint style="warning" %}
**Color Standards for Performance Indicators:**

* **Green (Excellent Performance):** Indicates a performance that is equal to or greater than 90%. This green color standard is used to represent high efficiency or compliance, signifying that the indicator is operating at an optimal level.
* **Orange (Moderate Performance):** Represents a performance between 60% and 89.99%. The orange color is used for indicators that are performing moderately, suggesting there is room for improvement, but the performance is still acceptable.
* **Red (Insufficient Performance):** Used for performances below 60%. The red color alerts to an unsatisfactory performance, indicating that the indicator is below an acceptable level and needs immediate attention for improvement.
* **Gray (Inactive):** Applied to indicators that are currently inactive. The gray color signals that the indicator is not in use or does not have sufficient data for performance evaluation at the moment.
  {% endhint %}

***


# KPIs Dashboard

This dashboard efficiently <mark style="color:green;">compiles key performance indicators (KPIs)</mark>, focusing on engine performance and team productivity. Available for <mark style="color:green;">MSS and Company users,</mark> it offers <mark style="color:green;">date filters for detailed analysis</mark>.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FcycYABoLoJEKDy8Nnqu1%2FScreenshot%202023-12-27%20at%2021.23.13.png?alt=media&amp;token=badb9ed0-f606-4802-a162-de00f74f04be" alt=""><figcaption><p>Overview KPI's Dashboard</p></figcaption></figure>

***

#### Average Time To Detect An Incident (MTTD)

The average time to identify an incident from the generation of the alert.&#x20;

***

#### Average Time To Respond To An Incident (MTTR)

A performance indicator of the security team measuring the time from the opening of the incident to the start of treatment.&#x20;

***

#### Average Time To Contain An Incident (MTTC)

The time it takes the team from identification to the start of the threat blocking phase.&#x20;

***

#### Average Time To Repair (MTTR)

The time required to fix the problems and eradicate the threat, returning the environment to a safe state.&#x20;

***

#### **SLA (Service Level Agreement)**

Displays the percentage of services delivered within the [<mark style="color:green;">contracted SLA</mark> ](/system-settings/managing-companies/configuring-the-companys-profile#sla)parameters.&#x20;

***

#### Workload Reduction

Shows the percentage of workload reduction, comparing alerts processed by the initial engine with generated incidents.&#x20;

***

#### Incident Response Procedure

Indicates the number of advanced playbooks registered in the system.

***

#### Procedure Compliance

Compares the total number of rules with those having associated advanced playbooks.&#x20;

***

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FFQfjzpco1BMlVYhLNpFO%2FScreenshot%202023-12-27%20at%2021.23.41.png?alt=media&amp;token=8356d43a-27d9-497f-a1dc-79e7728b8fb4" alt=""><figcaption><p>General Indicators</p></figcaption></figure>

***

#### Monitoring System

A column chart displays the total number of alerts generated by the solution (SIEM), with a line highlighting the proportional workload reduction.&#x20;

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FLzQ90agd4sdq4BlLgzdj%2FScreenshot%202023-12-27%20at%2021.26.27.png?alt=media&amp;token=217c3029-4a1a-407a-8b6a-faaee8a13188" alt="" width="563"><figcaption></figcaption></figure>

***

#### Timeline

Automatically evaluates all incidents handled over a defined period (30 days or customized), indicating the average response time and related KPIs.&#x20;

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FZFSnWS2q0bniKN1e3Vf5%2FScreenshot%202023-12-27%20at%2021.27.43.png?alt=media&amp;token=319cd511-6922-4960-9ee9-a667fed94a07" alt="" width="563"><figcaption></figcaption></figure>

***

#### Data Sources

Each column in the chart represents a data source, contrasting the total received alerts with those that are actually relevant.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FqiDXXQ7z2wfHHMrsYCU6%2FScreenshot%202023-12-27%20at%2021.26.37.png?alt=media&amp;token=c04b1068-a320-4da5-816b-4b2d1e79fbd0" alt="" width="563"><figcaption></figcaption></figure>

***

[<mark style="color:green;">Confusion Matrix</mark>](/response/dashboards/alert-management-dashboard/confusion-matrix#confusion-matrix-indicators)

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2Fa1wWRGJswjqjmjySF1Gk%2FScreenshot%202023-12-27%20at%2021.27.08.png?alt=media&amp;token=e153b08e-2085-4eb8-9ce2-5155cc7a6c1a" alt=""><figcaption><p>Confusion Matrix</p></figcaption></figure>

***


# Alert Management Dashboard

This dashboard provides a comprehensive monitoring interface for system-generated alerts. It displays metrics for <mark style="color:green;">alerts generated over the past 24 hours</mark> and allows users to track the status of alert processing to pinpoint potential errors. <mark style="color:green;">Users can annotate alerts to highlight any anomalies and utilize the confusion matrix to identify false positives and true positives</mark>, thus assessing the accuracy of the alert generation system. The dashboard is designed to facilitate quick responses with an average alert treatment time prominently displayed, ensuring that issues can be addressed promptly.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2F41mTl6bh2gKCan9ybZ2M%2FScreenshot%202023-12-21%20at%2021.05.39.png?alt=media&amp;token=e341e034-c0a3-4dd9-9e02-43186e88647e" alt=""><figcaption><p>Dashboard Alert Management</p></figcaption></figure>

***

### Alert Details

Users can view the current processing status of each alert and <mark style="color:green;">examine the contents of the payload</mark>. Furthermore, it is possible to [<mark style="color:green;">adjust the classification in the confusion matrix</mark>](/response/dashboards/alert-management-dashboard/confusion-matrix) to refine the system's accuracy and <mark style="color:green;">add specific comments to each alert</mark>. Should an alert fail, the tool <mark style="color:green;">enables reprocessing</mark>, ensuring that none are lost or overlooked due to processing errors.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FgyGXBYrsYqYWhm3vYsSt%2FScreenshot%202023-12-21%20at%2021.08.55.png?alt=media&amp;token=22c73d63-2b9f-4250-9476-7b17be8e34e4" alt="" width="297"><figcaption><p>Alert Details</p></figcaption></figure>

***


# Confusion Matrix

<mark style="color:green;">"Machine learning"</mark> refers to advanced computational <mark style="color:green;">systems capable of performing automated analysis and decision-making based on artificial intelligence rules</mark>. These systems, programmed to identify patterns and detect anomalies, are essential in various applications, including information security.

In the context of our system, <mark style="color:green;">we have integrated an alert evaluation engine that uses machine learning</mark>. This integration enhances our ability to analyze and respond to security events efficiently. <mark style="color:green;">We use the confusion matrix to measure the effectiveness of this technology</mark>, a crucial tool in assessing the system's accuracy in correctly identifying specific events.

In information security, the confusion matrix is used to evaluate the efficiency of monitoring systems, which use Boolean algebra to automatically identify potential threats. These are then appropriately classified and managed. <mark style="color:green;">Commonly in information security, we emphasize the 'true positive' and 'false positive' parameters.</mark> True positives indicate real threats correctly identified by the system, while false positives represent erroneous alerts. <mark style="color:green;">In our application, we have fully implemented the confusion matrix, which improves quality and increases operational control.</mark> These indicators allow us to evaluate the accuracy and maturity of the correlation rules, contributing to the system's evolution.

<mark style="color:green;">In Inopli, the indicators for the alerts are generated automatically, given by monitoring the entire trajectory of the incident during its treatment.</mark> However, we also value flexibility and accuracy. Therefore, [<mark style="color:green;">we allow manual updates for each alert. In situations of inconsistencies, analysts can intervene, adding detailed comments that reflect the specific context and characteristics of the incident.</mark>](/response/dashboards/alert-management-dashboard#alert-details)

***

## **Confusion Matrix Indicators**

This matrix not only categorizes alerts into 'true positives' and 'false positives' but also incorporates other crucial parameters such as Accuracy, F1-Score, Precision, False Positive Rate (FPR), Recall, and False Negative Rate (FNR). [<mark style="color:green;">Each of these topics plays a vital role in the detailed analysis of the system's effectiveness:</mark>](/response/dashboards/kpis-dashboard)

* **Accuracy:** This indicator measures the proportion of correct predictions (both true positives and true negatives) relative to the total number of cases analyzed. It is a general measure of the system's effectiveness.
* **F1-Score:** This metric is the balance between Precision and Recall. It is particularly useful when classes are unbalanced. The F1-Score is the harmonic mean of Precision and Recall, providing a consolidated view of the system's performance.
* **Precision:** Refers to the proportion of true positives relative to the total number of cases classified as positive (true positives and false positives). This metric indicates the accuracy of the system's positive predictions.
* **False Positive Rate (FPR):** This index shows the proportion of false positives relative to the total number of actual negative cases. A high FPR can indicate many false alarms, a critical aspect in information security.
* **Recall (Sensitivity or True Positive Rate)**: Measures the proportion of true positives relative to the total number of actual positive cases (true positives and false negatives). It is a crucial metric to understand the system's ability to correctly identify threats.
* **False Negative Rate (FNR)**: Indicates the proportion of false negatives relative to the total number of actual positive cases. A high FNR can mean that the system is failing to detect real threats, a significant risk in information security.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FU9q8fz6GNvsVdi34gW3k%2FScreenshot%202023-12-23%20at%2011.22.01.png?alt=media&amp;token=c1564581-9c0e-4b1c-a849-8623de43a452" alt=""><figcaption><p>Indicators Into KPI's Dashboard</p></figcaption></figure>

By integrating these indicators, <mark style="color:green;">Inopli not only efficiently categorizes alerts but also offers a comprehensive view of the system's performance and reliability.</mark> These indicators are necessary for ongoing evaluation and improvement of security strategies, ensuring that the system maintains a high rate of accuracy and efficiency in detecting and treating security incidents.

***


# Custom Reports

The <mark style="color:$success;">**Custom Reports**</mark> feature allows MSSPs and end users to automatically extract structured data from Inopli, focusing on <mark style="color:$success;">**Incidents**</mark> and <mark style="color:$success;">**Requests**</mark>. It ensures full data portability, enabling the export of all relevant records from the platform whenever needed, supporting external analytics, billing, compliance, and audit purposes.

**What It Does**

* <mark style="color:$success;">**Automates data export**</mark>**:** schedules recurring reports so incident and request data is generated without manual CSV/Excel exports.
* <mark style="color:$success;">**Scopes the dataset**</mark>**:** lets you select the <mark style="color:$success;">**company**</mark> and **reference period** that should be included in each report.
* <mark style="color:$success;">**Defines frequency**</mark>**:** supports <mark style="color:$success;">**daily, weekly**</mark>, or <mark style="color:$success;">**monthly**</mark> generation at a specific time, aligning exports with operational and reporting routines.
* <mark style="color:$success;">**Notifies stakeholders**</mark>**:** sends a notification with the generated report to the configured recipients, using the chosen subject for easy identification.
* <mark style="color:$success;">**Controls the schema**</mark>**:** provides a column selector where you choose the <mark style="color:$success;">**type**</mark> (*Incidents* or *Requests*) and the fields to include, such as `id`, `name`, `severity_name`, `status_name`, `created_at`, `updated_at`, `sla_expiration_time`, and `closed_at`.

**How It Works**

* In <mark style="color:$success;">**Report Info**</mark>, activate the report, select the <mark style="color:$success;">**Company**</mark>, choose the <mark style="color:$success;">**Period**</mark> you want to export, and add a short <mark style="color:$success;">**Description**</mark> to identify the purpose of that report.
* In <mark style="color:$success;">**Frequency**</mark>, choose whether the report will run <mark style="color:$success;">**Daily, Weekly**</mark>, or <mark style="color:$success;">**Monthly**</mark>, and set the exact time (and day, when applicable) for generation.
* In <mark style="color:$success;">**Sent notification to**</mark>, define the <mark style="color:$success;">**Subject**</mark> and add the <mark style="color:$success;">**Recipients**</mark> who should be notified every time the report is generated.
* In <mark style="color:$success;">**Columns**</mark>, set the <mark style="color:$success;">**Type**</mark> (e.g., *Incidents*) and select the fields that will compose each row of the export, tailoring the dataset to the consuming system or audience.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FBcpoT5weNNvIE17GsyUT%2Fimage.png?alt=media&amp;token=25730ec9-9149-4765-9ca8-9bb4b1dd6253" alt=""><figcaption></figcaption></figure>

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FygcwXBUJn9Zl3rr13zt5%2Fimage.png?alt=media&amp;token=b04fc64b-c0af-4012-9ed6-b63f8b4b47a1" alt=""><figcaption></figcaption></figure>

**Why This Matters**

Because the exported data contains the <mark style="color:$success;">**entire treatment trail of incidents and requests**</mark>, each generated file can also serve as a <mark style="color:$success;">**complete audit trail export**</mark>, providing traceability over every recorded action, update, and resolution stage.

This capability ensures that operational data stored in Inopli does not remain locked inside the platform. By automating the export of incidents and requests with precise control over scope, frequency, and schema, organizations can integrate Inopli data into BI tools, client reporting, audit processes, and long-term records, maintaining full visibility and ownership over their security operations data.


# AI for Incident Analysis

Inopli Response incorporates native **Artificial Intelligence (AI)** capabilities designed to support and enhance the incident management lifecycle. The AI engine operates as an analytical layer that assists security analysts by evaluating alerts, correlating security signals, and providing contextual insights to support accurate and timely decision-making.

The primary role of the AI within Inopli Response is to perform a **first-level assessment** of alerts and security events. When alerts are received, the AI automatically analyzes related events, historical data, indicators of compromise (IOCs), and contextual attributes to assess relevance, severity, and potential impact. This assessment is generated before formal incident handling and is presented to analysts as a structured reference to guide investigation.

The AI engine correlates alerts with previous incidents, ongoing investigations, and known activity patterns. By linking related events through shared attributes such as hosts, users, sessions, and IOCs, the platform reduces alert noise and highlights meaningful security activity. This correlation capability supports faster triage and more efficient prioritization of incidents.

In addition to contextual correlation, the AI supports **behavioral and predictive analysis**. By continuously evaluating patterns and trends across security data, the AI identifies deviations from expected behavior that may indicate emerging threats or abnormal activity. This predictive capability enables early visibility into risks and supports proactive security operations.

AI-generated insights are fully integrated into the incident management workflow of Inopli Response. The AI does not replace analyst judgment, but augments it by providing consistent assessments, correlations, and analytical context. Analysts use these insights as a foundation for validation, escalation, and response actions, ensuring that decision-making remains controlled, transparent, and auditable.

By combining automated assessment, contextual correlation, and predictive analysis, Inopli Response delivers an AI-driven approach to incident analysis that improves efficiency, reduces false positives, and strengthens the overall effectiveness of security operations.


# Monitoring Catalog (Overview)

Digital Risk Protection (DRP) refers to the continuous monitoring of external digital environments to detect threats that could harm a company’s reputation, executives, brand, or exposed assets. It operates across the open web, deep/dark web, messaging platforms, forums, social media, and app stores seeking signs of impersonation, data leaks, credential exposures, fraud attempts, and other forms of digital risk. Unlike reactive tools that only alert once a breach is underway, DRP is designed to act upstream, flagging risks before they escalate, by identifying early signals in unstructured content such as posts, media files, domains, and digital certificates.

The Inopli DRP module applies this principle in a fully automated and scalable manner. It collects and analyzes content from dozens of external sources and transforms it into actionable findings tied to monitored entities like brands, VIPs, and sensitive strings. Through techniques like language detection, entity recognition, similarity analysis, metadata extraction, OCR, and transcription, it enriches each signal with relevant context to support prioritization. Findings are classified by severity and type, enabling security teams to focus on what matters most, before damage occurs.

## What DRP Monitors

### [Communication channels](/drp/comm-channels-monitoring/messaging-and-chats)

* Public semi-open and private messengers and chat networks, including Discord, Telegram and IRC. Coverage includes text, links, and shared media (documents, images, audio). Findings are correlated to monitored companies, VIPs, and sensitive strings.

### [Deep/Dark web monitor](/drp/deep-dark-web-monitoring/deep-dark-web)

* Monitors relevant resources, crawling pages and scanning internal content (text and media). It applies the same enrichment used elsewhere—OCR for images, archive inspection, metadata analysis, and transcription—to surface findings tied to brands, VIPs, and sensitive strings.

### [Surface web & exposed assets](/drp/surface-web-monitoring/surface-web)

* Domain and certificate monitoring via Certificate Transparency (CT) logs to surface new certificates and domain look-alikesand inspects surface content for phishing and leaked or sensitive data, similarity, typosquatting, and bitsquatting analyses highlight impersonation risks.

### Core Detection Themes

* Mentions of monitored companies and VIPs across sources, with structured findings that include evidence and context.

### Sensitive strings and secrets

* Detection of emails, phone numbers, IPs, payment data patterns, and other sensitive strings; context is used to prioritize alerts.
* Purpose-built detection for credential leaks (e.g., user:password pairs), with noise reduction and correlation to monitored entities.

### Threat indicators

* Identification of phishing and malware indicators, suspicious commands, and attack patterns in messages, with severity-based prioritization.

### Links and infrastructure clues

* URL extraction and parsing (including t.me variations), plus domain/channel derivation to enrich context.

### Media intelligence

* **OCR on images** to extract text for correlation.
* **Archive inspection** (ZIP/RAR/7z/tar.gz) with recursive extraction and text analysis.
* **EXIF/metadata** analysis (e.g., GPS, capture time, device) to add geospatial/temporal context.
* **Audio transcription** with multilingual support; transcripts are analyzed like text.

### Language & entity understanding

* Automatic language detection across text, OCR, and transcripts.
* Multilingual Named Entity Recognition (people, organizations, locations, dates, monetary values, etc.) to enrich findings.


# Comm Channels Monitoring

The <mark style="color:green;">Communication Channels Monitoring</mark> component of the DRP module focuses on identifying early signs of digital risk by observing public and restricted conversation spaces such as messaging platforms, group chats, and online forums. Its purpose is to detect potential threats or reputational issues related to brands, executives, and sensitive terms through ongoing analysis of what people are saying and sharing in these channels. The monitoring is continuous and designed to <mark style="color:green;">avoid overloading sources, preserving the natural flow of the data being collected</mark>.

This module captures both text and shared media, including documents, images, and audio. All content is automatically examined to identify names of people or companies, mentions of confidential information, and any indications of malicious activity. Even when this information is <mark style="color:green;">hidden inside files, images, or audio clips</mark>, the system is capable of interpreting and analyzing them. This allows it to uncover leaks, suspicious conversations, or early signs of coordinated attacks that may not be immediately visible.

Each relevant finding is organized in a structured way, with context such as where it was found and how serious it might be. This helps teams quickly understand what matters most and take action when needed. The goal is not just to collect raw data, but to transform unstructured chatter into clear, actionable insights that support digital risk teams in staying ahead of emerging threats.

### **Where DRP looks.**

* <mark style="color:green;">**Messaging & chats**</mark>**:** DRP inspects messages and attachments (documents, images, archives, audio), extracts URLs and domains, and correlates mentions to monitored entities. It extends visibility with OCR for images, archive inspection, EXIF/metadata review, and audio transcription.
* <mark style="color:green;">**Forums & IRC-style communities**</mark>**:** DRP processes real-time messages and linked media to detect entity mentions (companies/VIPs/Sensitive Srings), sensitive strings, and other indicators. Multilingual entity recognition is applied to add context to each finding.

### Next pages

* [Messaging & Chats](/drp/comm-channels-monitoring/messaging-and-chats)
* [Forums & Communities](/drp/comm-channels-monitoring/forums-and-communities)
* [Risk Signals Detected](/drp/comm-channels-monitoring/risk-signals-detected)
* [Enrichment Strategies](/drp/comm-channels-monitoring/enrichment-strategies)


# Messaging & Chats

The *<mark style="color:green;">Messaging & Chats</mark>* module is part of the DRP solution focused on identifying digital threats that emerge in informal, high-velocity communication channels. These environments, such as <mark style="color:green;">**Telegram**</mark><mark style="color:green;">,</mark> <mark style="color:green;"></mark><mark style="color:green;">**IRC**</mark><mark style="color:green;">, and</mark> <mark style="color:green;"></mark><mark style="color:green;">**Discord**</mark>**,** are often used to discuss vulnerabilities, coordinate attacks, or circulate leaked data before such activity becomes visible on broader platforms. By maintaining active monitoring in these spaces, the module helps organizations anticipate and respond to security incidents in their earliest stages.

### What We Monitor

This module tracks conversations and shared content in public and private groups where threat actors, hacktivist communities, or information leakers may be active.&#x20;

* On <mark style="color:green;">Telegram</mark>, it follows discussions in large public channels and groups known for spreading sensitive information.&#x20;
* <mark style="color:green;">IRC</mark> remains relevant among certain technical circles where tactics, tools, and exploits are often exchanged.&#x20;
* <mark style="color:green;">Discord</mark>, with its diverse range of communities, also includes servers where information security topics are discussed, sometimes, including confidential or malicious content.

### Why This Matters

Real-time chat environments are where many threats first surface, often, hours or days before appearing in traditional intelligence feeds. For security teams, having visibility into these spaces is critical for early detection and proactive defense.&#x20;

This module enhances an organization’s ability to identify and respond to threats involving leaked data, impersonation attempts, exposed credentials, and reputational risks, all in alignment with a broader digital risk protection strategy.


# Forums & Communities

The *<mark style="color:green;">Forums & Communities</mark>* module monitors open discussions across the <mark style="color:green;">surface web</mark> as well as in <mark style="color:green;">deep and dark web</mark> environments. These spaces, often structured as discussion boards or hidden marketplaces, are widely used by cybercriminals to share techniques, leak stolen data, advertise access to compromised systems, or coordinate fraudulent activities. These forums are a critical source for identifying early-stage threats and emerging attack trends.

### Where We Look

On the <mark style="color:green;">surface web</mark>, the module tracks publicly accessible forums and community platforms where information related to cybersecurity, social engineering, or illicit data exchange may appear. This includes niche websites focused on specific technologies, underground sharing platforms, and open repositories of exposed information.

In parallel, the system monitors <mark style="color:green;">**hundreds of forums in deep and dark web environments**</mark>, where threat actors are more active and less inhibited. These include invite-only communities, marketplaces, and anonymous boards often associated with data leaks, malware distribution, and discussions about targeted attacks against companies or individuals. These forums operate in hidden networks and tend to be volatile, which makes structured monitoring essential for maintaining situational awareness.

### Why This Matters

Forums and online communities, particularly, those in the deep and dark web are where much of the cyber threat landscape is openly discussed. Actors share tactics, collaborate on exploits, and leak stolen data, often before such information reaches the public domain or intelligence reports. By actively monitoring these spaces, this DRP module helps organizations detect threats earlier, validate incidents, and understand how they are perceived or targeted within underground circles.

This visibility is key for anticipating attacks, mitigating reputational damage, and accelerating response. It enables security teams to take informed actions based on concrete findings, not speculation, strengthening the organization’s posture against digital risks that originate beyond the perimeter.


# Risk Signals Detected

<mark style="color:green;">Risk signals</mark> are the core output of the DRP monitoring process. These signals are the tangible results of observing informal, high-velocity digital spaces where early indicators of security threats frequently emerge. They represent findings that may require attention, investigation, or immediate action depending on their severity and context.

### Understanding Risk Signals

A <mark style="color:green;">risk signal</mark> can take many forms: leaked credentials being shared or sold, confidential documents exposed in chat groups, mentions of executive names or internal systems in dark web discussions, or even planned attacks circulating among threat actors. What defines a signal is not just *what* is said, but *where* and *how* it appears. A file shared in a closed forum known for cybercrime has a very different meaning than a message posted in a public channel.

The system identifies and interprets these signals by analyzing patterns of communication, the relevance of the content to monitored entities, and the nature of the platform where it was found. It distinguishes casual commentary from coordinated threats or sensitive data exposures ensuring that only the most actionable intelligence reaches the security team.

### From Raw Content to Actionable Insight

<mark style="color:green;">Risk signals</mark> are not simply extracted data points, they are enriched findings. Each one is contextualized to explain the type of threat involved (e.g., data leakage, impersonation, credential exposure), its possible impact, and the environment in which it was detected. This gives incident response teams a clear, prioritized view of what matters most, allowing them to act quickly when necessary by consolidating signals from disparate sources and translating them into structured, <mark style="color:green;">security-relevant insights</mark>.


# Enrichment Strategies

The <mark style="color:green;">enrichment stage</mark> transforms raw material gathered from messaging platforms, forums, and other communication channels into intelligence that security teams can act on. Instead of passing along unstructured text or files exactly as they appear, the DRP platform adds layers of meaning that clarify who is involved, what is being discussed, and why it could matter to the organisation’s security posture.

### Why Enrichment Matters

Messages and posts rarely arrive in a neat format. They may be written in different languages, include shorthand or emojis, reference people or systems only insiders recognise, or hide sensitive information inside attachments. Without additional context, an analyst must spend time deciphering each fragment before deciding whether it poses a real threat. Enrichment automates that effort: it cleans and normalises content, detects its language, and attaches relevant metadata so that analysts can focus on judgement rather than translation or formatting tasks.

### Layers of Context Applied

First, <mark style="color:green;">linguistic processing</mark> determines the language of every message and converts unusual encodings into a standard form, ensuring nothing is lost to garbled characters. Next, the system identifies <mark style="color:green;">names of people, companies, products, locations, and monetary values</mark> to reveal who or what is being discussed. References are then matched against the organisation’s monitored assets, brands, executives, domains, or technologies so that even indirect mentions surface as potential concerns.

Attachments receive similar attention. Documents are read for embedded text, images are scanned for on-screen words, and archives are unpacked so that hidden material cannot slip past unnoticed. Throughout this process, duplicate items are removed and timestamps are aligned, allowing conversations to be viewed in sequence rather than as isolated snapshots. Finally, each finding is assigned an initial relevance score that reflects its probable impact, helping security teams decide what to investigate first.

### Outcome for Analysts

When enrichment is complete, every finding includes enough context for immediate triage: the original evidence, a concise explanation of its significance, and indicators such as language, entities mentioned, and preliminary severity.&#x20;


# Deep/Dark Web Monitoring

<mark style="color:green;">Deep and dark web spaces</mark> host some of the most valuable early-warning signals for information-security teams. <mark style="color:green;">Hidden marketplaces, invitation-only forums, leak sites, ransomware blogs and covert communication channels</mark> are often where stolen data is advertised, access to compromised networks is sold, and plans for future attacks are discussed. The Deep / Dark Web Monitoring component of the DRP solution maintains ongoing visibility across these environments so that organisations can detect emerging threats long before they surface in conventional intelligence feeds or mainstream media.

### Where We Look

Coverage includes a wide range of hidden services reachable via Tor or similar anonymity networks, as well as closed communities that operate behind registration barriers or trust-based vetting. This span of sources captures posts offering <mark style="color:green;">credentials, corporate documents, customer records, exploit kits, or discussions about targeting specific brands, executives or technologies</mark>. Because many of these sites appear and disappear unpredictably, continuous observation is essential to avoid blind spots.

### How Findings Are Generated

Content gathered from these channels is examined for indicators that matter to the organisation: leaked data sets, mentions of proprietary systems, references to privileged accounts, or negotiations to buy and sell illicit access. Context such as the reputation of the poster, the forum’s focus, and the type of asset being traded is factored into each finding. <mark style="color:green;">Only material that could present a plausible risk is elevated</mark>, helping security teams focus on genuine exposures rather than background chatter.

### Next pages

* [Deep/Dark Web](/drp/deep-dark-web-monitoring/deep-dark-web)
* [Risk Signals Detected](/drp/deep-dark-web-monitoring/risk-signals-detected)
* [Enrichment Strategies](/drp/deep-dark-web-monitoring/enrichment-strategies)


# Deep/Dark Web

The <mark style="color:green;">Deep / Dark Web section</mark> of the DRP concentrates on hidden parts of the internet. Sites and forums that are deliberately excluded from mainstream search engines and often require special networks such as Tor for access. These spaces host a steady trade in <mark style="color:green;">stolen data, privileged-access</mark> offers and discussions about forthcoming attacks.&#x20;

#### What We Monitor

* <mark style="color:green;">**Leak and dump sites**</mark>: repositories where attackers publish or sell credential collections, internal documents, or customer records.
* <mark style="color:green;">**Underground marketplaces**</mark>: listings that advertise remote-access tools, exploits, or corporate assets for sale.
* <mark style="color:green;">**Ransomware and extortion blogs**</mark>: pages where criminal groups announce victims, publish sample data, and negotiate payments.
* <mark style="color:green;">**Closed technical forums**</mark>: invitation-only boards where threat actors exchange tactics or crowd-source vulnerabilities.

#### Why This Matters

Activity in deep and dark-web communities frequently precedes <mark style="color:green;">high-profile breaches or reputational crises</mark>. Early awareness allows security teams to validate whether their data is exposed, understand adversary intentions and launch containment measures <mark style="color:green;">before damage escalates</mark>. Continuous monitoring of these hidden environments therefore forms a critical layer of defence within a comprehensive <mark style="color:green;">Digital Risk Protection strategy</mark>.


# Risk Signals Detected

The *<mark style="color:green;">Risk Signals Detected</mark>* section explains the types of findings generated through deep and dark web monitoring. These findings emerge from <mark style="color:green;">underground forums, ransomware blogs, leak sites, and hidden marketplaces</mark>, where threat actors share, sell, or discuss content that may indicate exposure or targeting of an organization. Each signal is collected, interpreted, and structured to support early detection and response.

#### What We Detect

This monitoring layer identifies different types of digital risk that may impact a business, including:

* <mark style="color:green;">**Credential leaks**</mark>**:** mentions or listings of usernames, passwords, or authentication tokens tied to corporate systems, domains, or key individuals.
* <mark style="color:green;">**Data exposure**</mark>**:** internal documents, customer records, or confidential files posted publicly or offered for sale.
* <mark style="color:green;">**Access-for-sale offers**</mark>**:** discussions or listings advertising unauthorized access to systems such as VPNs, RDPs, panels, or inboxes.
* <mark style="color:green;">**Extortion activity**</mark>**:** ransomware victim announcements, sample leaks, negotiation details, or countdown pages linked to payment demands.
* <mark style="color:green;">**Targeting and impersonation**</mark>**:** posts referencing executives, employees, partners, or customers in the context of fraud, social engineering, or doxxing.
* <mark style="color:green;">**Attack planning**</mark>**:** threat actor conversations related to tools, exploits, or infrastructure used by the organization or its supply chain.

#### Why This Matters

These findings offer early visibility into events that can lead to serious incidents often appearing days or weeks before any public disclosure. By identifying signals of compromise or malicious intent at the source, security teams can act proactively: containing the threat, notifying impacted stakeholders, or initiating response efforts.

Each signal is presented with clear context: what was found, where it was found, and why it may pose a risk. This helps transform hidden, fragmented activity into actionable intelligence, supporting a stronger and faster digital risk response.


# Enrichment Strategies

The *<mark style="color:green;">Enrichment Strategies</mark>* applied to deep and dark web findings ensure that raw, often fragmented content is transformed into clear and actionable intelligence due to the nature of these sources like <mark style="color:green;">forums, leak sites, and underground markets</mark>. Many posts include informal language, encrypted references, or hidden data within files. Enrichment adds the necessary context to help security teams understand the significance of each finding.

#### What We Do

This process begins by standardizing and cleaning the content. The language of each item is identified, and relevant entities such as people, companies, domains, or technologies are extracted and linked to the organization’s monitored assets. Files and archives are unpacked, images are scanned for on-screen text, and audio is transcribed when necessary. This allows buried evidence to be revealed and included in the analysis.

In addition to the content itself, metadata such as timestamps, links, and file information is collected to complete the picture. If the same leak appears in different places, duplicates are removed and the information is consolidated to present a single, unified view to analysts. Findings are also prioritized based on relevance and severity.

#### Why This Matters

Without enrichment, deep and dark web content remains difficult to interpret and full of noise. With it, each signal becomes easier to understand, compare, and act on. The process allows analysts to quickly identify exposed credentials, leaked documents, access-for-sale offers, or active threats, all with enough context to support immediate decision-making.


# Surface Web Monitoring

The *<mark style="color:green;">Surface Web Monitoring</mark>* section of the DRP program focuses on open, searchable parts of the internet where security-relevant traces frequently appear first. It looks for brand misuse, exposed data, and infrastructure signals that indicate phishing, impersonation, or operational exposure well before these issues turn into incidents.

#### What We Monitor

* <mark style="color:green;">**Open web & targeted searches**</mark>**:** public pages and indexed content using OSINT queries to surface mentions of companies, VIPs, and sensitive strings, as well as exposed API specs or cloud resources.&#x20;
* <mark style="color:green;">**Public code repositories**</mark>**:** GitHub, GitLab, and Bitbucket for credentials, configuration files, and proprietary material committed by mistake.
* <mark style="color:green;">**Domain ecosystem & certificates**</mark>**:** newly issued TLS certificates and domain permutations that resemble official brands, helping reveal phishing sites and look-alike infrastructure.
* <mark style="color:green;">**Look-alike domains (abuse)**</mark>**:** detection of typosquatting and related variants that exploit visual or keyboard similarities to mislead users.
* <mark style="color:green;">**App stores and extensions**</mark>**:** listings that impersonate brands, misuse trademarks, or bundle malicious functionality.
* <mark style="color:green;">**DNS and subdomains**</mark>**:** public records and subdomain enumeration that reveal misconfigurations or unintended exposure of services.

#### Why This Matters

Surface-web signals often foreshadow phishing campaigns, fraud, and data exposure. Early visibility into look-alike domains, leaked code or credentials, risky app listings, and misconfigured services enables faster takedown, containment, and stakeholder notification.

### Next pages

* [Surface Web](/drp/surface-web-monitoring/surface-web)
* [Domain & Brand Look-Alikes](/drp/surface-web-monitoring/domain-and-brand-look-alikes)
* [Risk Signals Detected](/drp/surface-web-monitoring/risk-signals-detected)
* [Enrichment Strategies](/drp/surface-web-monitoring/enrichment-strategies)


# Surface Web

The *<mark style="color:green;">Surface Web</mark>* monitors open, searchable parts of the internet to uncover brand misuse, exposed assets, and security-relevant traces that often precede incidents. Coverage spans public sites, code repositories, domain/certificate ecosystems, DNS and subdomains, cloud storage, and official/third-party app stores. The goal is to turn open-web noise into concrete findings tied to your brands, people, and infrastructure.

### What We Monitor

* <mark style="color:green;">**Public web & targeted searches**</mark>**:** Open pages and indexed content are queried for sensitive strings, exposed API documentation (Swagger/OpenAPI, Postman collections), and other security artefacts. Crawling of corporate sites helps reveal credentials, configs, and unintended data exposure. &#x20;
* <mark style="color:green;">**Public code repositories**</mark>**:** GitHub, GitLab, and Bitbucket are scanned for secrets, configuration files, and proprietary material, including, checks across recent commit history.&#x20;
* <mark style="color:green;">**Domains, certificates & look-alikes**</mark>**:** Subdomains and newly issued certificates are tracked to surface fresh assets and attack infrastructure. Look-alike risks are identified using domain-variation techniques and similarity analysis. &#x20;
* <mark style="color:green;">**DNS & infrastructure signals**</mark>**:** DNS records are validated to catch misconfigurations; exposed hosts/services are mapped and fingerprinted to identify technologies and versions in use.&#x20;
* <mark style="color:green;">**Cloud storage exposure**</mark>**:** Publicly accessible buckets and containers across S3, GCP, and Azure are discovered through optimized permutation strategies and assessed for sensitive content. &#x20;

### How We Detect

Findings are produced by combining OSINT scanning with validation steps that reduce false positives. Web searches feed into structured analysis pipelines; subdomains are enumerated. Domain look-alikes are generated and ranked by similarity models. DNS checks and service fingerprinting validate real exposure. cloud buckets are enumerated and verified for public access and sensitive files; app-store look-alikes are confirmed with textual and visual similarity methods.     &#x20;

#### Why This Matters

Open-web traces frequently foreshadow phishing, fraud, data leakage, or abuse of brand and infrastructure. Early visibility into misconfigured services, leaked secrets, look-alike domains, risky app listings, and exposed cloud storage enables rapid takedown and containment, strengthening the organization’s overall digital risk protection posture.


# Domain & Brand Look-alikes

The *<mark style="color:green;">Domain & Brand Look-alikes</mark>* covers surface websites and domains that imitate official brands to enable phishing, fraud, or traffic hijacking. It focuses on domain variations, deceptive registrations, and cloned pages that resemble legitimate assets closely enough to confuse users.

#### What We Monitor

* <mark style="color:green;">**Domain permutations and IDNs**</mark>**:** variations created via typosquatting, homograph/Unicode swaps, bitsquatting, TLD swaps, and subdomain tricks that resemble official domains. &#x20;
* <mark style="color:green;">**New certificates & subdomains**</mark>**:** certificate issuance that mentions brand domains (via Certificate Transparency) and subdomain discoveries. &#x20;
* <mark style="color:green;">**Live site clones**</mark>**:** pages that copy branding, layouts, or flows from the official site to collect credentials or payments. Similarity is checked against the legitimate site.&#x20;
* <mark style="color:green;">**Registration & DNS signals**</mark>**:** WHOIS data, name servers, and DNS records that indicate newly activated or misconfigured look-alike infrastructure.&#x20;

#### How We Detect

Candidates are generated with multiple domain-fuzzing strategies. They’re then compared to monitored brands using weighted similarity measures to highlight the closest matches.  \
To catch active infrastructure early, the system watches CT logs for certificates that include monitored names and extracts SAN entries to reveal new hostnames; subdomains are also enumerated via search engines and CT sources.  \
Each candidate is validated with DNS/WHOIS checks and content analysis. Pages are fingerprinted (screenshots, perceptual hashes and fuzzy hashing) and compared to the official site to spot clones even when HTML differs. &#x20;

#### Why This Matters

Look-alike domains are a common foundation for phishing, credential theft, brand abuse, and malware delivery. Detecting them at the moment of appearance when a certificate is issued, DNS goes live, or a clone is first published gives security teams time to block, takedown, or warn users before large-scale impact. Continuous coverage of permutations, certificates, subdomains, and page similarity reduces blind spots and strengthens brand and user protection within the DRP program.


# Risk Signals Detected

The *<mark style="color:green;">Surface Web Monitoring</mark>* layer produces findings tied to exposed data, brand misuse, and signs of operational risk found in publicly accessible sources. These signals help identify early traces of compromise, misconfiguration, or abuse that may escalate if left unaddressed.

Findings in this layer typically fall into one of the following categories:

* <mark style="color:green;">**Leaked credentials and sensitive files**</mark>**:** authentication keys, passwords, API tokens, internal documentation, and configuration files exposed through public code repositories like GitHub or embedded in company websites.
* <mark style="color:green;">**Exposed APIs and data schemas**</mark>**:** public access to Swagger/OpenAPI specs or Postman collections that reveal the structure of internal systems, sensitive endpoints, or production data samples.
* <mark style="color:green;">**Open cloud storage**</mark>**:** public S3, GCP, or Azure buckets containing log files, backups, or confidential documents inadvertently exposed.
* <mark style="color:green;">**Brand impersonation and misleading domains**</mark>**:** look-alike domains registered to exploit visual or keyboard similarity with official assets, often used in phishing or fraud campaigns.
* <mark style="color:green;">**Certificate and DNS anomalies**</mark>**:** new TLS certificates or subdomains linked to monitored brands, which may indicate shadow infrastructure or asset misuse.

Each finding is linked to a specific risk category such as phishing, data leakage, infrastructure exposure, or brand fraud and is enriched with supporting evidence and context to support investigation and response.


# Enrichment Strategies

Each piece of <mark style="color:green;">collected evidence</mark> undergoes normalization and classification. Language is detected and content is cleaned to eliminate false positives from formatting issues or irrelevant matches. When credentials, keys, or tokens are identified in code or web pages, the enrichment process cross-checks them against known brand domains, employee emails, or infrastructure patterns to confirm the likelihood of real exposure.

In cases involving <mark style="color:green;">domains or subdomains</mark>, WHOIS metadata, certificate transparency records, and DNS responses are added to determine whether the asset is newly registered, active, and potentially malicious. **Additionally,&#x20;**<mark style="color:green;">**all suspicious domains are validated against the Inopli internal threat feed**</mark>**&#x20;and public phishing repositories to confirm known malicious infrastructure and reduce false positives.** This step enhances the ability to quickly identify phishing threats and supports prioritization based on confirmed reputation signals.

When findings involve <mark style="color:green;">**cloud storage**</mark>, enrichment confirms whether the exposed content is publicly accessible, identifies the cloud provider, and examines the filenames and content types to highlight sensitive data such as internal documentation, logs, or customer information.

For <mark style="color:green;">**public code repositories**</mark>, commit metadata and author information are included to support traceability. Findings are enriched with indicators such as repository visibility, timestamps, and file paths to help prioritize which exposures require immediate attention.


# VIP Monitoring

<mark style="color:green;">VIP Monitoring</mark> focuses on protecting executives and other high-profile individuals by identifying early signs of digital risk tied to their names, roles, and personal context. Coverage spans the monitored surfaces of the DRP program messaging platforms, forums and communities, and the open web so mentions and exposures are detected even when they appear in fast-moving or niche venues. Multilingual analysis and entity recognition ensure that person names and related details are captured consistently across languages and formats. &#x20;

#### Where We Look

Monitoring includes real-time chat ecosystems and community boards where VIP references often emerge first. Mentions in Telegram, Discord and IRC are correlated to tracked VIP profiles, with direct and indirect references detected even when names are abbreviated or altered.  Findings from these streams are packaged with context for downstream triage alongside other DRP outputs, keeping VIP-related activity aligned with wider risk monitoring.&#x20;

#### What We Monitor

VIP-related findings typically involve four exposure patterns. <mark style="color:green;">**Identity and impersonation**</mark> signals include name misuse, look-alike profiles, and social-engineering set-ups that reference a VIP to build trust or pressure targets. <mark style="color:green;">**Data and credential exposure**</mark> covers leaks of email/password pairs and documents that include VIP identifiers, with correlation to monitored entities to raise priority.   <mark style="color:green;">**Personal context in media**</mark> extends detection beyond plain text: text inside images (OCR), content within archives, and speech transcribed from shared audio are all scanned for VIP mentions.  <mark style="color:green;">**Location or sensitive metadata**</mark> in shared images can add time/place clues around a VIP reference, improving assessment of potential physical-world risk.&#x20;

#### How Findings Are Produced

Mentions of VIPs are detected in text, images, documents, and audio, enriched with multilingual NER, and correlated to the monitored VIP catalogue to distinguish casual references from security-relevant ones.   Each validated observation is emitted as a structured finding with the evidence, source context, and an initial severity to support rapid triage and response by security teams.&#x20;

#### Why This Matters

Threat actors frequently exploit VIP identities for phishing, extortion, fraud, or doxxing. Early, cross-surface visibility into VIP mentions backed by multi-format analysis helps reduce time to detect, confirm, and contain incidents that could escalate into reputational, legal, or physical-security harm.


# Keyword / Query Monitoring

<mark style="color:green;">Keyword / Query Monitoring</mark> strengthens DRP coverage by tracking brand names, VIPs, and **sensitive strings** across monitored sources and languages. It focuses on meaningful mentions and security-relevant patterns—credentials, URLs, and other indicators, turning scattered references into structured findings with context and initial severity.&#x20;

#### What We Monitor

The watchlists include organization names, executive identities, product terms, domains, and **sensitive strings** tied to confidentiality or access. Detection considers both direct and indirect mentions and correlates them to monitored entities to surface true relevance.  \
Signals are captured in **multiple languages**, ensuring that references in different regions or communities are not missed.&#x20;

#### How Queries Are Applied

Queries operate across text and shared media so that <mark style="color:green;">**evidence inside files**</mark> is discoverable. Text found in images (OCR), documents, and archives is extracted and evaluated against the same watchlists used for messages.  Security-oriented patterns such as <mark style="color:green;">**malicious URLs**</mark>, commands, and phishing artefacts are included to detect early threat coordination alongside brand or VIP references. &#x20;

#### Why This Matters

Mentions of brands, executives, and **sensitive strings** often precede data leakage, credential exposure, or social-engineering campaigns. By unifying multilingual queries with entity correlation and media-aware discovery, the monitoring reduces noise and delivers <mark style="color:green;">**actionable findings**</mark> what was found, where, and why it matters for security.


# Social Media Monitoring

The *<mark style="color:green;">Social Media Monitoring</mark>* section focuses on public and semi-open networks where impersonation, fraud, and data exposure frequently appear first. Coverage spans multiple platforms and languages, correlating mentions of brands, companies, and VIPs to produce security-relevant findings rather than raw posts. &#x20;

#### What We Monitor

Social profiles and content are evaluated for signals that matter to information security:

* <mark style="color:green;">**Profiles and account behavior**</mark>**:** creation date, followers, posting activity, inactivity, and patterns that indicate newly created or suspicious accounts are assessed to spot likely impersonation or abuse.&#x20;
* <mark style="color:green;">**Text and bio indicators**</mark>**:** usernames, names, bios, and posts are checked for risky elements such as suspicious links, emails, and phone numbers that can support phishing or scams.&#x20;
* <mark style="color:green;">**Mentions of monitored entities**</mark>**:** references to companies and VIPs are correlated across languages to prevent missing region-specific or obfuscated mentions. &#x20;
* <mark style="color:green;">**Media and links in posts**</mark>**:** embedded URLs are extracted and associated with the finding; text inside images and documents is read so that signals hidden in media are not overlooked. &#x20;
* <mark style="color:green;">**Tasked searches**</mark>**:** targeted lookups by username, personal name, company, or VIP are supported to surface impersonation attempts and brand misuse efficiently.&#x20;

Each validated observation is published as a structured finding with type, severity, and contextual metadata to support rapid triage alongside other DRP outputs.&#x20;

#### Why This Matters

Abuse of brand identity and VIP personas on social networks enables phishing, fraud, doxxing, and misinformation. Early, cross-language visibility into suspicious profiles, risky content, and media-embedded signals shortens time to detect and contain incidents, improving digital risk protection without overwhelming teams with noise.


# Page Reference Monitoring

The <mark style="color:green;">**Page Reference Monitoring**</mark> feature enables proactive detection of phishing and brand impersonation attempts through embedded JavaScript code. This mechanism identifies when legitimate websites are cloned and deployed under unauthorized or suspicious domains, allowing the security team to react before reputational or financial damage occurs.

This feature is particularly effective for detecting <mark style="color:green;">**look-alike sites**</mark>, credential harvesting pages, or infrastructure reuse targeting users of a known web service or brand.

***

#### How It Works

1. <mark style="color:green;">**Script Deployment**</mark>\
   The Inopli platform provides a unique JavaScript snippet for each monitored domain. This script is embedded directly into the HTML of selected web pages (typically login portals, user dashboards, or transaction pages).
2. <mark style="color:green;">**Silent Beaconing**</mark>\
   When the legitimate page is loaded, the script performs passive fingerprinting and silently confirms the origin via a secured beacon back to the Inopli DRP backend.
3. <mark style="color:green;">**Clone Detection**</mark>\
   If the same HTML and JavaScript are reused or mirrored under a different domain—typically during phishing or impersonation attempts—the beacon is still triggered but now exposes a mismatch in origin. This event is logged and surfaced as a <mark style="color:green;">**Finding**</mark> in the DRP console.
4. <mark style="color:green;">**Threat Attribution**</mark>\
   The suspicious or unauthorized domain is then enriched and flagged using all standard enrichment processes: WHOIS, DNS, phishing feeds, and the Inopli internal threat graph. If confirmed as malicious, it is escalated via the Response module.

***

#### Benefits

* Early detection of phishing sites before wide distribution
* Passive monitoring, no active scanning required
* Lightweight, no impact on page performance
* Automatic correlation with brand and infrastructure profiles
* Seamless integration with existing DRP findings and workflows


# App Stores

The *<mark style="color:green;">App Stores</mark>* section of the DRP monitors official and third-party catalogues to uncover brand impersonation, malicious or misleading listings, and unauthorized distribution of software tied to the organization. Coverage includes major stores as well as alternative Android repositories  with capture of listing details, icons, screenshots and basic metadata for assessment.  &#x20;

#### What We Monitor

* <mark style="color:green;">**Impersonation in names and publishers**</mark>**:** app titles and developer identities that closely resemble official brands or company units, suggesting attempts to mislead users.&#x20;
* <mark style="color:green;">**Visual misuse of brand assets**</mark>**:** icons and screenshots that reuse or mimic official logos, layouts, or design elements to increase credibility.&#x20;
* <mark style="color:green;">**Cloned or repackaged apps**</mark>**:** listings whose package contents or structure strongly overlap with legitimate apps, indicating republishing or tampering.&#x20;
* <mark style="color:green;">**Unauthorized distributions**</mark>**:** appearances of corporate APKs or SDKs outside approved channels, including mirrors in third-party stores. &#x20;
* <mark style="color:green;">**Suspicious listing context**</mark>**:** anomalies in listing metadata (e.g., name/developer mismatches, inconsistent descriptions, recycled imagery) used to prioritize review.&#x20;

#### Why This Matters

Abusive or counterfeit apps enable <mark style="color:green;">credential theft, malware delivery and brand fraud</mark> at scale. Early detection of impersonation, repackaging and unauthorized distribution provides time to request takedowns, warn users and remediate exposure, strengthening overall digital risk protection across mobile ecosystems.&#x20;


# Client Onboarding and Configuration


# Company Setup

The activation of <mark style="color:green;">Inopli's Digital Risk Protection (DRP) module</mark> for a monitored entity begins with the configuration of its monitoring profile. This is a required first step before any data collection or threat detection can begin. The monitoring profile provides the baseline identity data and digital presence of the company, allowing the DRP system to contextualize and correlate findings accurately.

The process must be initiated by the authorized partner or designated contact for the monitored company. A formal monitoring activation request must be submitted, including a complete set of required profile information. Once validated, this data is used to guide and personalize all DRP monitoring tasks across surface web, social media, deep/dark web, and app ecosystems.

#### Required Information

The following fields must be provided when requesting DRP activation:

* `brand name` — Display name of the monitored brand
* `legal name` — Official registered name of the entity
* `tax id` — Legal tax identifier of the organization
* `country` — Country of registration or operations
* `language` — Primary language used in brand presence and communication

**Social & Digital Presence**

These informations are essential for monitoring across communication channels and public platforms:

* `facebook`, `instagram`, `twitter`, `linkedin`, `youtube`, `tiktok`, `threads`, `telegram`, `whatsapp`, `wechat`, `qq`, `reddit`, `snapchat`, `pinterest`, `tumblr`, `medium`, `vk`, `flickr`, `vimeo`, `stackoverflow`, `discord`
* `github`, `gitlab`, `google_play_id`&#x20;

#### Process Notes

* Once activated, the system begins entity correlation and enrichment tasks for threat detection.
* Any changes to this profile after activation must be submitted via the update workflow.


# Monitoring Profiles

The <mark style="color:green;">DRP module</mark> defines the customized perimeter of each monitored entity within it. These profiles serve as the operational scope for threat detection, data enrichment, and prioritization. They allow organizations to configure what should be monitored, such as <mark style="color:green;">domains, high-risk individuals (VIPs), and sensitive keywords or identifiers (strings)</mark> tailoring detection efforts to their unique risk surface.

Each profile is fully self-managed by the user through the configuration interface under the respective company settings. Authorized users can add, edit, or remove items at any time. The DRP engine continuously ingests and correlates these elements across surface, deep/dark web, and communication platforms to identify brand impersonation, credential leaks, reputational threats, and fraud campaigns.

#### Profile Types

There are three types of items that can be configured within a Monitoring Profile:

* <mark style="color:green;">**Domains:**</mark> Used for tracking company-owned domains, subdomains, and web infrastructure.
* <mark style="color:green;">**VIPs:**</mark> Includes executives, public figures, or employees with a high exposure or risk index.
* <mark style="color:green;">**Strings:**</mark> Covers sensitive keywords, identifiers, or custom tokens such as product names, legal terms, internal project codes, or PII patterns.

Each of these categories can be managed independently and updated as the threat surface evolves.

***

**Pages in this section:**

* [Domains](/drp/client-onboarding-and-configuration/monitoring-profiles/domains)
* [VIPs](/drp/client-onboarding-and-configuration/monitoring-profiles/vips)
* [Strings](/drp/client-onboarding-and-configuration/monitoring-profiles/sensitive-strings)


# Domains

<mark style="color:green;">Domains</mark> are foundational elements in digital risk monitoring. By registering organizational domains, the <mark style="color:green;">Inopli DRP module</mark> is able to detect impersonation attempts, typo-squatting, subdomain enumeration, phishing campaigns, certificate transparency anomalies, and data leaks linked to the organization’s web infrastructure.

The configuration process is straightforward and requires only the input of a domain name. Once registered and marked as active, the DRP engine continuously monitors external sources such as <mark style="color:green;">surface web, WHOIS records, SSL certificates, paste sites, and malicious DNS entries</mark> for threats tied to the domain.

Findings are enriched with context, risk level, and exposure metadata. If validated as true positives, they trigger response actions in the Inopli Response module for incident tracking and remediation.

***

#### Domain Configuration Fields

Each domain entry contains only one required field:

* `domain` – The fully qualified domain name (e.g., `example.com`) to be monitored

***

#### User Interface Example

Below is the platform interface used to manage and monitor domains:

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FlJV8077Fa3gM7J6kPQZr%2Fimage.png?alt=media&amp;token=c889fc72-0ccd-4535-b937-83ab2f6e497e" alt=""><figcaption></figcaption></figure>

Each Domain can be toggled on/off, and actions include edit or remove. Only active Domains are monitored in real time.


# Sensitive Strings

<mark style="color:green;">Sensitive Strings</mark> are <mark style="color:green;">user-defined keywords, patterns, or identifiers</mark> that represent critical data elements for the organization. These may include API keys, internal project codes, client tokens, legal references, employee identifiers, or any proprietary string whose exposure could lead to risk scenarios such as data leakage, impersonation, or regulatory violations.

The <mark style="color:green;">Inopli DRP module</mark> allows companies to configure these strings directly from the platform’s settings panel under the `Sensitive Strings` tab. Once registered and activated, each string becomes a monitored entity. The DRP engine will continuously inspect indexed content (surface, dark web, and other channels) for signs of exposure, correlation, or misuse involving these terms.

Findings are enriched with metadata, including context of exposure, severity, and source, and may trigger incident creation through the Response module if confirmed as valid by the analyst or an automated policy.

***

#### String Configuration Fields

Each entry includes the following fields:

* `type` – Category of the string to be monitored. Accepted types are: `API Key`, `Password`, `Token`, `Secret`, `Other`
* `value` – The actual keyword or string to be monitored
* `regex_pattern` – Optional field to define a custom regular expression pattern
* `case_sensitive` – Boolean that defines if the match is case-sensitive
* `exact_match` – Boolean to specify if only exact string matches are accepted
* `category` – Optional logical grouping (e.g., Legal, DevOps, HR)
* `severity` – Risk impact associated with string exposure (e.g., Low, Medium, High)

***

#### User Interface Example

Below is the platform screen used to manage and edit sensitive strings for monitoring

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FuULCIo6IFEBvkKYqM3MU%2Fimage.png?alt=media&amp;token=6fcf84d3-4c8d-43b1-a355-3f3652208cc9" alt=""><figcaption></figcaption></figure>

Each Sensitive String can be toggled on/off, and actions include edit or remove. Only active Sensitive Strings are monitored in real time.


# VIPs

<mark style="color:green;">VIPs</mark> are individuals within the organization who hold strategic, public, or high-risk roles and therefore require targeted monitoring across external digital environments. These profiles are typically associated with executives, spokespersons, board members, or key personnel whose names, identities, or credentials could be exploited in impersonation, fraud, or reputational attacks.

In the <mark style="color:green;">Inopli DRP module</mark>, VIPs can be configured directly by the user in the <mark style="color:green;">**company’s DRP settings**</mark> <mark style="color:green;">**panel**</mark> under the `VIPs` tab of the Monitoring Profile section. Each registered VIP becomes a reference point for correlation across deep/dark web, social networks, forums, and other external data sources.

Once a VIP is configured and marked as active, the DRP system continuously searches for signals that may involve or target the person, including mentions, leaks, fake profiles, and social engineering indicators. Confirmed threats tied to a VIP will trigger the escalation workflow through the **Response module**, creating incidents for operational response if marked as true positive.

***

#### VIP Record Fields

Each VIP entry consists of the following fields:

* `full_name` – The individual’s full name as it appears in official or public records
* `department` – The department or unit the VIP belongs to
* `position` – The role or job title (e.g., CEO, CISO, Board Member)
* `risk_level` – Optional classification of risk exposure (e.g., High, Medium, Low)
* `notes` – Optional comments or context for identification
* Social media handles (optional):\
  `linkedin`, `twitter`, `facebook`, `instagram`, `tiktok`, `youtube`, `github`, `gitlab`, `snapchat`, `threads`, `tumblr`, `medium`, `stackoverflow`, `pinterest`, `reddit`, `telegram`, `wechat`, `qq`, `vk`, `vimeo`, `flickr`
* National identifiers (optional, if relevant):\
  `cpf`, `rg`, `cnh`, `passport`, `ssn`, `driver_license`, `national_id`, `residence_permit`, `eu_passport`, `nif`, `nie`, `dni`, `identity_card` – These are used only if legally allowed and justified by the risk profile

***

#### User Interface Example

Below is a screenshot of the VIP configuration screen used to add, edit, or deactivate VIPs from the monitoring scope:

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FT9Nom52nh4pqbzf530em%2Fimage.png?alt=media&amp;token=d76c5ccf-983c-4107-8d91-55a2584e26c9" alt=""><figcaption></figcaption></figure>

Each VIP can be toggled on/off, and actions include edit or remove. Only active VIPs are monitored in real time.


# Integrations


# Response Module

The <mark style="color:green;">Inopli DRP module</mark> is tightly integrated with the <mark style="color:green;">Inopli Response module</mark> to ensure that identified threats are not only detected but also managed through structured operational workflows. Once a monitoring profile is active and findings begin to surface, each signal is enriched and classified. Findings presented to the security team or analysts can be marked as true positives, false positives, or benign.

When a <mark style="color:green;">**true positive**</mark> is confirmed by an analyst or an automated rule, the system automatically triggers an escalation process by interfacing with the <mark style="color:green;">**Response module**</mark>. This process results in the <mark style="color:green;">**automatic creation of a security incident**</mark>, which is then assigned to the operations team for handling and resolution.

Each incident contains:

* The original finding and all correlated evidence
* Enrichment metadata from the DRP engine (e.g., entity match, severity, exposure level)
* Audit logs of analyst action (who validated and when)
* Links to response playbooks and historical context if applicable

This seamless integration ensures that threat signals are actionable and traceable, closing the loop between <mark style="color:green;">**detection and response**</mark>. It also helps maintain response consistency and reduces the likelihood of missing relevant threats due to manual friction or communication delays.


# Notifications


# SMS

The <mark style="color:green;">SMS integration</mark> allows the Inopli platform to send real-time alerts and notifications via SMS using <mark style="color:green;">AWS Simple Notification Service (SNS)</mark>. This is useful for reaching key stakeholders in high-priority situations, such as critical incident detection, VIP exposure, or urgent compliance findings.

This feature is optional and can be enabled by the user within the **Settings > Integrations** section of the platform.

***

### How It Works

Once activated, the Inopli platform uses the provided AWS credentials to publish messages to AWS SNS. SMS alerts are sent to the list of configured recipients based on predefined triggers such as validated findings, severity thresholds, or incident escalations. All delivery attempts are recorded in the platform’s audit logs.

***

### Required Configuration

To enable this integration, users must provide the following:

* `AWS Access Key ID` – IAM user access key with SNS publish permissions
* `AWS Secret Access Key` – Secret key for the IAM user
* `Region` – AWS region where SNS is active (e.g., `us-east-1`)
* `Recipients` – One or more phone numbers in E.164 format (e.g., `+14155552671`) that will receive SMS alerts
* `Topic ARN (optional)` – If integrating with a pre-existing SNS topic
* `Notification Triggers` – Event types that should trigger SMS alerts (e.g., confirmed VIP exposure, credential leak, etc.)

> 📌 **Security Note**: Credentials are stored securely with encryption. Only users with the appropriate permissions can modify or delete them.

***

#### Example Use Cases

* A VIP exposure is confirmed → SMS sent to the crisis response lead
* High-severity keyword leakage triggers an alert → SMS sent to compliance manager
* SOC team receives SMS when a domain impersonation finding is escalated


# E-mail

The <mark style="color:green;">Email integration</mark> enables the Inopli platform to send automated alerts and notifications via email using its built-in delivery service. No SMTP setup is required. This integration is ideal for keeping internal teams, stakeholders, or external partners informed of key security events such as confirmed findings, incident escalations, and monitoring anomalies.

This feature can be configured directly in the **Settings > Integrations** section of the platform.

***

### How It Works

The platform sends emails using its internal notification engine. Users only need to define the recipients and select the event types that should trigger email alerts. Each message includes structured metadata, contextual insights, and direct links to the relevant event or incident inside the platform. All emails are logged for audit purposes and delivery visibility.

***

### Required Configuration

To enable email notifications, users must define:

* `Recipients` – One or more email addresses to receive alerts
* `Notification Triggers` – Select which types of events will result in email notifications (e.g., true positive finding, incident creation, keyword exposure)
* `Notification Format` – Choose between compact summary or full context (when available)

> 📌 **Note**: All emails are sent from a trusted Inopli system address. No email server or credential setup is required.

***

#### Example Use Cases

* Security analysts receive an email when a VIP is targeted in a confirmed threat
* Legal or compliance teams are alerted when a sensitive string appears in an external data source
* External partners are notified of relevant incident stages without platform access


# API

The API integration allows external systems to retrieve findings, incidents, and other security events generated by the Inopli platform. This enables seamless integration with third-party systems such as SIEMs, dashboards, GRC platforms, or custom automation workflows.

Access to the API is **read-only** and secured through a private token provided by the platform. No configuration is required on the user’s side.

***

#### How It Works

Each company receives a **private API token** generated by the Inopli platform. This token is scoped to the organization and must be included in the `Authorization` header of all API requests.

The API provides structured, RESTful endpoints for accessing:

* Confirmed findings
* Incident records
* VIP exposure data
* Asset and profile information

All requests return data in JSON format, and the platform logs all access attempts for security and auditing purposes.

***

#### Access Details

* **Token Delivery**: The token is issued by the Diazero Technologies team and delivered securely to the company
* **Rate Limiting**: Access is rate-limited per company
* **Expiration**: Tokens do not expire by default but can be manually rotated by the platform administrator upon request

> 📌 **Security Note**: This token provides access to sensitive organizational data. It must be stored securely and treated as a credential.

***

#### Example Use Cases

* Pull all true positive findings in the last 48 hours for correlation in a SIEM
* Retrieve open incidents to auto-create tickets in an ITSM platform
* Export VIP-related alerts into a GRC system for continuous risk monitoring


# Hunt

The <mark style="color:green;">**Hunt**</mark> feature in <mark style="color:green;">Inopli DRP</mark> enables users to search and investigate threat indicators across the platform’s internal intelligence base and correlated public feeds. Designed for both proactive threat hunting and reactive validation, it supports security teams in identifying malicious infrastructure, leaked assets, and suspicious behaviors across multiple dimensions.

This module provides immediate visibility into known threats and related findings, allowing analysts to trace attacker footprints, validate detection signals, and enrich investigations with contextual threat data.

***

#### Searchable Indicator Types

Hunting can be performed using the following categories:

* **IP Address** – Malicious or suspicious network indicators
* **Hash** – Known malware or leaked file signatures
* **Domain** – Phishing domains, typo-squats, and rogue infrastructure
* **Email** – Exposed, spoofed, or attacker-attributed email addresses
* **URL** – Hostnames or full links used in phishing or malware delivery
* **Username** – Aliases used in forums, dumps, or credential leaks

***

### Interface Overview

Users initiate a search by selecting the indicator type and entering the corresponding value. The Hunt engine returns results enriched with reputation signals, detection history, threat relationships, and classification.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FiIzfaBmQKxExDGPeezFz%2Fimage.png?alt=media&amp;token=84e9c1e0-6c0a-478f-827f-fe07b4eda97a" alt=""><figcaption></figcaption></figure>


# Search Results

Once a <mark style="color:green;">hunt query</mark> is executed, the <mark style="color:green;">**Results**</mark> page displays all matched threat intelligence entries based on the selected indicator and search term. The returned findings are enriched with metadata to support prioritization and further investigation.

Each result represents a correlated threat signal found within the Inopli DRP database or across integrated external sources. The system aggregates and categorizes findings to streamline triage and decision-making.

***

### Result Summary Overview

At the top of the Results screen, summary indicators are displayed:

* <mark style="color:green;">**Total Results**</mark> – Total number of matching threat records
* <mark style="color:green;">**Search Time**</mark> – Time taken to complete the query (in milliseconds)
* <mark style="color:green;">**Search Term**</mark> – The query string used during the hunt

***

### Result Table Fields

Each result row contains:

* <mark style="color:green;">**ID**</mark> – Unique incremental identifier for visual sorting
* <mark style="color:green;">**Category**</mark> – General threat category (e.g., Malware, Phishing, InfoStealer)
* <mark style="color:green;">**Type**</mark> – Specific sub-type within the category (e.g., Ransomware, Email, Domain)
* <mark style="color:green;">**Values**</mark> – IOC(s) matched against the hunt query (e.g., domain, email, hash)
* <mark style="color:green;">**Confidence**</mark> – Estimated confidence level (e.g., 85%) based on correlation signals and source reliability
* <mark style="color:green;">**UUID**</mark> – Internal unique identifier for traceability and pivoting
* <mark style="color:green;">**Threat Data**</mark> – Origin scope of the intelligence (e.g., Global, Regional, Tenant-based)

Each result can be expanded or clicked to view full details, including the source, enrichment layers, relationship graph, and timestamps.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FYWyv5SQhZlYDJWIlbfw4%2Fimage.png?alt=media&amp;token=df8e1559-70db-4183-8fbd-0b503e4481d4" alt=""><figcaption></figcaption></figure>

All search results can be <mark style="color:green;">**exported**</mark> in multiple formats to support external analysis, reporting, or archival. Supported formats include <mark style="color:green;">**CSV**</mark> for structured data handling, <mark style="color:green;">**PDF**</mark> for static reporting, and <mark style="color:green;">**HTML**</mark> for easy sharing or offline review. Exports preserve metadata such as confidence level, threat category, and UUID for traceability.


# Findings

The <mark style="color:green;">**Findings**</mark> feature represents the core output of <mark style="color:green;">Inopli DRP</mark>’s threat detection engine. Each finding is the result of active surveillance across multiple layers of the internet including surface, deep, and dark web and is produced when content is matched against elements from the organization's monitoring profile.

Monitoring inputs may include <mark style="color:green;">corporate domains, names and identifiers of VIPs, internal project names, sensitive strings, and keywords associated with infrastructure, clients, or proprietary data</mark>. Once a match is detected, it is processed through enrichment and validation routines to determine its legitimacy and severity.

Findings serve as the central intelligence object of the DRP workflow. They are not static records but dynamically enriched entities that support decision-making and escalation. Verified findings automatically integrate with the **Response** module, allowing operations teams to initiate containment, attribution, or takedown procedures when applicable.

The system ensures full traceability for each finding by associating metadata such as detection source, confidence level, enrichment context, matching rule (when applicable), and timestamps. Every finding also includes the raw evidence, which can be reviewed by analysts for verification or false positive dismissal.

***

#### Detection Categories

Findings are classified according to the source and type of exposure. The following categories are supported:

* <mark style="color:green;">**Exposed Credentials**</mark>\
  Leaked username/password pairs found in public pastes, dumps, or chat logs.
* <mark style="color:green;">**Leaked Documents**</mark>\
  Internal presentations, spreadsheets, contracts, or technical documents referencing the company’s domain or VIP names.
* <mark style="color:green;">**Cloud Bucket Exposure**</mark>\
  Files publicly accessible in cloud storage such as S3, Azure Blob, or similar, containing sensitive or proprietary content.
* <mark style="color:green;">**Phishing & Lookalike Domains**</mark>\
  Domains that imitate official company websites, including typo-squatting and phishing kits.
* <mark style="color:green;">**VIP Mentions**</mark>\
  Sensitive or malicious references to executive names or internal personnel in open or criminal forums.
* <mark style="color:green;">**Sensitive Strings Detected**</mark>\
  Predefined strings (e.g., internal project names, client references, tokens, credentials) detected in web pages, code, or chats.
* <mark style="color:green;">**Threat Actor Discussions**</mark>\
  Targeted discussions involving the brand, products, infrastructure, or VIPs in threat actor communities or deep web sources.
* <mark style="color:green;">**Code Repository Exposure**</mark>\
  Exposure of keys, tokens, employee emails, or internal comments in public Git repositories.
* <mark style="color:green;">**Dark Web Artifacts**</mark>\
  Data related to the company found in dark web marketplaces, leaks, or ransomware listings.
* <mark style="color:green;">**Clone Alerts (JS Probe)**</mark>\
  Sites that have embedded the Inopli JavaScript and were detected as clones based on unauthorized propagation.
* <mark style="color:green;">**Automated Rule Matches**</mark>\
  Findings generated from correlation rules created by analysts using Structured, XML, YARA, or Sigma detection logic.

***

#### Lifecycle

Each finding passes through the following stages:

1. <mark style="color:green;">**Ingestion**</mark> – Raw evidence is collected from open, dark, and proprietary sources.
2. <mark style="color:green;">**Correlation**</mark> – Content is matched against the company’s monitoring profile.
3. <mark style="color:green;">**Enrichment**</mark> – Metadata is added (WHOIS, DNS, internal feeds, etc.).
4. <mark style="color:green;">**Classification**</mark> – Automated severity scoring and tagging.
5. <mark style="color:green;">**Response**</mark> – If marked as a true positive, the finding triggers an incident in the **Response** module.


# Results

The <mark style="color:green;">**Results**</mark> interface displays enriched and correlated information about each monitored entitywhether it is a <mark style="color:green;">**company-level configuration**</mark><mark style="color:green;">, a specific</mark> <mark style="color:green;"></mark><mark style="color:green;">**VIP**</mark><mark style="color:green;">, a</mark> <mark style="color:green;"></mark><mark style="color:green;">**sensitive string**</mark><mark style="color:green;">, or a</mark> <mark style="color:green;"></mark><mark style="color:green;">**domain**</mark>. This is the primary view for analysts to investigate entity-level exposure and track all findings linked to that asset across surface, deep, and dark sources.

Each record consolidates contextual metadata, historical findings, enrichment details, and automation outputs. Analysts can use this interface to monitor ongoing exposure, review detection history, and evaluate risk signals tied to the selected entity.

***

#### Sections per Entity Type

* <mark style="color:green;">**Company Profile Results**</mark>\
  Displays the company name, tax identifiers, social media handles, and configured monitoring profile. Shows a chronological list of all findings that matched any item from the company configuration, including domain-based leaks, impersonations, and VIP exposures.
* <mark style="color:green;">**VIP Results**</mark>\
  For each registered VIP (executive, stakeholder, or key individual), this section presents their identifiers, aliases, and custom metadata. Findings are grouped by type (e.g., mentions, credential leaks, impersonation attempts), with timeline and severity indicators.
* <mark style="color:green;">**Sensitive String Results**</mark>\
  Lists each configured keyword, tag, or expression, along with matches detected across monitored sources. Results include context snippets, source links, and whether the string was found in code, documents, or threat actor discussions.
* <mark style="color:green;">**Domain Results**</mark>\
  Displays all findings associated with the domain, including leaked documents, phishing lookalikes, code repository exposures, and clone detections from the JS monitoring probe. The view also includes domain enrichment (WHOIS, DNS records, certificate transparency, etc.).

***

#### Available Data Points

Each result includes:

* <mark style="color:green;">**Enriched metadata**</mark> (source, first seen, last seen, risk level, matched pattern)
* <mark style="color:green;">**Finding preview**</mark> (summary, evidence type, threat category)
* <mark style="color:green;">**Linked incidents**</mark> (if the finding triggered a response case)
* <mark style="color:green;">**Automated rule matches**</mark> (if any structured rule matched the entity)
* <mark style="color:green;">**Tags and classification**</mark> (automatically assigned by the DRP engine)
* <mark style="color:green;">**Visual timeline**</mark> (showing recurrence and frequency of exposure)

***

#### Exports

Results for each entity can be **exported** in <mark style="color:green;">**CSV**</mark><mark style="color:green;">,</mark> <mark style="color:green;"></mark><mark style="color:green;">**PDF**</mark><mark style="color:green;">, or</mark> <mark style="color:green;"></mark><mark style="color:green;">**HTML**</mark> format to support audits, reporting, or integration with external systems. Exports preserve all metadata and finding references for traceability.


# Advanced Features


# Automatic Search Rules

<mark style="color:green;">**Automatic Search Rules**</mark> allow security teams to define and deploy custom correlation logic that continuously monitors the <mark style="color:green;">Inopli DRP</mark> dataset for matching patterns, indicators, or behaviors. These rules operate on top of the internal threat intelligence index and can proactively trigger incidents without requiring manual validation.

When a rule matches a new entry, whether it's a domain, string, IOC, or correlation pattern the system automatically escalates it to the <mark style="color:green;">**Response**</mark> module, where an incident is created with full context and enrichment.

This feature is designed to reduce reaction time, automate repetitive detection tasks, and encode organizational threat models into reusable and auditable rules.

***

### Rule Types

Inopli supports three types of rule syntaxes, each suited to different detection needs:

* <mark style="color:green;">**Structured Query Rules**</mark>\
  Human-readable logic designed for analysts to define conditional search patterns based on values, fields, and Boolean logic.
* <mark style="color:green;">**YARA Rules**</mark>\
  Used for defining byte-level or string-level conditions. These rules support <mark style="color:green;">**regular expressions (regex)**</mark> for advanced matching of malware signatures, credential formats, file patterns, or encoded strings. Regex enables the detection of complex obfuscation techniques or variable content structure in payloads.
* <mark style="color:green;">**XML Match Rules**</mark>\
  Designed to match specific tags, attributes, or values in structured XML content. These rules also support <mark style="color:green;">**regex**</mark> within node values or attribute conditions, allowing flexible pattern recognition in feeds, form submissions, or structured artifacts.
* <mark style="color:green;">**Sigma Detection Rules**</mark>\
  YAML-based rules inspired by the Sigma standard, allowing analysts to write abstract, backend-agnostic detection logic. <mark style="color:green;">Inopli</mark> parses these rules and translates them into native queries over the DRP dataset. This format is especially useful for expressing multi-field correlation patterns and structured IOC detections.

***

### Detection & Escalation Flow

1. The analyst defines a rule and saves it in the rule engine.
2. The engine continuously scans new DRP entries in real-time.
3. When a match is found, it is enriched and validated.
4. If thresholds or severity conditions are met, an incident is automatically created in the **Response** module.

***

**Pages in this section:**

* [Structured Query Rules](/drp/advanced-features/automatic-search-rules/structured-query-rules)
* [YARA Rules](/drp/advanced-features/automatic-search-rules/yara)
* [XML Match Rules](/drp/advanced-features/automatic-search-rules/xml)
* [SIGMA Rules](/drp/advanced-features/automatic-search-rules/sigma)


# Structured Query Rules

<mark style="color:green;">**Structured Query Rules**</mark> allow analysts to define custom detection logic using a readable query syntax that filters and correlates threat signals based on field values, Boolean conditions, and pattern matches. This format is ideal for teams that want to express precise conditions over the normalized threat intelligence dataset without relying on low-level syntax.

These rules operate continuously over incoming findings within the DRP module and are capable of triggering automated incidents in the Response module when a match is detected.

***

### Rule Syntax Overview

Structured Query Rules support logical operators, field-based filters, and nested conditions. Supported constructs include:

* <mark style="color:green;">Field equality</mark>:\
  `type = "domain"`
* <mark style="color:green;">String containment</mark>:\
  `value contains "gov.br"`
* <mark style="color:green;">Lists and sets</mark>:\
  `category in ["phishing", "malware"]`
* <mark style="color:green;">Boolean logic</mark>:\
  `type = "email" AND confidence >= 80 AND threat_data = "public"`
* <mark style="color:green;">Negation</mark>:\
  `NOT type = "hash"`

***

### Use Cases

Some examples of how Structured Query Rules can be used:

* Detect newly registered `.zip` domains with medium or high risk:\
  `value endswith ".zip" AND risk_level in ["medium", "high"]`
* Match credentials leaked from specific business units:\
  `value contains "@diazero.com" AND department = "Finance"`
* Flag phishing emails targeting executives:\
  `type = "email" AND target_group = "executive" AND category = "phishing"`

***

### Rule Behavior

Once a rule is saved and enabled, it will run in real-time against all new entries ingested by the <mark style="color:green;">DRP engine</mark>. If a match is found, the result is enriched, validated, and, if eligible, escalated as an incident in the **Response** module.

***

To create a new rule, users can access the <mark style="color:green;">**Structured Rule Editor**</mark> via the platform’s interface. This editor supports live syntax validation and preview of matching entries.


# YARA

<mark style="color:green;">**YARA Rules**</mark> allow analysts to define pattern-based detection logic using string matching and binary-level conditions. Originally designed for malware classification, YARA is also highly effective for detecting suspicious strings, tokens, and structural markers in exposed content within the Inopli DRP dataset.

YARA rules operate continuously on findings involving <mark style="color:green;">text bodies, source code, cloud storage leaks, and other artifacts</mark> where content analysis is meaningful.

***

### Rule Structure

A basic YARA rule consists of three main sections:

* <mark style="color:green;">**Meta**</mark> (optional)\
  Contains descriptive fields like `author`, `description`, or `severity`
* <mark style="color:green;">**Strings**</mark>\
  Defines patterns to match, including plaintext strings, hexadecimal byte patterns, or **r**<mark style="color:green;">**egular expressions (regex)**</mark>
* <mark style="color:green;">**Condition**</mark>\
  Boolean logic that defines when the rule should trigger

### Regex Support

YARA natively supports <mark style="color:green;">**regular expressions**</mark> using the `/regex/` syntax within the `strings` section. This enables analysts to detect:

* Obfuscated credentials
* Token formats (e.g., JWT, OAuth, API keys)
* File path structures
* Encoded indicators like Base64 or hex

Regex can be combined with modifiers like `nocase`, `wide`, or `ascii` to refine detection logic.

***

#### Use Cases

* Detect password patterns in HTML or JS sources
* Identify obfuscated malware strings in leaked ZIPs
* Flag exposure of client secrets in public cloud storage
* Match encoded backdoor calls in script-based payloads

***

### Incident Triggering

Once a YARA rule matches content in a DRP finding, the result is automatically enriched. If classified as a threat based on rule severity or context, it triggers an <mark style="color:green;">**incident in the Response module**</mark> for operational follow-up.


# XML

<mark style="color:green;">**XML Match Rules**</mark> are designed for detecting threats or patterns within structured data sources that use XML formatting. This rule type is ideal for processing feeds, form submissions, third-party alerts, and content with hierarchical tagging such as threat reports, leak disclosures, or machine-readable submissions.

These rules allow analysts to define precise conditions over specific XML nodes, attributes, or values. They support <mark style="color:green;">**regular expressions (regex)**</mark> for flexible pattern matching within content and provide fine-grained control over structured data inspection.

***

### Rule Structure

Each XML rule includes:

* <mark style="color:green;">**Target Element(s)**</mark>\
  The XML node or attribute to inspect (e.g., `<email>`, `<domain>`, `@type`)
* <mark style="color:green;">**Condition**</mark>\
  Logic defining what should be matched. Conditions can include:
  * Exact value match
  * Partial string match
  * **Regex match**
* <mark style="color:green;">**Severity**</mark>\
  Optional impact classification (`low`, `medium`, `high`)

### Regex Support

Regex can be used to:

* Identify email domains, credential patterns, or encoded values
* Detect naming conventions in tags or attributes
* Match variations in formatting across data sources

Regex is defined inside `<condition>` and supports common expressions such as:

```xml
<rule>
  <condition regex=".*unauthorized\s+access.*" />
  <severity>high</severity>
</rule>
```

***

### Use Cases

* Flag indicators in external CTI feeds
* Match credentials or tokens in structured breach dumps
* Detect abuse types in standardized incident formats (e.g., STIX, TAXII)
* Monitor custom fields in partner submissions or open disclosure reports

***

### Incident Triggering

When an XML Match Rule finds a match in newly ingested structured content, the result is classified and enriched. If it meets the predefined criteria, it triggers an <mark style="color:green;">**incident in the Response module**</mark> automatically.


# SIGMA

<mark style="color:green;">**Sigma Detection Rules**</mark> bring a flexible and standardized way to define detection logic using YAML-based structures. Inspired by the open Sigma format but adapted to Inopli’s internal data model, these rules allow analysts to describe correlations and matching conditions in a clear, human-readable form that abstracts away backend query language dependencies.

This rule type is especially useful for analysts familiar with SOC practices or SIEM rule writing, enabling fast onboarding and reusable logic across clients and use cases.

***

### Rule Structure

Each Sigma rule is written in **YAML format** and includes:

* <mark style="color:green;">**Metadata**</mark>\
  Descriptive fields like `title`, `id`, `description`, `status`, `level`, `tags`, and `author`
* <mark style="color:green;">**Detection Logic**</mark>\
  Conditions are expressed using field-value maps, lists, and logical operators. Inopli supports `selection`, `filter`, `condition` blocks.
* <mark style="color:green;">**Trigger Definition**</mark>\
  Conditions evaluate the presence of fields or values in the DRP dataset. When a rule is matched, it is escalated following the defined severity level.

Example:

```yaml
yamlCopiarEditartitle: Suspicious domain with sensitive keyword
id: 8c7a-fake-1234-5678
status: stable
description: Detects domains containing sensitive internal keywords
level: medium
author: drp.team@inopli.com

detection:
  selection:
    type: domain
    value|contains: "internal"
  condition: selection
```

***

### Detection Model

Sigma rules are translated internally into structured queries compatible with Inopli’s data engine. They can be applied over:

* IOCs (domain, IP, hash, email)
* Content fields (value, description, source, category)
* Context metadata (tenant, risk level, enrichment tags)

All supported operators include:

* Exact match
* `contains`, `startswith`, `endswith`
* Lists (`field: ["a", "b"]`)
* Field modifiers (`value|contains`)

***

### Use Cases

* Match known IOCs from shared threat intelligence
* Detect exposure of internal identifiers or keywords
* Alert on findings linked to specific attack techniques
* Build reusable rules for sector-specific monitoring

***

### Incident Triggering

Once matched, Sigma rules follow the same workflow as other rule types: they enrich the finding and, if not filtered as false positive, **trigger an&#x20;**<mark style="color:green;">**incident in the Response module**</mark>.


# Overview

The <mark style="color:green;">RPA module</mark> in Inopli provides a centralized and visual environment for orchestrating automated actions in response to security events, repetitive tasks, and operational workflows. Built with flexibility and scalability in mind, it empowers <mark style="color:green;">SOC teams</mark> to define playbooks using a no-code editor, reducing response time and human intervention.

This section introduces the core components of the RPA module, organized into distinct functional areas that work together to enable automation at every level of security operations:

***

* <mark style="color:green;">**Automations**</mark>\
  Full workflow definitions executed based on triggers such as timers, detection rules, or analyst actions. Each automation can contain branching logic, error handling, and multi-step processing. There is no limit to the number of playbooks that can be created, allowing the SOC team to automate both recurring processes and complex incident responses without restriction.
* <mark style="color:green;">**Components**</mark>\
  Reusable building blocks used inside automations. These are modular actions or sequences that can be shared across different workflows to ensure consistency and reduce duplication.
* <mark style="color:green;">**Integrations**</mark>\
  This area manages all third-party connections used by the playbooks. Inopli RPA supports a growing library of connectors, with dozens of native integrations available out-of-the-box. Whether connecting to SIEM platforms, messaging tools, ticketing systems, or cloud providers, each integration is configurable and can be used in multiple automation flows simultaneously.
* <mark style="color:green;">**Appliances**</mark>\
  Remote execution units for running automations in isolated or controlled environments. These are typically used when actions must occur in segmented networks or require direct access to internal infrastructure.
* <mark style="color:green;">**Tasks**</mark>\
  A kanban-style monitoring interface showing the current state of every automation task, grouped into categories such as inactive, pending, running, failed, and successful. This area gives visibility into execution flow and allows analysts to audit task lifecycles and outcomes.
* <mark style="color:green;">**Dashboard**</mark>\
  A visual hub summarizing the overall status of the automation framework. It includes real-time insights into automation coverage, task success rates, component health, and new custom logic or knowledge deployed by the team.

<mark style="color:green;">Inopli RPA</mark> is built to support enterprise-scale automation, allowing SOCs to create and manage hundreds or thousands of workflows without architectural limitations. The modular design, deep integration capabilities, and visual flow editor make it possible to rapidly deploy new automations and adjust existing ones as threats and operational demands evolve.


# Integrations

The <mark style="color:green;">**Integrations**</mark> section of the <mark style="color:green;">Inopli RPA</mark> module provides a robust and extensible framework for connecting with third-party platforms, internal systems, cloud services, security tools, and external APIs. This integration layer is essential for executing automated actions across the security ecosystem during playbook execution.

Each integration is implemented as a **connector** that can be customized and reused across multiple workflows. These connectors support granular configurations, including credentials, endpoint mappings, API keys, headers, and response handling, ensuring secure and efficient interaction with the external system.

Currently, Inopli supports over **200 native connectors**, enabling comprehensive orchestration and automation across a wide range of use cases such as ticket creation, enrichment, threat hunting, alerting, asset isolation, and more.

***

### &#x20;Available Connectors

* **Security Tools & EDR**
  * CrowdStrike Falcon
  * SentinelOne
  * Microsoft Defender ATP
  * Carbon Black Cloud
  * Cynet
  * Trend Micro Vision One
* **Threat Intelligence & Enrichment**
  * VirusTotal
  * URLVoid
  * Talos ThreatSource
  * AbuseIPDB
  * Recorded Future
  * DomainTools
  * ThreatQ
  * Shodan
  * JoeSandbox
* **Email & Collaboration**
  * Microsoft Teams
  * Slack
  * Exchange
  * Mimecast
  * Cisco Email Security
  * Twilio
* **Ticketing & ITSM**
  * Jira
  * ServiceNow
  * BMC Remedy
  * Freshservice
  * SysAid
  * ConnectWise
* **Cloud & Infrastructure**
  * AWS EC2, IAM, S3, GuardDuty, Security Hub
  * Azure AD, Security Center
  * Google Cloud API, Armor, Pub/Sub
  * Docker, Kubernetes, VSphere
* **SIEM & Logging**
  * Splunk
  * ElasticSearch
  * Azure Sentinel
  * QRadar
  * ArcSight
  * Devo
  * Exabeam
* **Vulnerability Management**
  * Nessus
  * Tenable.io
  * Orca Security
  * Qualys (via HTTP API)
* **Data Sources & DBs**
  * MongoDB
  * PostgreSQL
  * MSSQL
  * MySQL
  * Redis
* **Other Utilities**
  * SSH
  * WMI
  * REST API
  * CSV / JSON input
  * Custom HTTP v2

***

New connectors are added regularly, and custom connectors can be developed using Python. This allows teams to integrate with internal systems or proprietary APIs when required.


# Dashboard

The <mark style="color:green;">**Dashboard**</mark> <mark style="color:green;"></mark><mark style="color:green;">pag</mark>e of the <mark style="color:green;">Inopli RPA</mark> module serves as the central monitoring interface for all core areas of automation activity. Through an intuitive and visually engaging layout, it provides a high-level overview of the operational state of each key category **Automations**, **Tasks**, **Knowledge**, and **Customizations** allowing teams to instantly assess system health, execution status, and areas requiring attention.

***

### **Purpose and Design**

* <mark style="color:green;">**Visual Summary of Automation Ecosystem**</mark>\
  The dashboard presents a circuit-brain layout with interconnected nodes representing major functional areas. Each node displays a summary status (e.g., Complete, Error, New) with contextual messages to indicate ongoing operations or issues.
* <mark style="color:green;">**Status Indicators**</mark>\
  Color-coded signals (green, red, blue) quickly communicate the current state of executions or configurations, helping operators identify successful completions, recent updates, or errors in need of intervention.
* <mark style="color:green;">**Categorical Drilldown Access**</mark>\
  Each dashboard section links directly to its corresponding feature page—such as **Tasks**, **Automations**, or **Knowledge**—enabling a seamless workflow from high-level monitoring to granular configuration or review

***

This centralized view is particularly useful for large environments where multiple automations, tasks, and knowledge resources are actively maintained and executed.


# Automations

The <mark style="color:green;">**Automations**</mark> feature of the <mark style="color:green;">Inopli RPA</mark> module is where <mark style="color:green;">incident response and operational workflows</mark> are transformed into structured, repeatable, and fully automated processes. At its core, this feature allows organizations to create and manage <mark style="color:green;">**an unlimited number of playbooks**</mark>, each representing a complete automation flow tailored to a specific detection, incident, or business requirement.

***

### Key Capabilities

* <mark style="color:green;">**Visual Workflow Builder**</mark>\
  Analysts can build complex routines using a <mark style="color:green;">**graphical no-code editor**</mark>, enabling them to model processes without needing to write or modify code. Each playbook is structured as a visual canvas of connected actions and decision nodes, supporting conditional logic, parallel execution, retries, and customized transitions between stages.
* <mark style="color:green;">**Ready-to-Use and Customizable Templates**</mark>\
  The system includes <mark style="color:green;">**preconfigured playbook templates**</mark> designed to address common security operations tasks. These templates can be adapted or new ones created from scratch, supporting use cases ranging from incident triage and escalation to enforcement and documentation workflows.
* <mark style="color:green;">**Integrated Execution Logic**</mark>\
  Playbooks can react automatically to detection events, specific triggers, or scheduled intervals. Automated actions can include asset isolation, enrichment queries, ticket generation, policy application, or communication with third-party platforms, all performed without human intervention unless configured otherwise.
* <mark style="color:green;">**Form-Based Configuration**</mark>\
  For each automation, users can define <mark style="color:green;">**custom forms**</mark> to guide execution and input collection, allowing context-specific controls and structured decision-making criteria, all managed directly through the interface.

***

### Monitoring and Reporting

* <mark style="color:green;">**Operational Dashboards**</mark>\
  Real-time dashboards offer a centralized view of automation performance. Analysts can track executions, error states, timings, and the outcome of each step, ensuring transparency and operational oversight.
* <mark style="color:green;">**Scheduled Reporting**</mark>\
  The module supports <mark style="color:green;">**automatic and scheduled delivery of executive and operational reports**</mark>, configured per playbook, user group, or organizational unit. Reports are available in various formats and include graphical insights on workflow activity, effectiveness, and exceptions.

***

### Process Control and Auditing

* <mark style="color:green;">**Standardization and Oversight**</mark>\
  Playbooks can embed approval steps, checkpoints, and branching logic aligned with internal governance and response protocols. Each automation step is fully auditable, supporting compliance and post-incident reviews.
* <mark style="color:green;">**Built-in Validation Mechanisms**</mark>\
  Automation flows can incorporate <mark style="color:green;">**status verification routines**</mark>, cross-system checks, and correlation conditions to ensure that each action aligns with security and business requirements.

***

The image below illustrates the Inopli automation builder, showcasing how analysts define multi-step workflows visually, with full access to actions, conditions, and integrations configured within the platform.

<figure><img src="https://2621223932-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FLTQJomzpe5BTzHSLQPAt%2Fuploads%2FtAB9LJKA0ozUsyG2A5aM%2Fimage.png?alt=media&amp;token=78bea196-86dc-4922-a511-9ef91138a329" alt=""><figcaption></figcaption></figure>


# Components

The <mark style="color:green;">**Components**</mark> <mark style="color:green;"></mark><mark style="color:green;">feature</mark> of the Inopli RPA module enables the creation of <mark style="color:green;">**reusable automation blocks**</mark>, encapsulating logic, conditions, and actions into modular units. These components act as micro-playbooks that can be referenced across multiple larger automation workflows, ensuring consistency, efficiency, and simplified maintenance.

***

### Purpose and Design

* <mark style="color:green;">**Encapsulated Logic**</mark>\
  Each component is built to perform a specific function such as enriching data, validating inputs, triggering notifications, or interacting with third-party systems. Once created, the component behaves as a **self-contained automation object**, with its own input/output structure and execution context.
* <mark style="color:green;">**Drag-and-Drop Integration**</mark>\
  Components are available directly within the <mark style="color:green;">**visual automation builder**</mark>, where they can be dragged into larger playbooks and reused across various steps and branches without the need to redefine their logic.
* <mark style="color:green;">**Parametrization and Input Binding**</mark>\
  Each component can accept <mark style="color:green;">**dynamic parameters**</mark> at runtime, making them adaptable to different scenarios. Inputs and outputs are clearly defined, enabling clean interfacing with other playbook elements.

***

### Benefits

* <mark style="color:green;">**Reusability Across Automations**</mark>\
  By modularizing recurring logic into components, teams reduce duplication and improve scalability. A single update to a component reflects across every automation that uses it, streamlining change management.
* <mark style="color:green;">**Faster Playbook Assembly**</mark>\
  Analysts can rapidly assemble new automations using a growing library of existing components, focusing on business logic instead of low-level implementation details.
* <mark style="color:green;">**Operational Consistency**</mark>\
  Components enforce <mark style="color:green;">**standardization of procedures**</mark>, ensuring that critical actions (like asset tagging, email notifications, or escalation triggers) follow approved, centrally managed workflows.


# Tasks

The <mark style="color:green;">**Tasks**</mark> <mark style="color:green;"></mark><mark style="color:green;">section</mark> within the <mark style="color:green;">Inopli RPA</mark> module serves as a <mark style="color:green;">**dedicated environment for managing and automating daily SOC routines**</mark>, combining operational visibility with workflow-based automation. Presented in a <mark style="color:green;">**kanban-style interface**</mark>, this feature is designed to streamline recurring analyst activities through structured task flows and automated execution.

***

### Operational Flow

* <mark style="color:green;">**Predefined Columns**</mark>\
  The task board follows a fixed column structure: *<mark style="color:green;">Backlog</mark>*<mark style="color:green;">,</mark> <mark style="color:green;"></mark>*<mark style="color:green;">To Do</mark>*<mark style="color:green;">,</mark> <mark style="color:green;"></mark>*<mark style="color:green;">In Progress</mark>*<mark style="color:green;">,</mark> <mark style="color:green;"></mark>*<mark style="color:green;">Under Review</mark>*<mark style="color:green;">, and</mark> <mark style="color:green;"></mark>*<mark style="color:green;">Done</mark>*. This standardization ensures alignment across teams and supports consistent operational reporting.
* <mark style="color:green;">**Card-Based Automation**</mark>\
  Each task card has it's own <mark style="color:green;">**dedicated automation workflow**</mark>, allowing routine actions such as notifications, data validation, ticket creation, or escalation to be executed automatically when the task progresses. The workflow is fully visual and built with the same no-code interface used in the main Automations module.
* <mark style="color:green;">**Recurring and Triggered Tasks**</mark>\
  Teams can schedule <mark style="color:green;">**recurring task**</mark>**s** (e.g., daily log checks, threat feed reviews) .

***

### Designed for SOC Operations

* <mark style="color:green;">**SOC-Centric Templates**</mark>\
  The module includes task templates for <mark style="color:green;">**routine SOC activities**</mark> including shift handovers, IOC hunting, asset verifications, and healthchecks enabling fast setup and standardized execution.
* <mark style="color:green;">**Status Tracking and SLAs**</mark>\
  Each task can carry metadata like <mark style="color:green;">**priority, deadline, SLA**</mark>, and assignment to specific analysts. The system tracks progress and flags overdue or blocked tasks automatically.
* <mark style="color:green;">**Integrated Audit Trail**</mark>\
  All task actions and transitions are logged and auditable, ensuring compliance with internal operational procedures and facilitating post-incident reviews.


# Appliances

The <mark style="color:green;">**Appliances**</mark> <mark style="color:green;"></mark><mark style="color:green;">section</mark> of the <mark style="color:green;">Inopli RPA</mark> module provides full lifecycle management for <mark style="color:green;">**virtual execution environments**</mark>, enabling the distribution of automation workloads across physical servers or cloud-based infrastructures. Each appliance acts as a remote executor for playbooks, tasks, and integrations.

***

### Overview

* <mark style="color:green;">**Virtual Appliance Deployment**</mark>\
  Appliances are provisioned using <mark style="color:green;">**Docker-based images**</mark>, ensuring consistent and lightweight deployments across heterogeneous environments. Installation can be performed on bare-metal servers, virtual machines, or public cloud instances.
* <mark style="color:green;">**Unlimited Scaling**</mark>\
  There is <mark style="color:green;">**no limit to the number of appliances**</mark> that can be registered. Organizations are free to create as many as needed to support distributed automation, high availability, or multi-region operations.
* <mark style="color:green;">**Centralized Control**</mark>\
  All appliances are managed centrally within the Inopli interface. Admins can register, monitor, and remove appliances at any time, with visibility into their operational status and assigned workloads.

***

### Use Cases

* <mark style="color:green;">**Distributed Execution**</mark>\
  Appliances can be installed <mark style="color:green;">**close to the data or systems they need to interact with**</mark>, reducing latency for sensitive automations (e.g., internal AD changes, on-premises security controls).
* <mark style="color:green;">**Workload Isolation**</mark>\
  Different appliances can be dedicated to specific workflows, tenants, or departments — providing <mark style="color:green;">**logical and operational separation**</mark> where needed.
* <mark style="color:green;">**Cloud-Native or On-Prem Ready**</mark>\
  Whether deployed in a <mark style="color:green;">**Kubernetes cluster**</mark>, a <mark style="color:green;">**cloud VM**</mark>, or an <mark style="color:green;">**on-premises appliance**</mark>, the setup process remains the same, using containerized infrastructure with minimal prerequisites.


---

[Next Page](https://docs.inopli.com/llms-full.txt/1)